Kapālins for Azure Monitor
Azure OpenAI request logs, Azure AI Foundry audit logs and Microsoft 365 Copilot activity held in a Log Analytics workspace. Azure Monitor runs its AI on its own side, where no gateway can sit. Kapālins reads the Azure Log Analytics REST API (AzureDiagnostics, AIAuditLogs and OfficeActivity tables) and puts every event in the same timeline, rules and evidence chain as the rest of your estate.

See what no gateway sees
Azure Monitor’s own logs are the only record of how its AI is used. Kapālins is where that record meets everything else.
A risky action becomes an incident
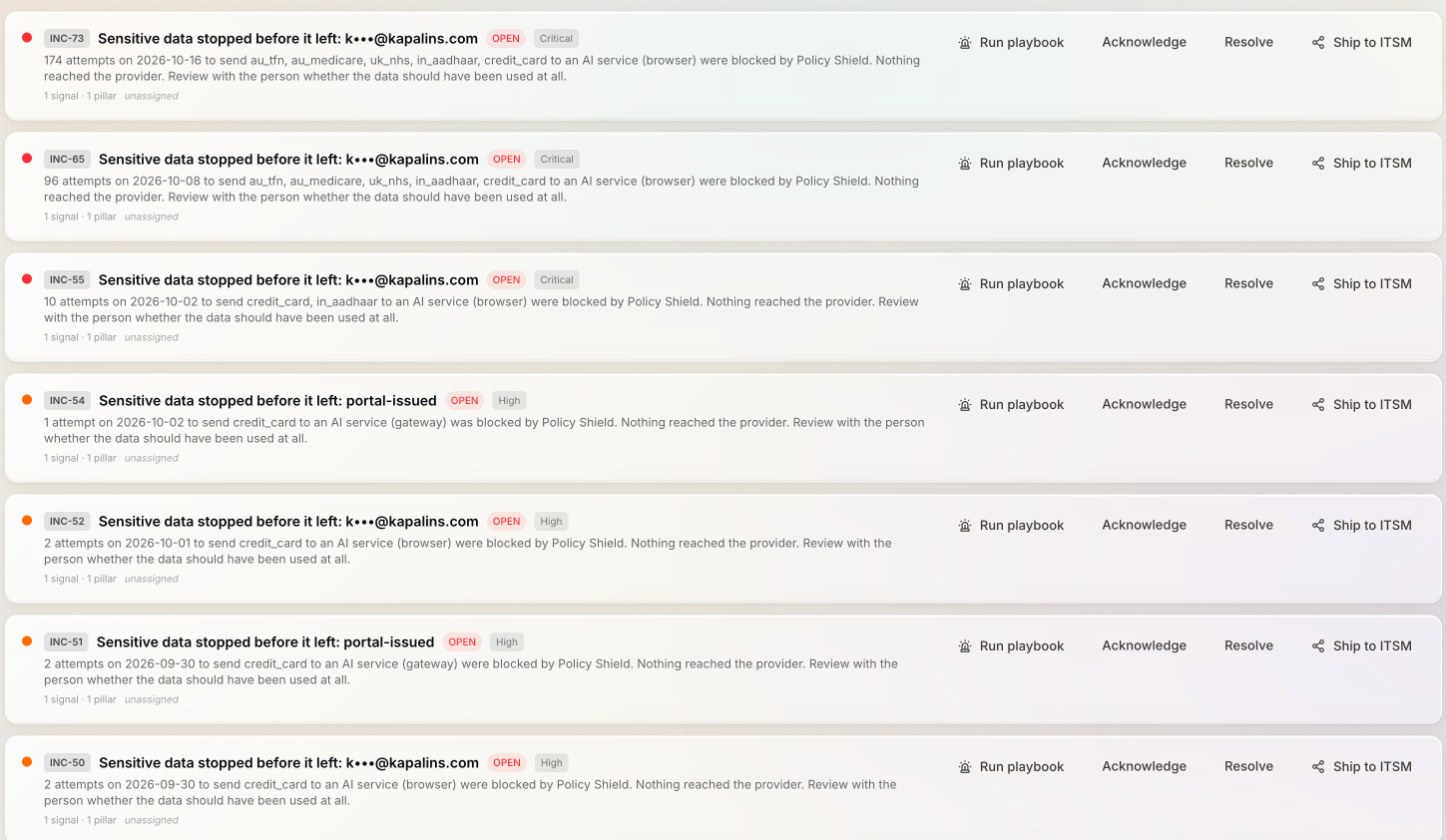
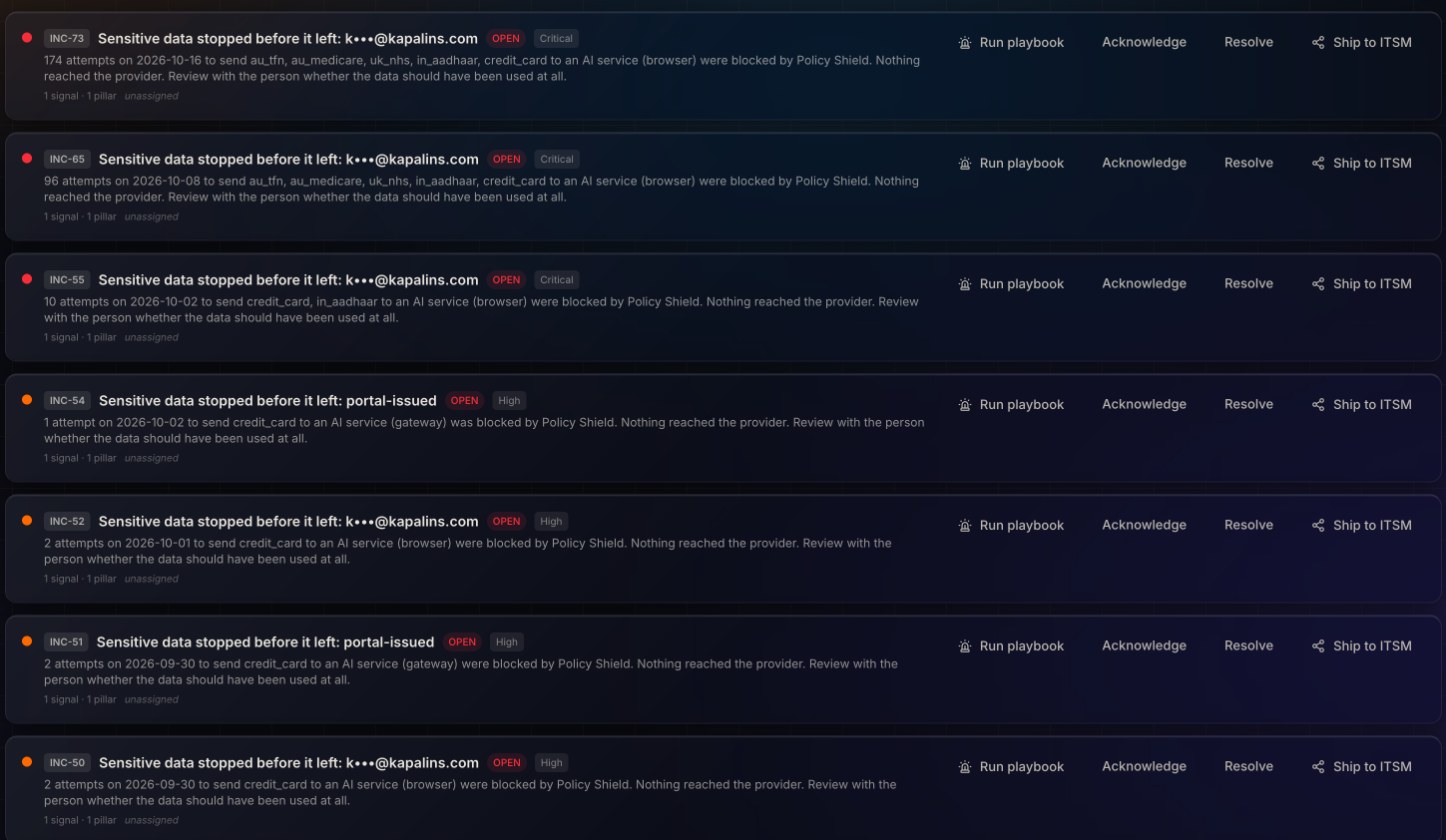
The same detection rules as the gateway run on every Azure Monitor event, and a finding opens one incident card your SOC already triages.
Evidence an auditor accepts
Each event is attributed to a person and kept with the raw source record, inside the evidence pack.
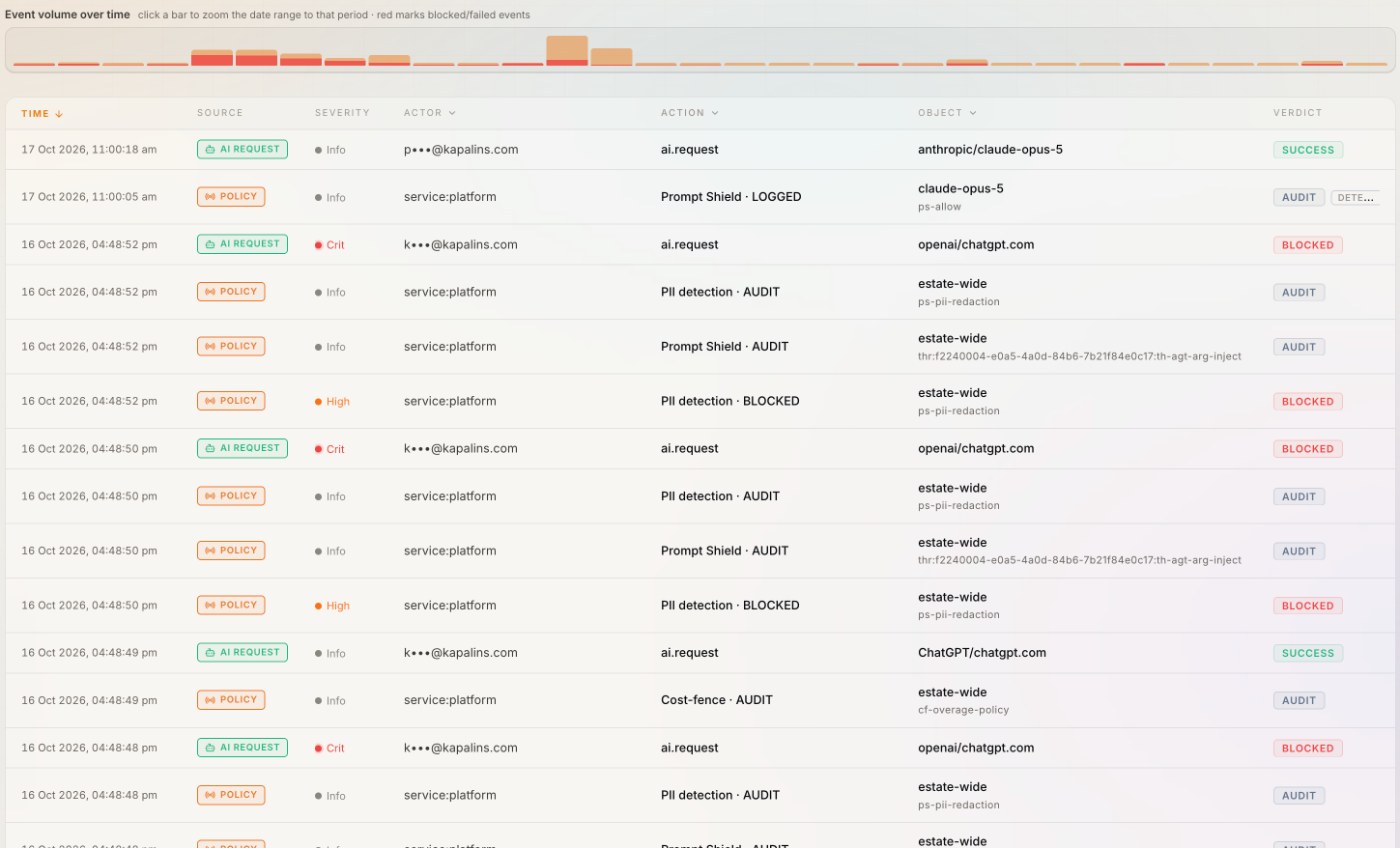
Azure Monitor in the same timeline as everything else.
Kapālins reads the Azure Log Analytics REST API (AzureDiagnostics, AIAuditLogs and OfficeActivity tables) every 15 minutes, turns each record into one event shape, and attributes it to a person from your directory.
- A high-water mark, so nothing is read twice or skipped
- The raw record kept exactly as it arrived
- Source label "Azure Monitor" on every row
A finding, not a log line.
Rule families and custom checks run on Azure Monitor events after the fact. What matters opens an incident with the person, the rule and the evidence, and is pushed to your SIEM or ITSM.
- Mute, risk-accept or escalate from the card
- Notification clocks start when an incident is reportable
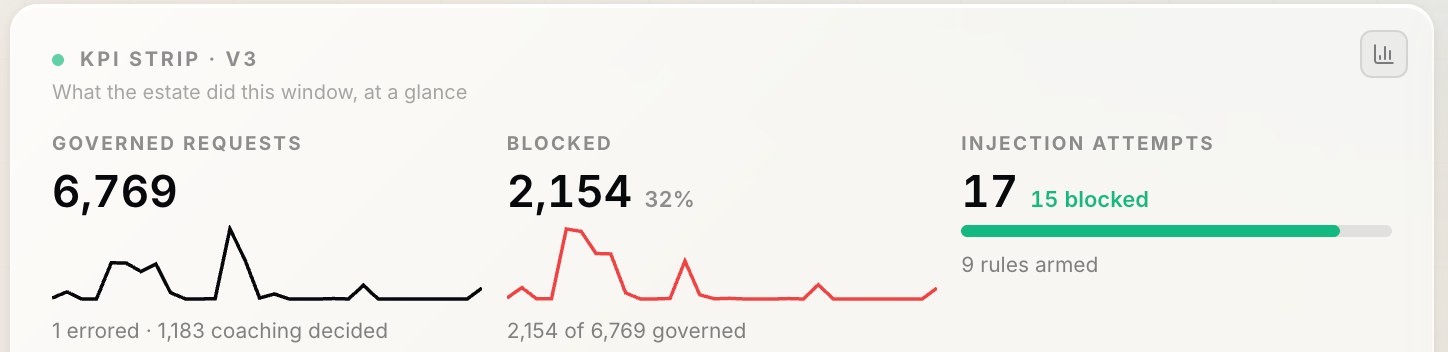
Counted in the number the board reads.
Azure Monitor activity feeds the AI Trust Index and the compliance obligations it proves, so it is governed rather than exempted.
- Obligation, control, artifact, verification in one chain
Four steps.
- Grant a read credentialAn Entra application with read access to the workspace.
- Paste it in KapālinsIntegrations › Azure Monitor › Create. A live read validates it before anything is stored.
- Watch the first sweepLogs shows each event with its source, the person and the rules that fired.
- Tune the rulesMute, risk-accept or escalate from the incident card.
See Azure Monitor governed in thirty minutes.
Bring the person who holds the credential. We connect it live and watch the first events land.
Questions buyers ask.
Does Kapālins change anything in Azure Monitor?
No. The connector reads with the credential you grant, or receives what the platform pushes. Nothing is written back.
How current is the timeline?
Pulled sources are swept every 15 minutes; pushed sources arrive as they happen. Each window overlaps the last, so a late record is caught next time.
Where is the credential kept?
Encrypted at rest with AES-256-GCM, decrypted only inside the ingestion job and the connect-time validation, never returned to the browser or written to a log.