Kapālins for Claude
Every way your enterprise uses Claude — claude.ai, Cowork, Claude Code, the Claude API, Bedrock, Vertex AI and Foundry, Microsoft 365 and Slack — through the same eight layers of Kapālins: identity, data, threat, agents, MCP, model control, visibility and evidence.
Looking for claude.ai, Cowork or Claude Code? The Claude Enterprise integration
Every route to Claude rises through eight layers of Kapālins.
claude.ai and the desktop app, Cowork, Claude Code, your apps on the Claude API, Bedrock, Vertex AI and Foundry, Microsoft 365 and Slack: each passes the same eight layers. Inline where Claude lets a check stand in the path, through the gateway where your apps call it, and from Claude’s Compliance API for the record.
Delete the inline hook, or switch off single sign-on in your Claude organisation, and a critical incident opens at the next check.
Try it: Claude Enterprise →Claude Code asks Kapālins before every command and tool call. A risky one waits for a person, with the reason.
Try it: run a command that reads .env →Claude Code on a laptop, a script with its own Claude key, a personal claude.ai account: found where it runs, not where it was registered.
Try it: Shadow AI → Claude →Add the Kapālins connector and Claude reads your incidents, integrity ratings and policy, signed in as you. It changes nothing.
Try it: add the connector →Claude across the business, without the week-one surprises.
Five things every security team discovers the week Claude rolls out, and what changes with Kapālins.
Customer records in prompts
Card numbers and national IDs go to Claude with nobody aware.
Card numbers held back before they left, this week on our demo organisation.
Personal accounts at work
Nobody can say which personal AI accounts are in use.
Personal-account AI tools found across 51 tools in use, counted, never named.
Coding agents with full reach
Agents run commands and edit files without anyone asking.
Tool calls checked in 7 days; risky ones wait for a person.
Controls switched off
A deleted hook or disabled SSO goes unnoticed until the audit.
Raised at the next check, with the change in one timeline.
“Where are we on AI risk?”
Figures pulled from tool after tool for every board pack.
Asked in Claude, answered from your own data: Trust Index 73, Good.
 Same Claude. Same people. You just can’t see or prove anything.
Five control points. Every Claude surface. Nothing for your people to change.
Your people keep using Claude the way they do today. Kapālins sits at the five points where control matters, before, around, inside and after Claude, and every one of them runs on the same policy and the same record.
 One policy · one record · evidence for 43 frameworksthe same rules at every control point
Control points 3 and 4 work with a Claude Enterprise organisation. Figures: our demo organisation, last 7 days, read on 9 November 2026.
Your AI risk briefing, one question away.
The Kapālins connector lets Claude read your organisation’s posture as the person asking: the same figures as the console, a link to each, and nothing Claude can change.
ClaudeKapālins connectedHere is your organisation this week, from Kapālins:
A Claude security practice you can offer every client.
Each client organisation switches it on for its own people and gets the controls its plan includes. Your consultants hand regulators evidence, not opinions.
More Claude, in the organisations that say no today.
In regulated organisations, a Claude rollout waits on one question: can we control it and prove it? Kapālins answers it on every Claude surface, using the interfaces Anthropic publishes.
Built on Anthropic’s published interfaces. An integration, not an Anthropic product.
Data leaving, shadow use, agent reach and evidence, each met with a working control rather than a policy document.
claude.ai, Desktop, Claude Code, Cowork, Chrome, Microsoft 365, Slack, the API and the clouds.
43 frameworks, including 13 Gulf instruments, so a regulated team can show its Claude controls from the first week.
With the connector, a CISO asks Claude itself where the organisation stands, from live Kapālins data.
Handled before they ask.
Each of these happens in real organisations the week Claude rolls out. Here is the moment, and what Kapālins does about it.
Illustrations of real controls. The guardrail and inside-Claude checks work with a Claude Enterprise organisation. Attacks are mapped to MITRE ATLAS.
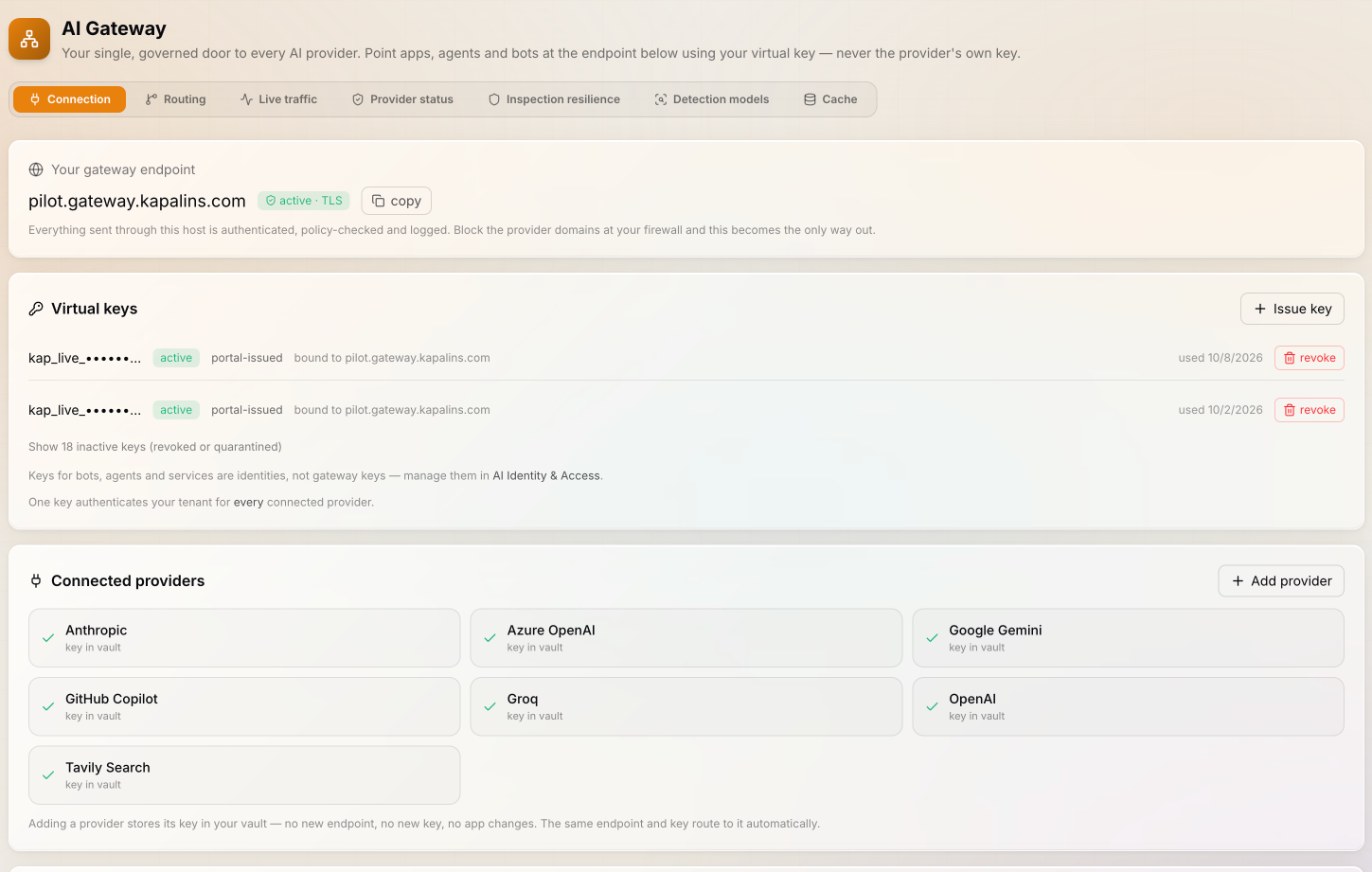
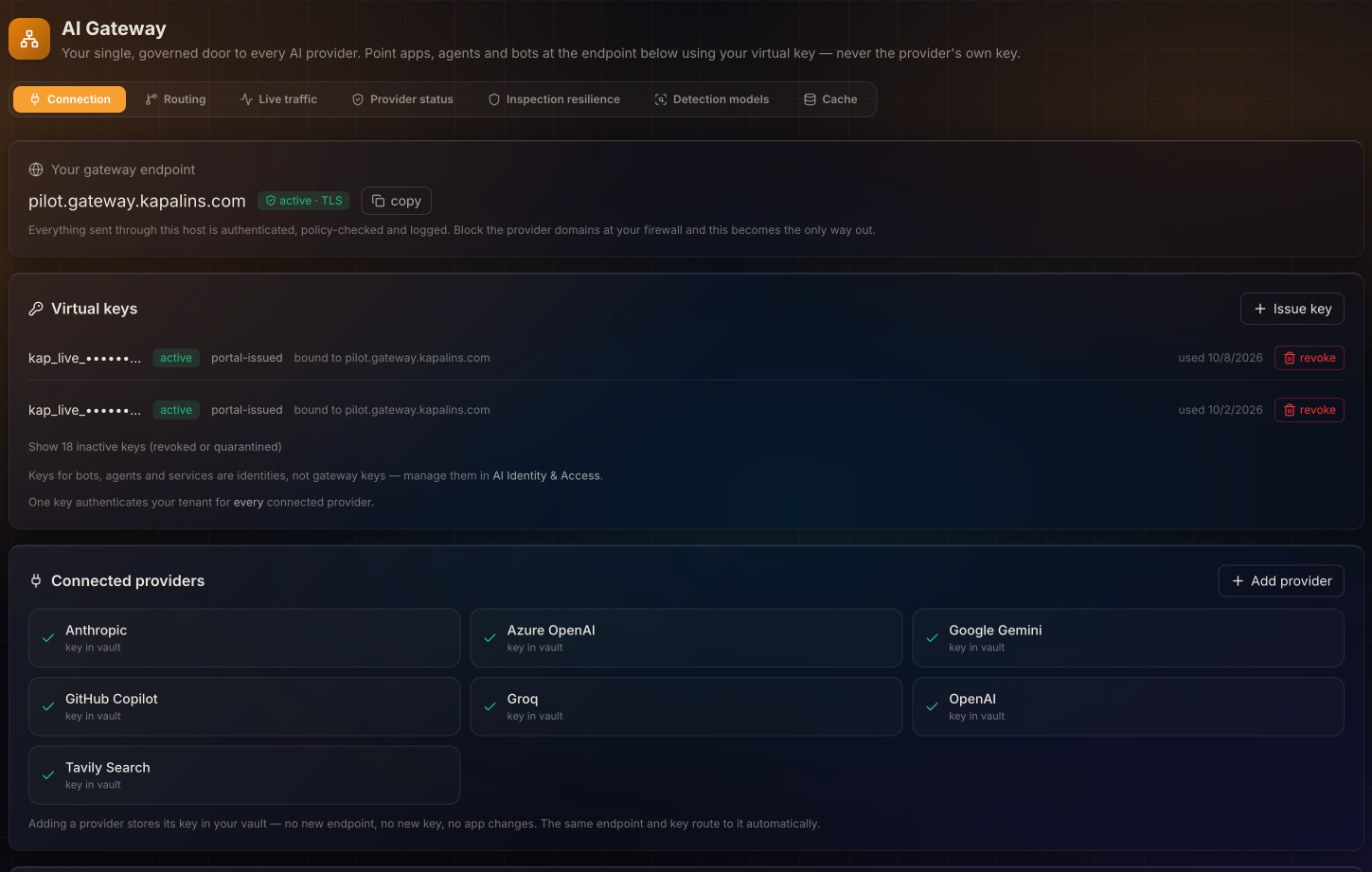
One endpoint, one key, every provider.
Point the application at your gateway host with a virtual key. Kapālins routes to Claude with the key it holds, fails over when Claude is down, and meters every call to the team that made it.
- Your app speaks Anthropic API format
- 36 Claude models priced, so spend lands on a team the same day
- Block the provider domains at your firewall and this becomes the only way out
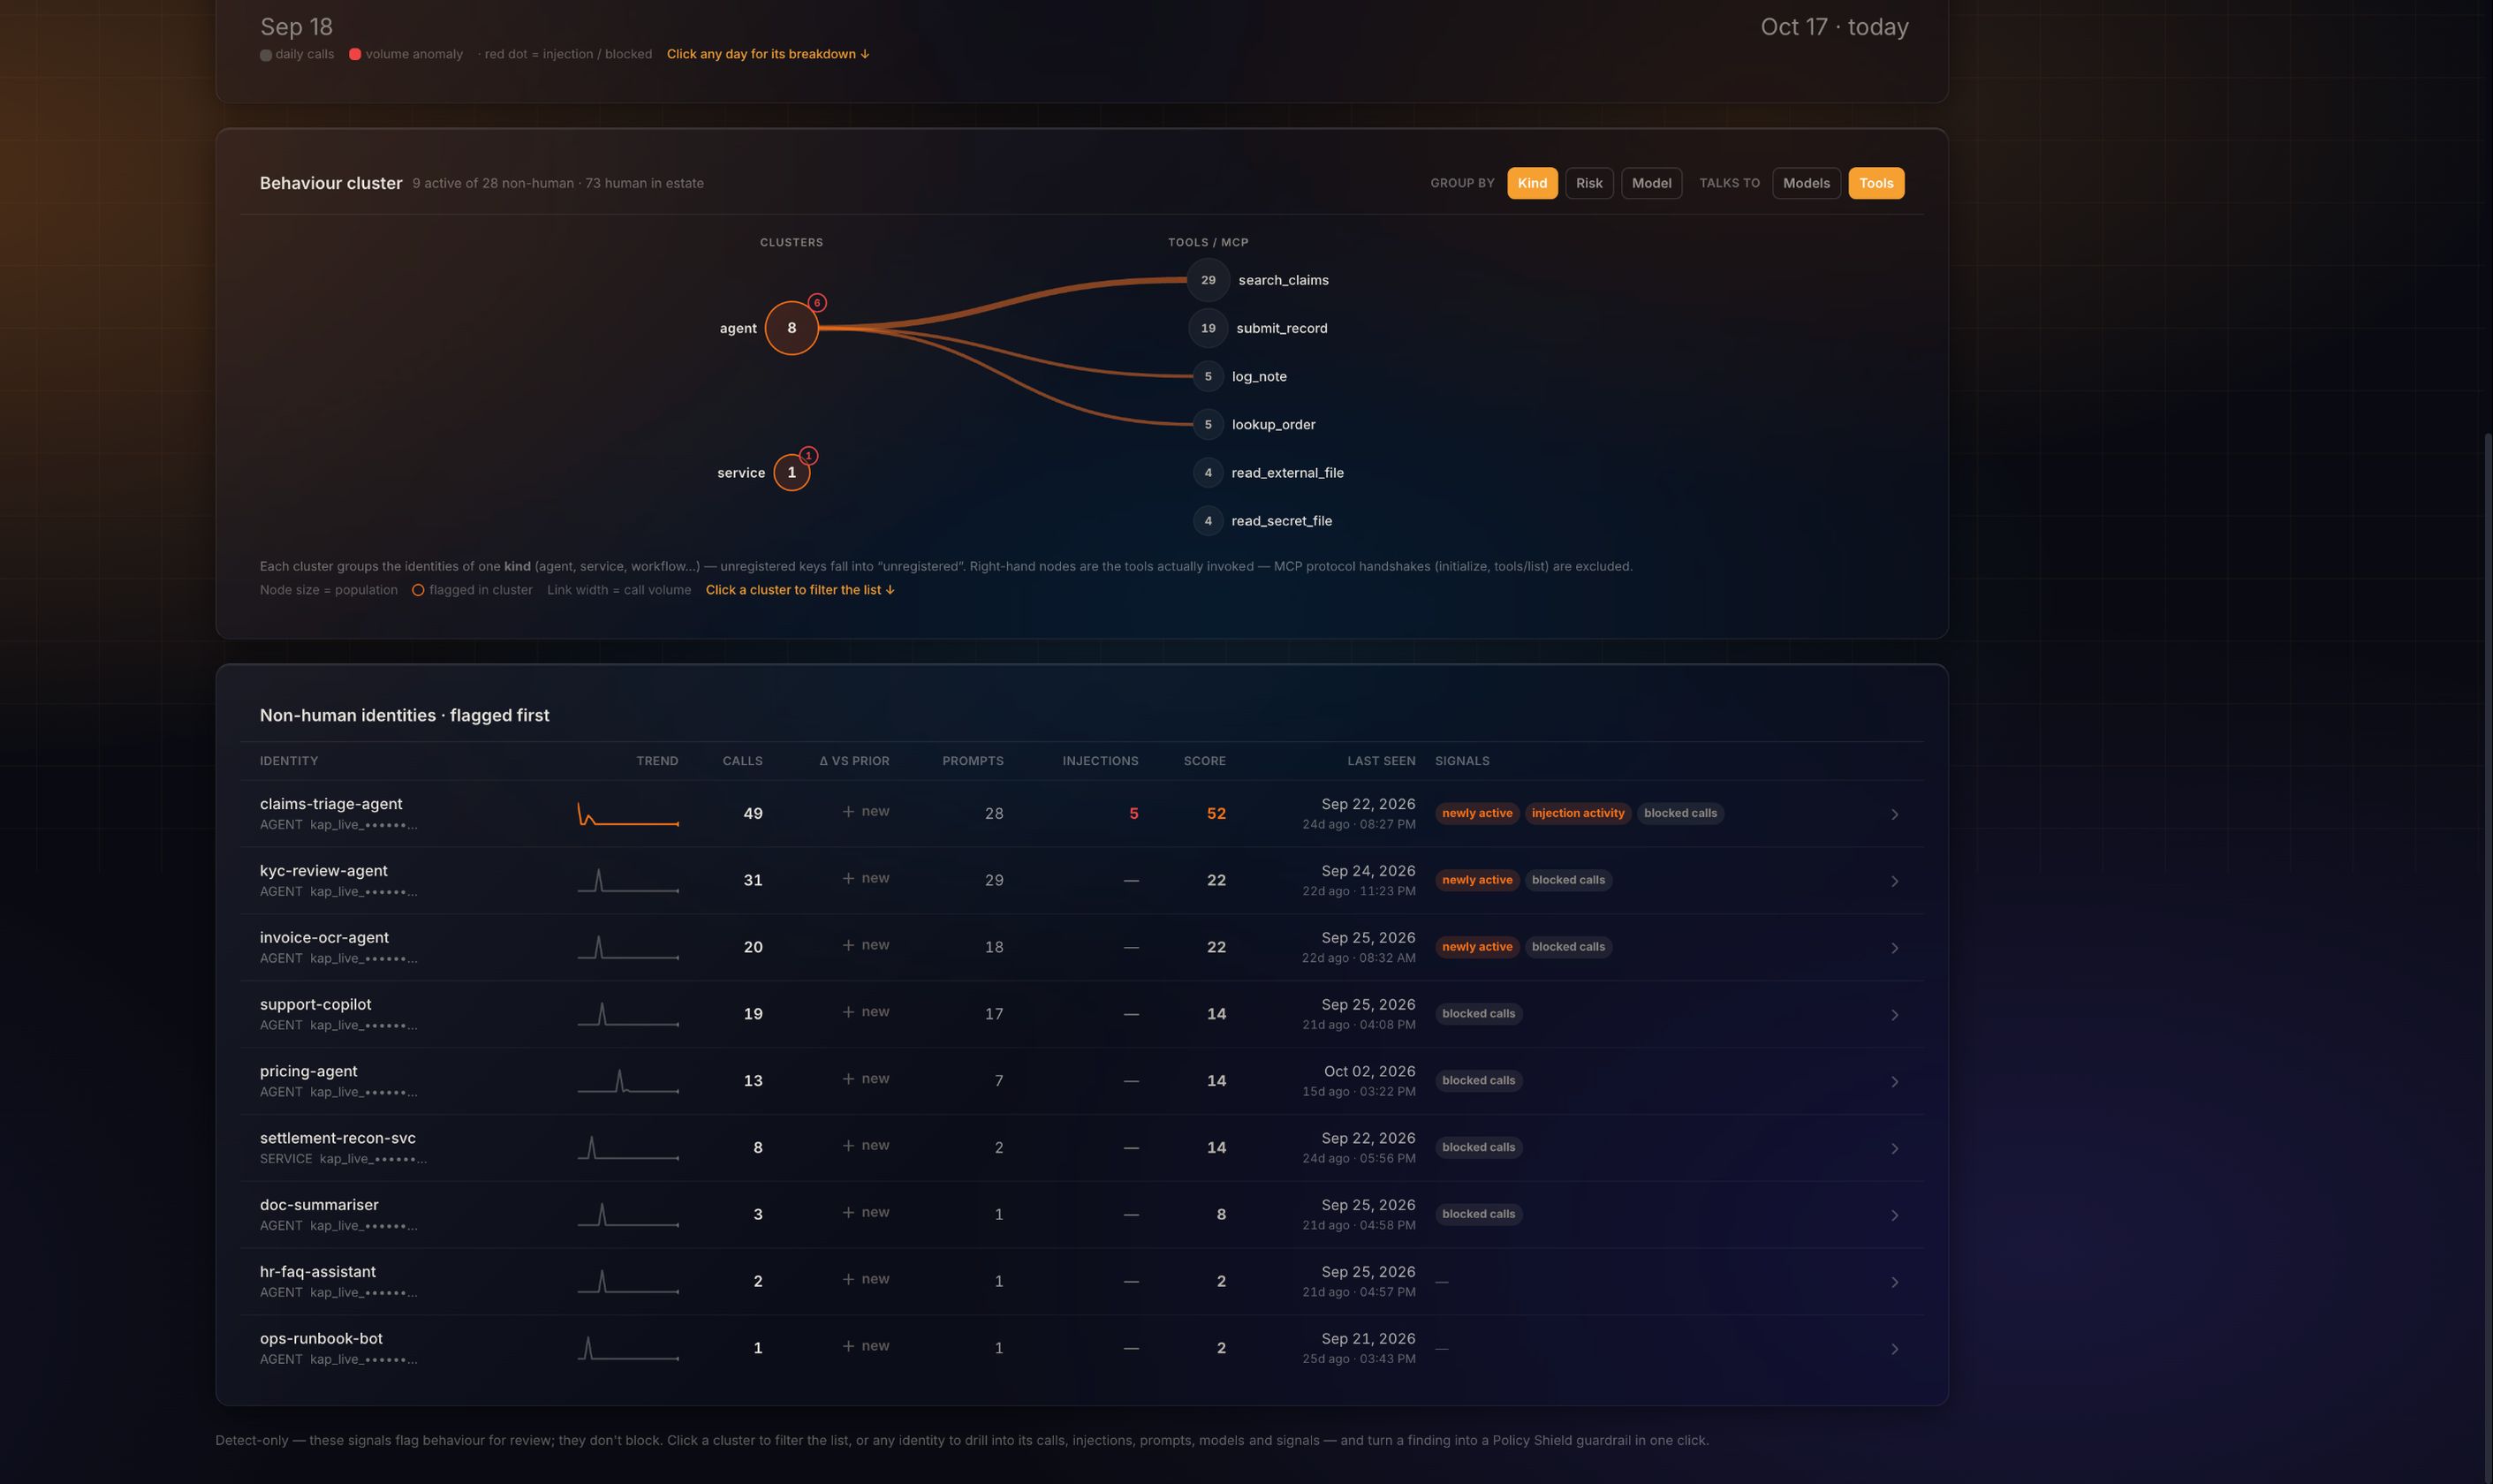
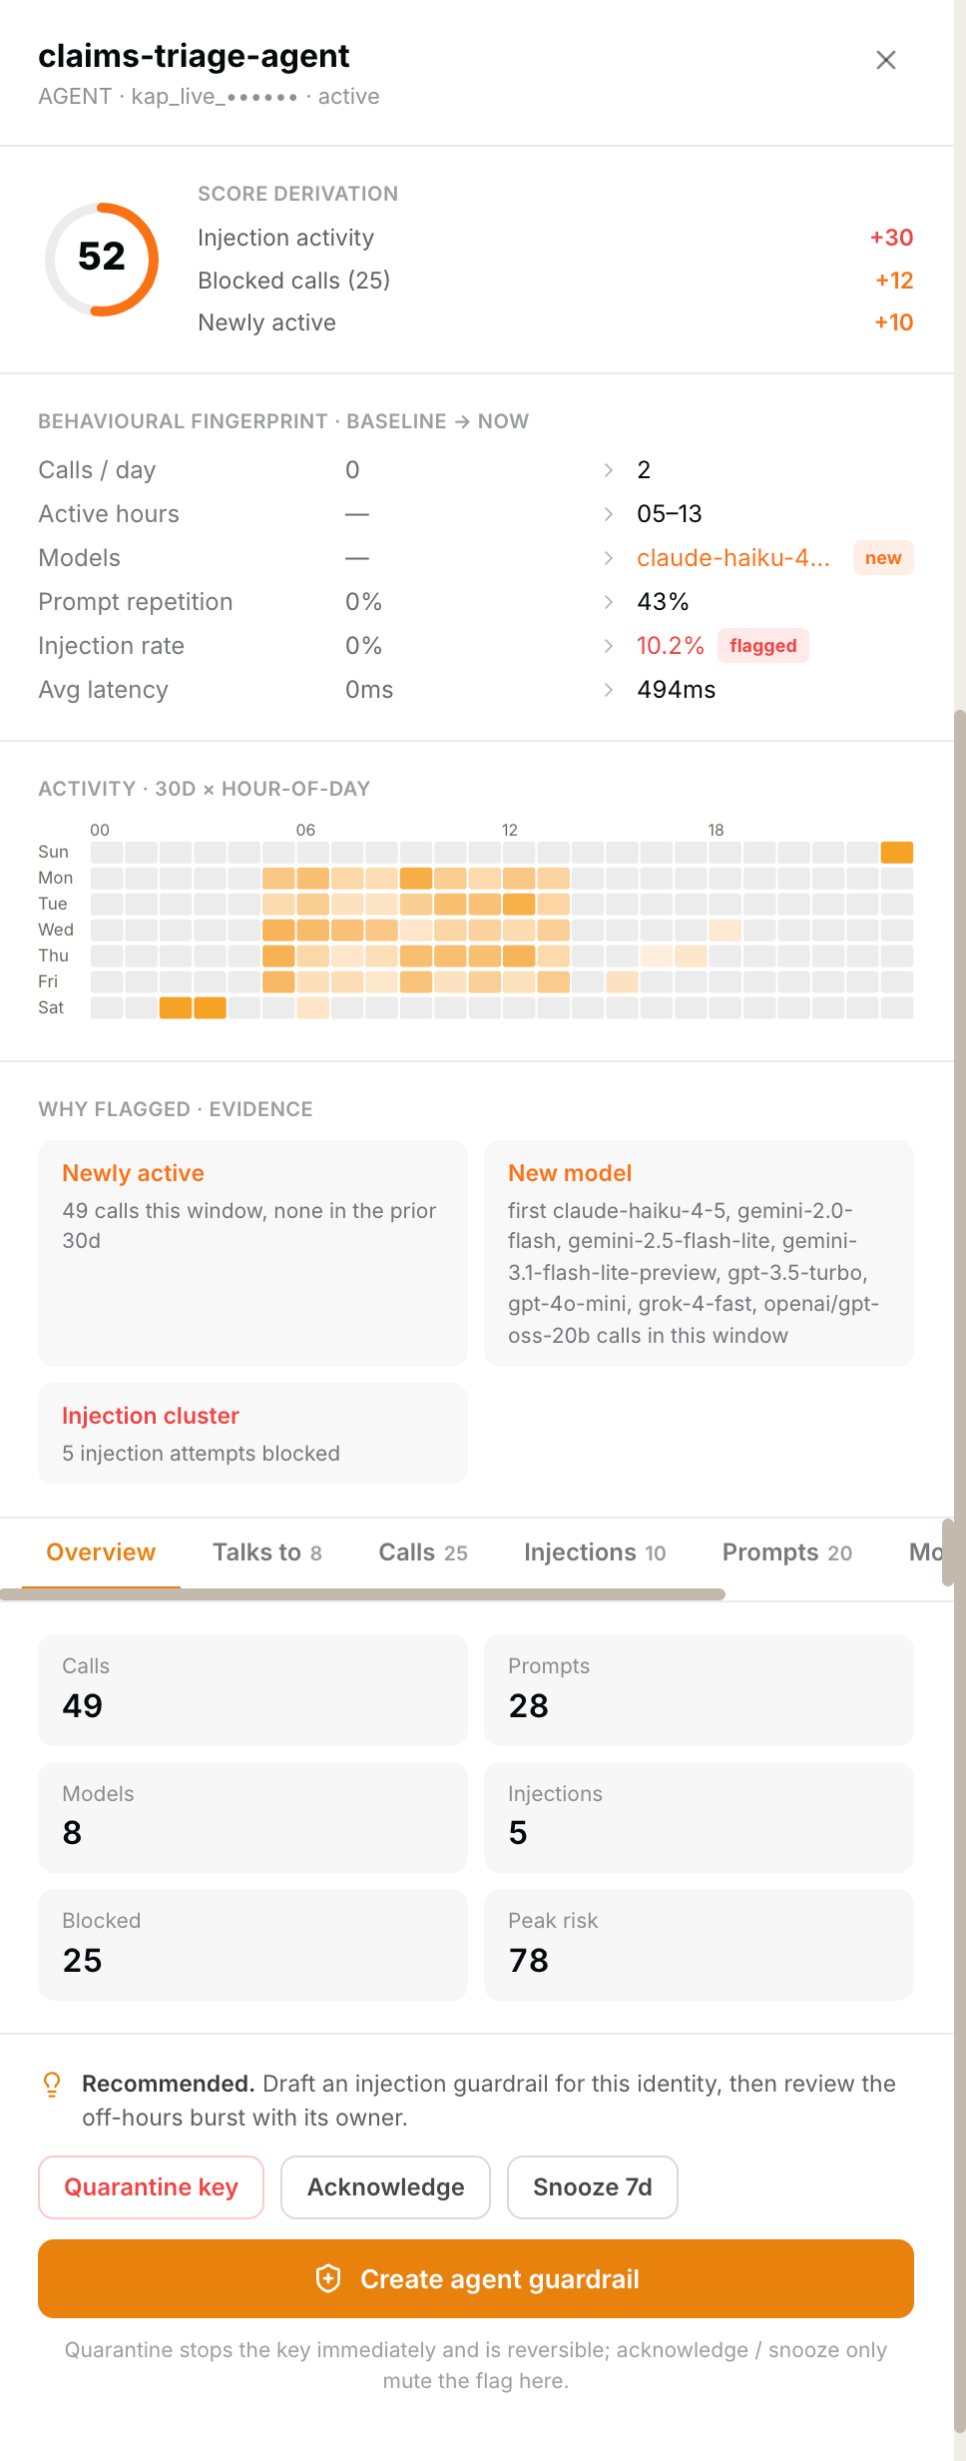
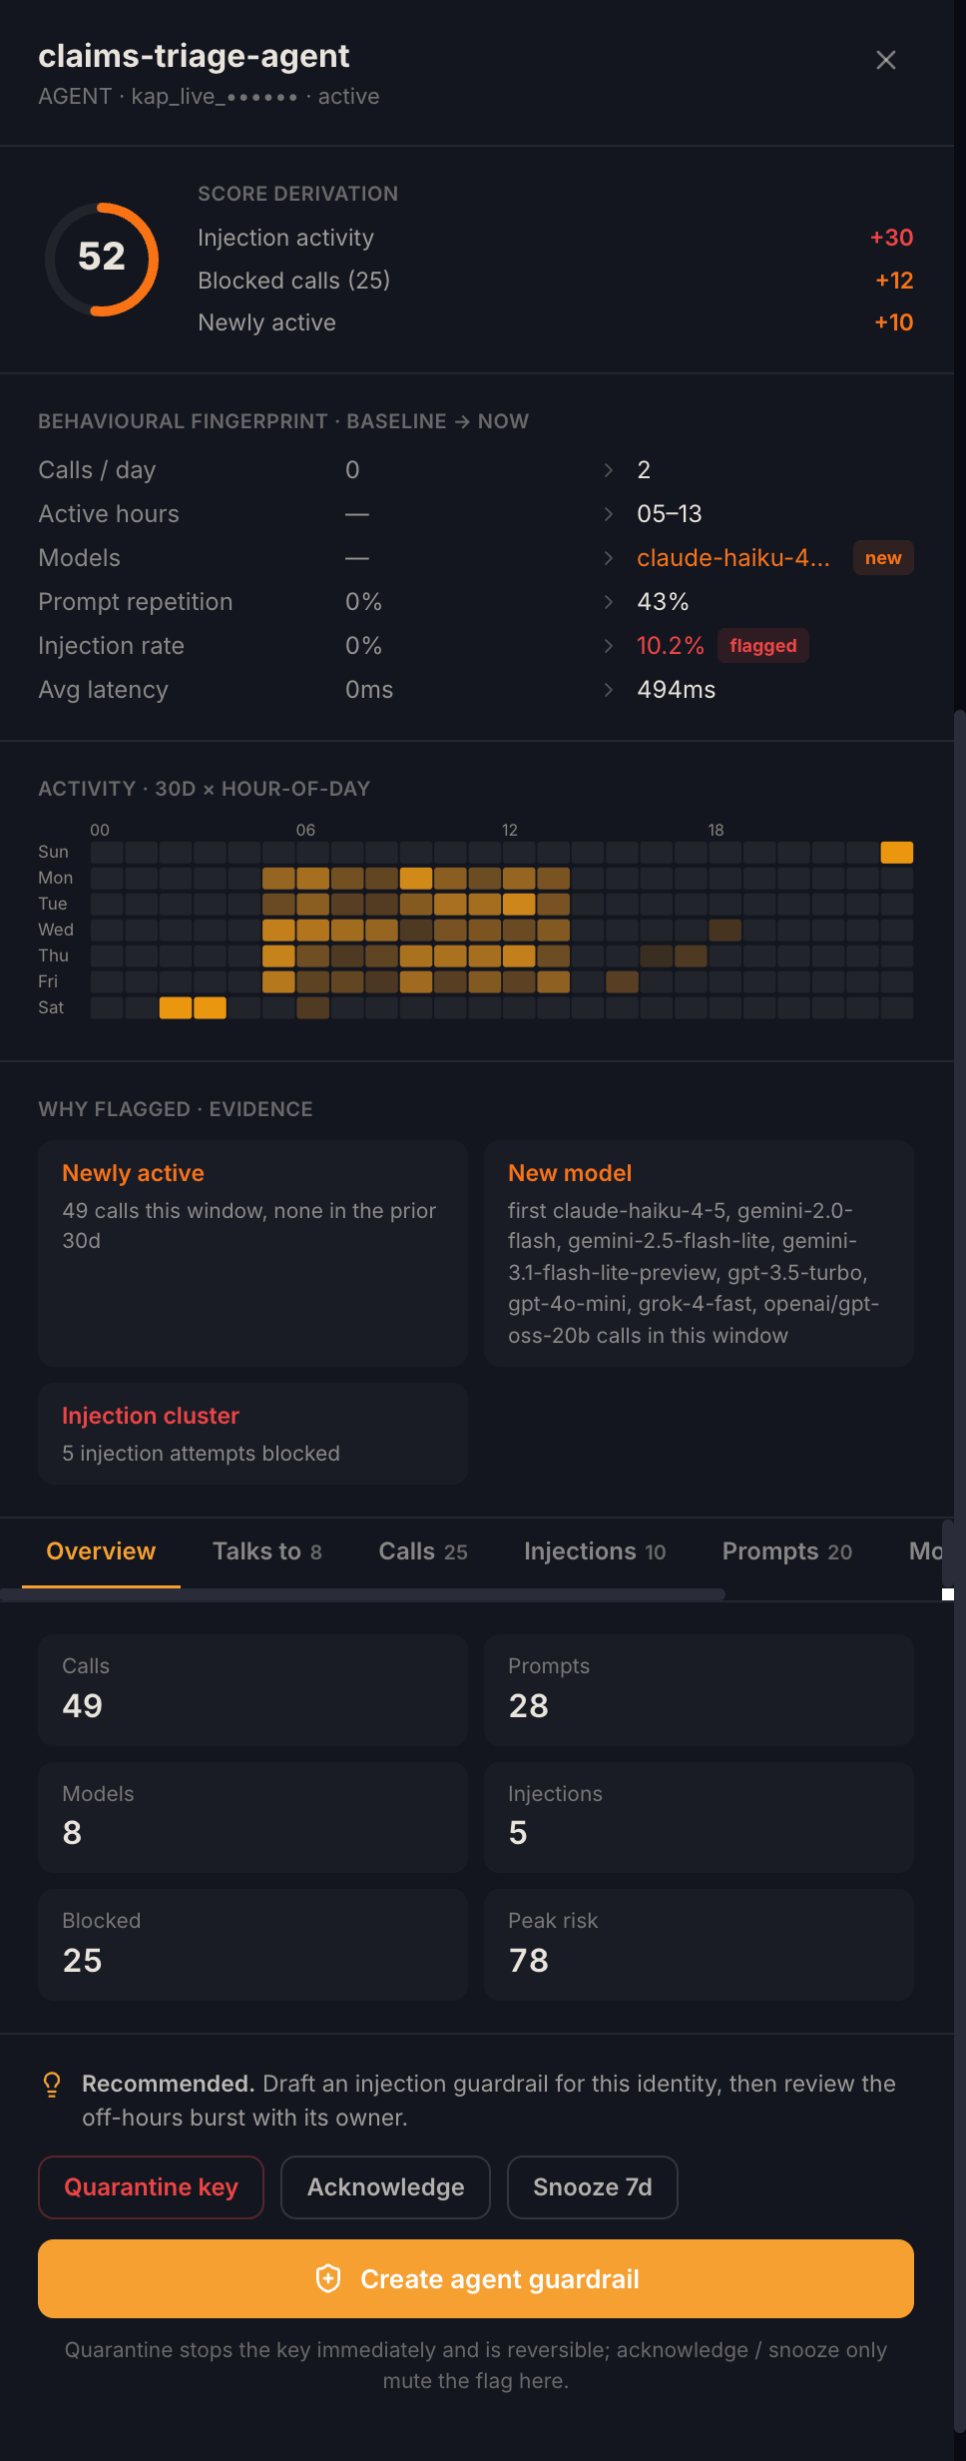
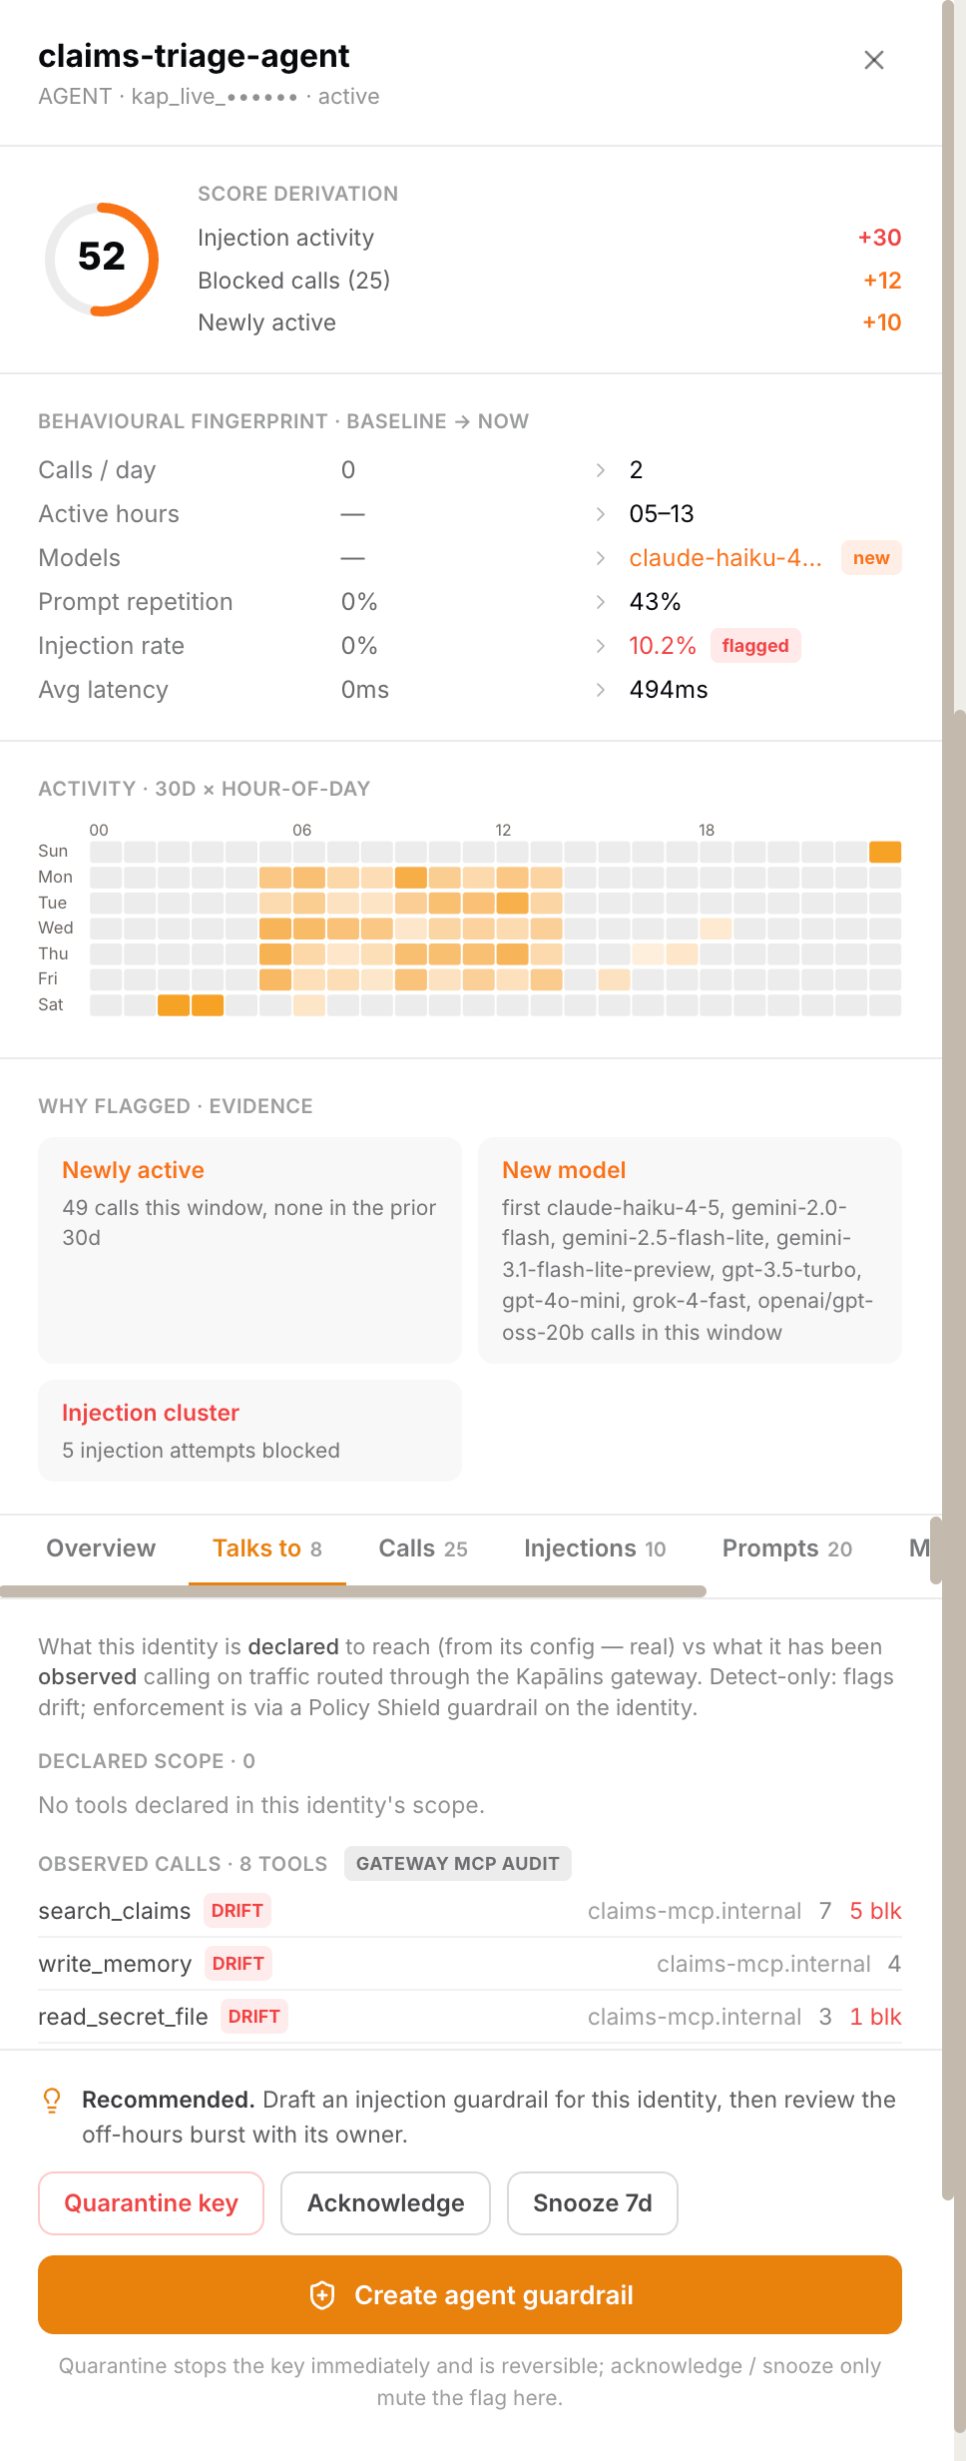
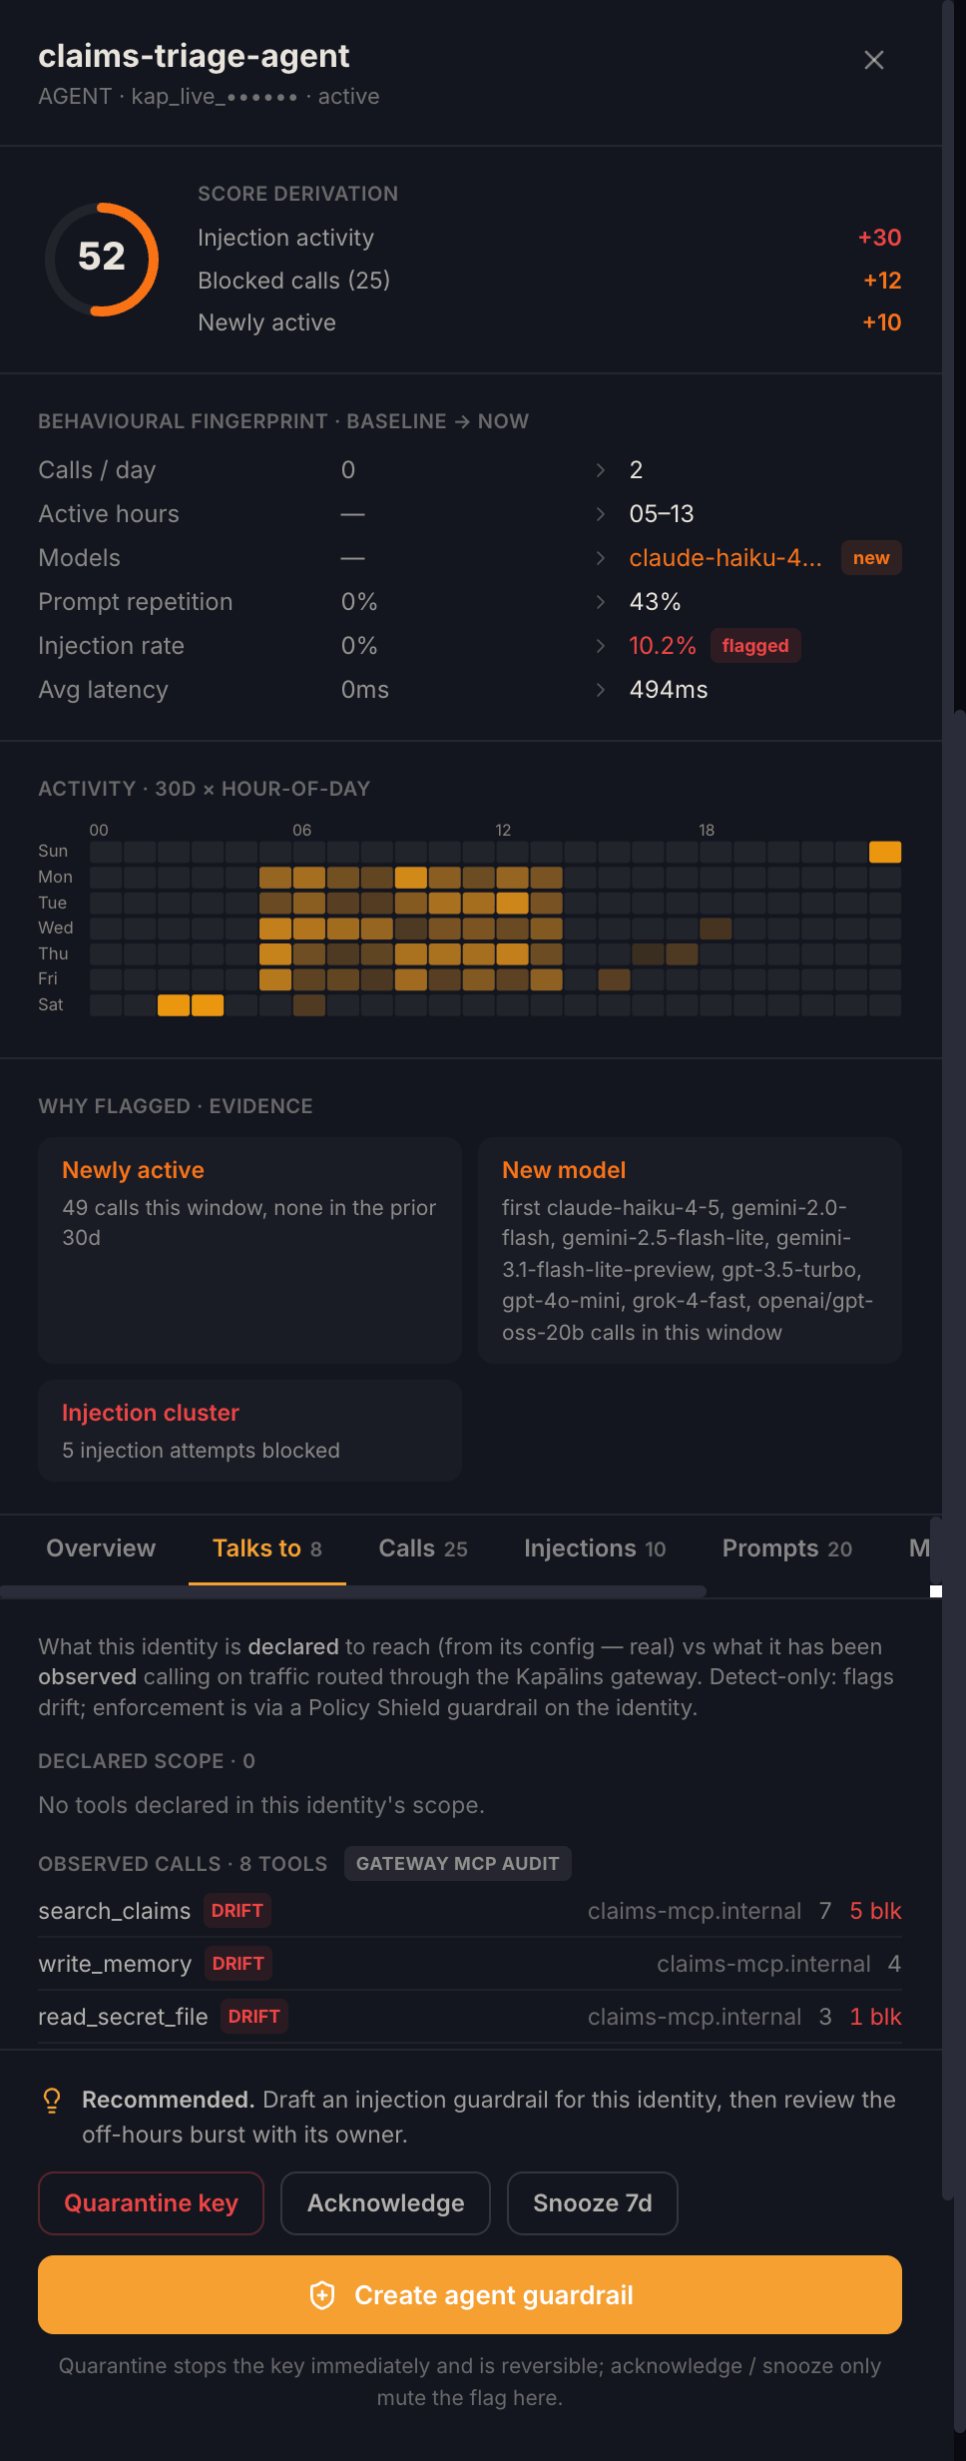
Agents calling Claude, fingerprinted.
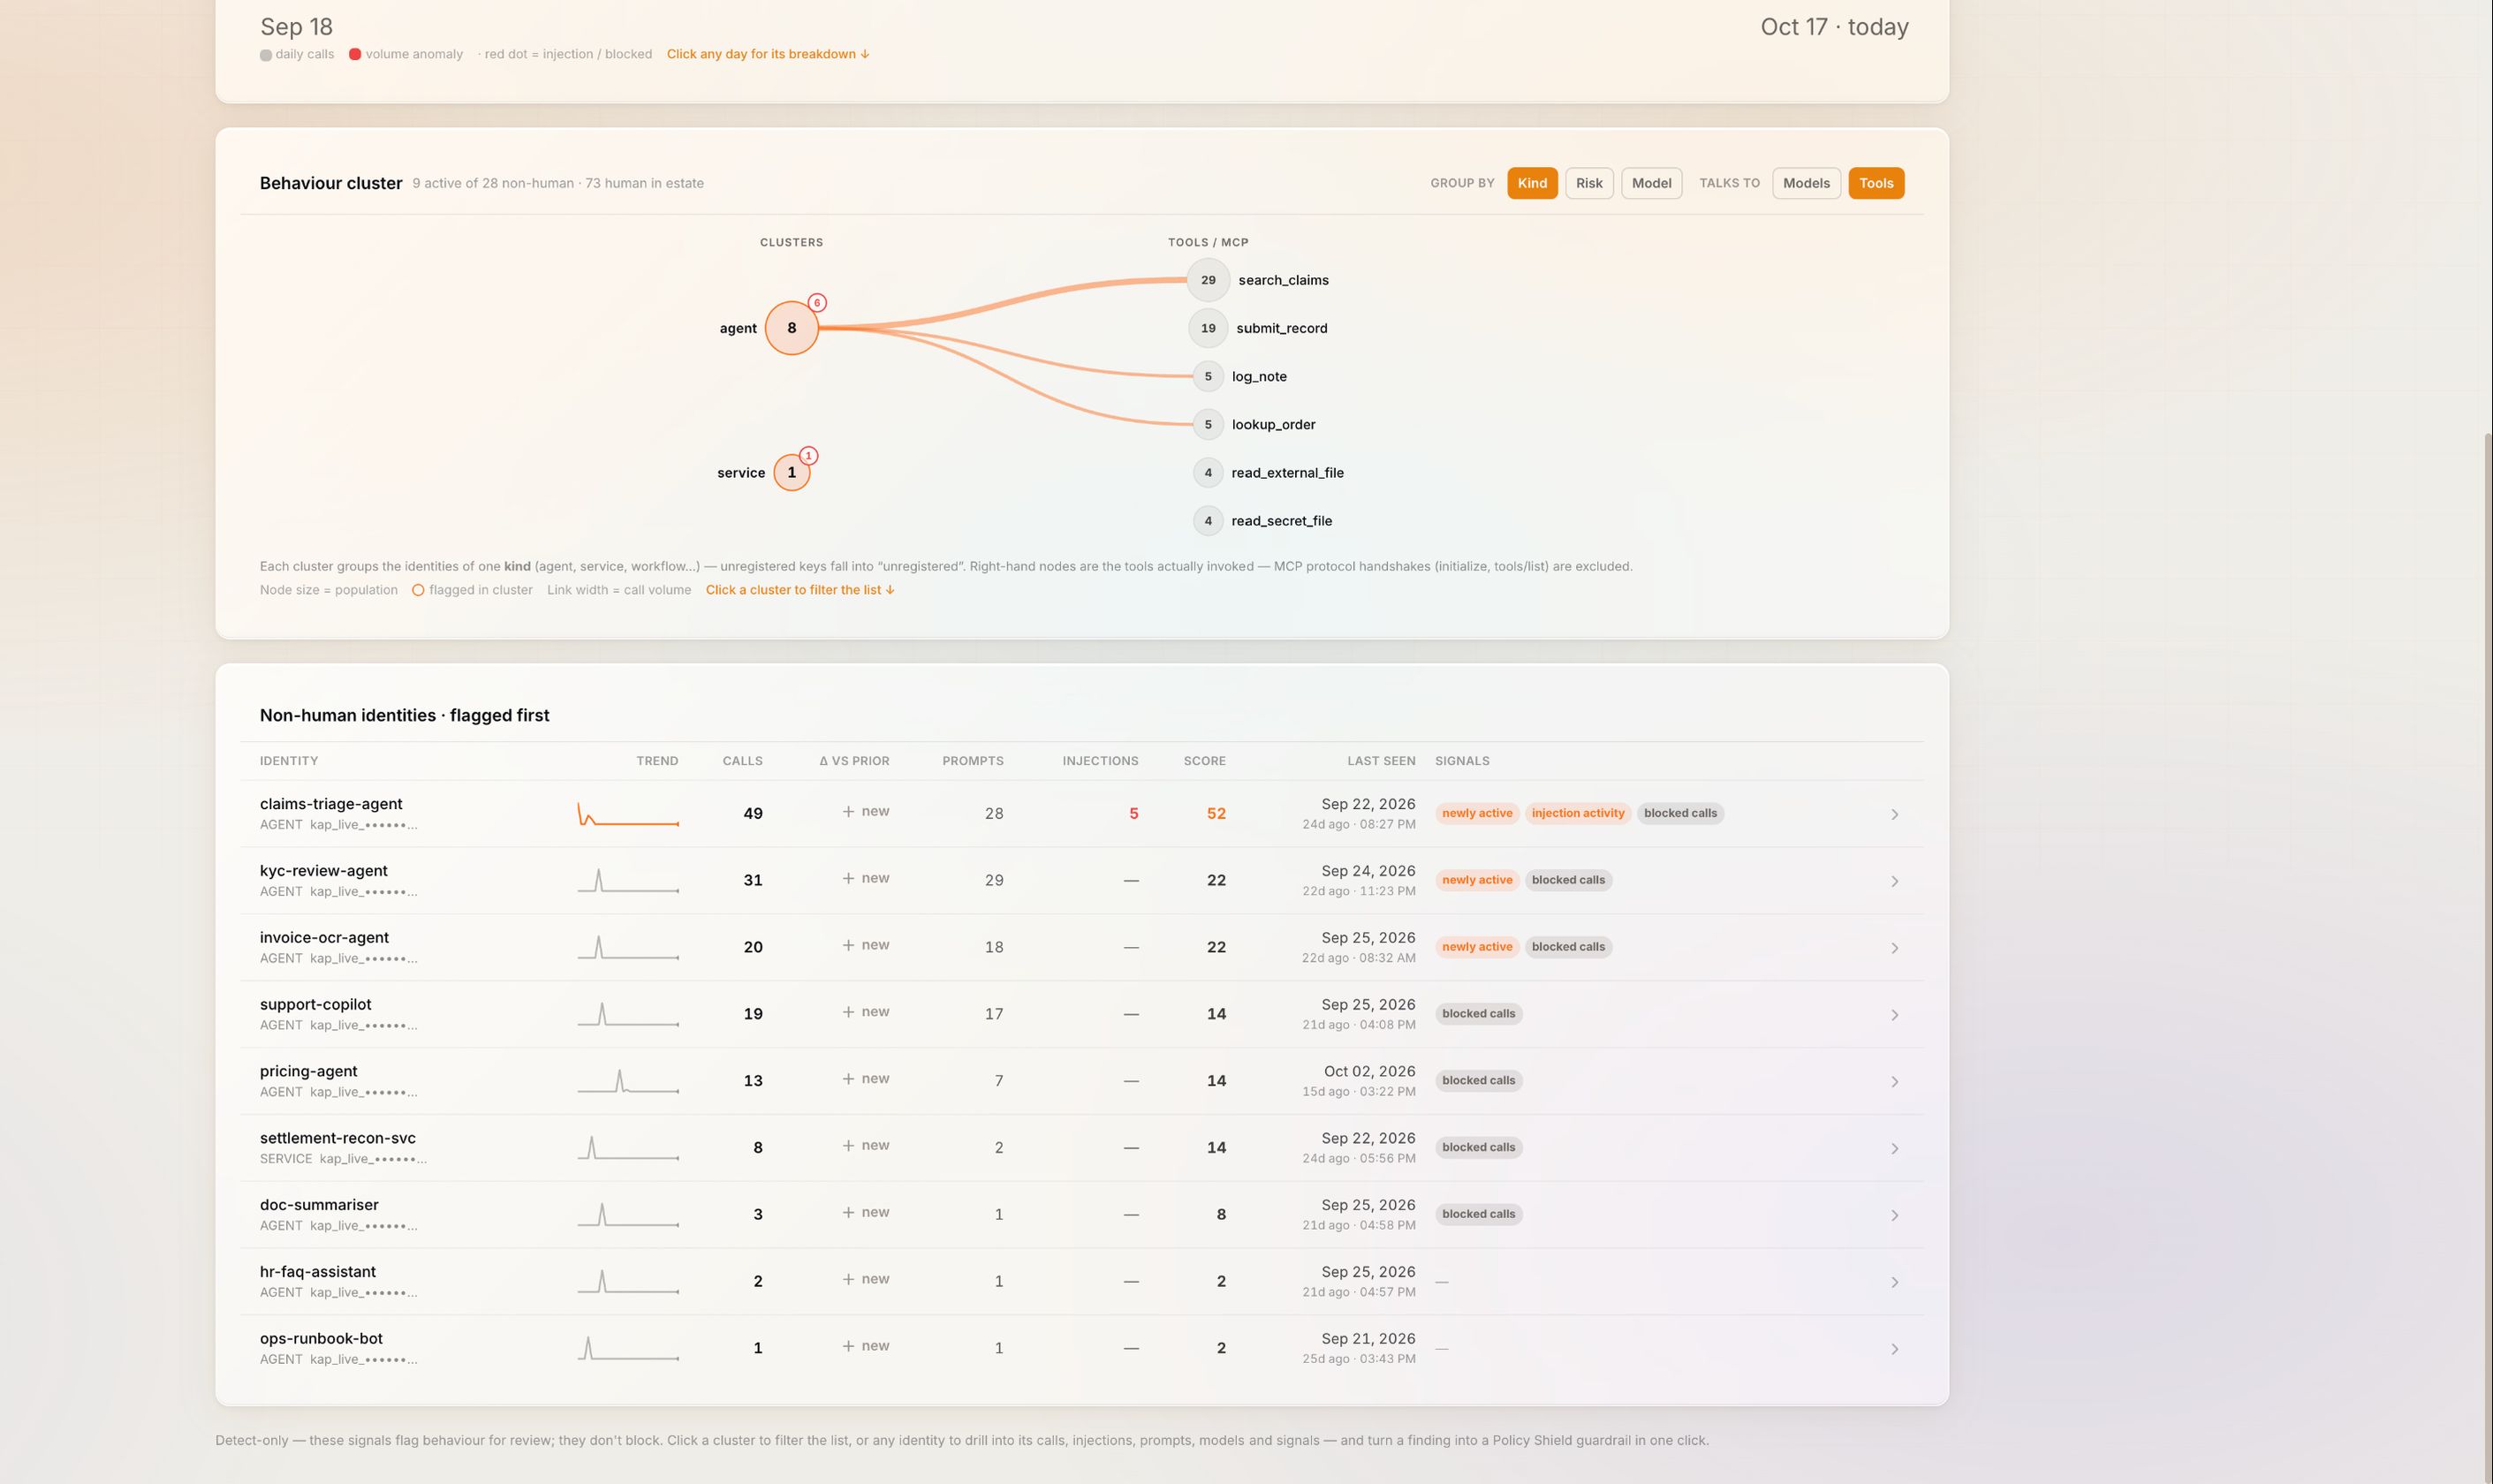
Every agent and service key that calls Claude through the gateway gets a behaviour baseline: calls, active hours, models, prompt repetition, injection rate. When one drifts it is flagged with the reasons, and one click drafts a guardrail or quarantines the key.
- The tools and MCP servers each agent actually invoked
- Detect only by default; quarantine is one click and reversible
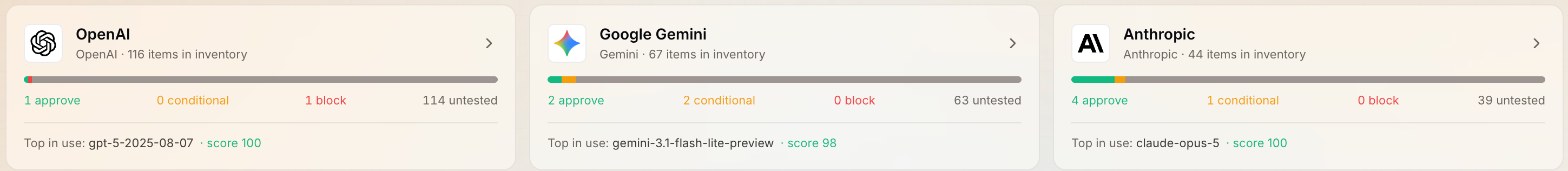
Every Anthropic model, approved or not.
The Probe Runner tests Anthropic models through your own key with the built-in red team and the Alignment Lab’s alignment tests. A model is approved, conditional or blocked from its results. On Growth and Fortress, Policy Shield acts on the verdict at the gateway; on Foundation it records what it would have refused.
- Injection, unsafe code, harmful behaviour and hallucination suites
- Scheduled tests and Alignment Core come with Model Threat Simulation at Protect (Growth and Fortress), tests on demand and Alignment Full at Prove (Fortress); Model Threat Simulation is also sold as an add-on. At See, you see the results of tests already run.
Four steps.
- Add the providerIntegrations › Claude › paste the key. Kapālins checks it with a live call, then seals it.
- Issue virtual keysOne per application or agent, each with its own policy, models and budget.
- Change the base URLPoint the application at the gateway. Request and reply formats stay as they are.
- Detect, then enforceEvery shield starts in detect, so nobody is blocked on day one. Enforcing needs the AI gateway at Protect; below it, the gateway records what it would have blocked.
See Claude governed in thirty minutes.
Bring the person who holds the credential. We connect it live and watch the first events land.
Questions buyers ask.
Does the gateway add latency to Claude calls?
Policy Shield runs in the request path. Each family can be set to detect only, and the gateway reports its own added time per call in the timeline.
Do my applications need code changes?
A base URL and a key. The gateway accepts the OpenAI and Anthropic formats, so request and response handling stay as they are.
Can Claude be governed without the gateway?
Routing is what makes inline control possible. AI that cannot be routed, such as hosted copilots, is governed from its audit logs, identity grants and the device sensor instead.