Kapālins for Elastic
Your SOC keeps working in Elastic Security and Elasticsearch, on Elastic Cloud or self-managed. Kapālins sends every AI finding, block and incident there through the Elasticsearch _bulk API, one Elastic Common Schema document per finding, into a data stream your detection rules query by name, with the person, the rule and what was stopped on each one.


No new console for the SOC
Analysts triage AI findings in Elastic, next to everything else, in its own field names.
AI-specific signal you do not have today
Prompt injection, sensitive data in prompts, unapproved models and agent tool calls, mapped to MITRE ATLAS before they arrive.
Every push on record
Each push is logged with Elastic’s response, and the integration shows the last error until the next push succeeds.
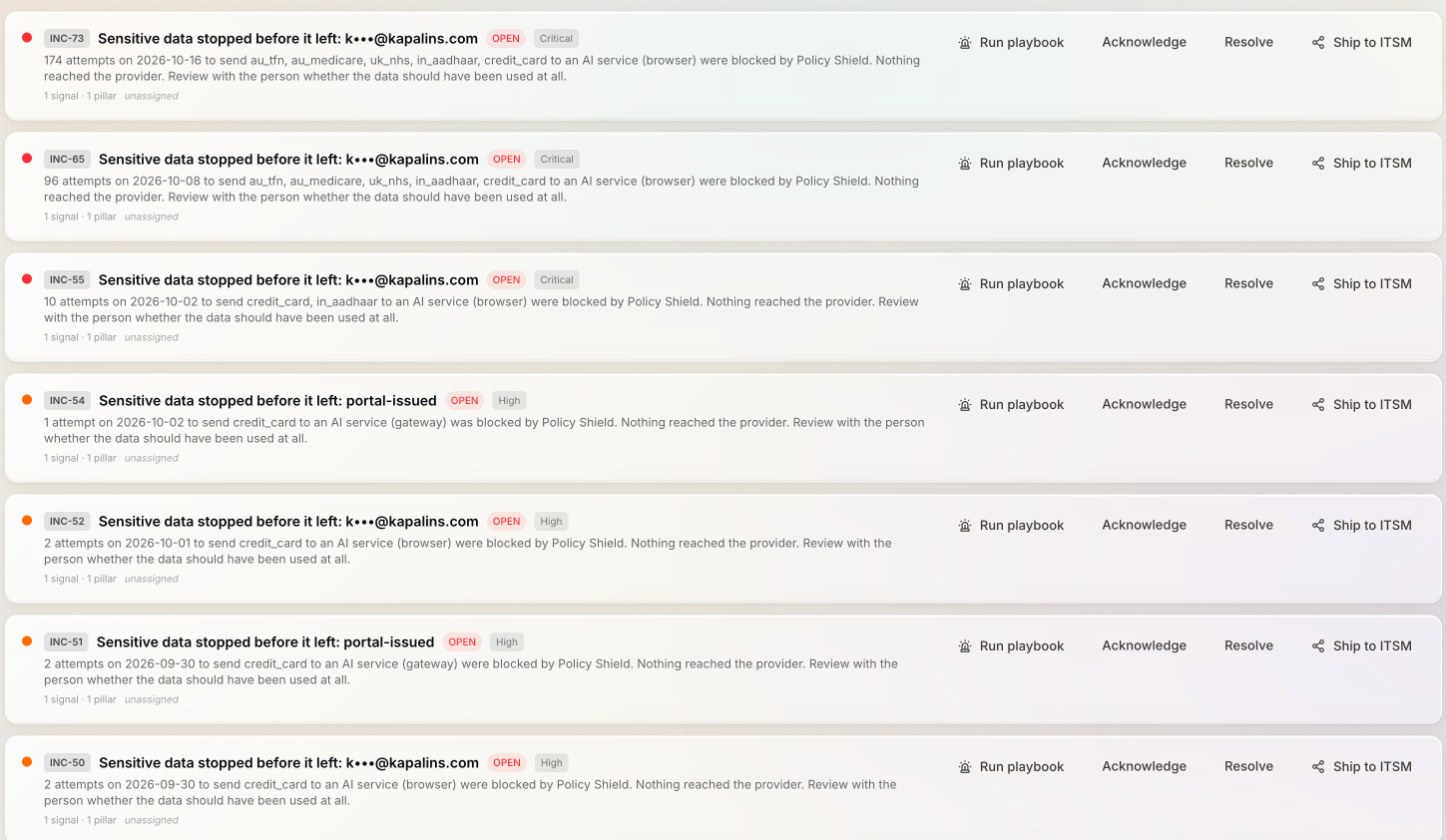
What lands in Elastic.
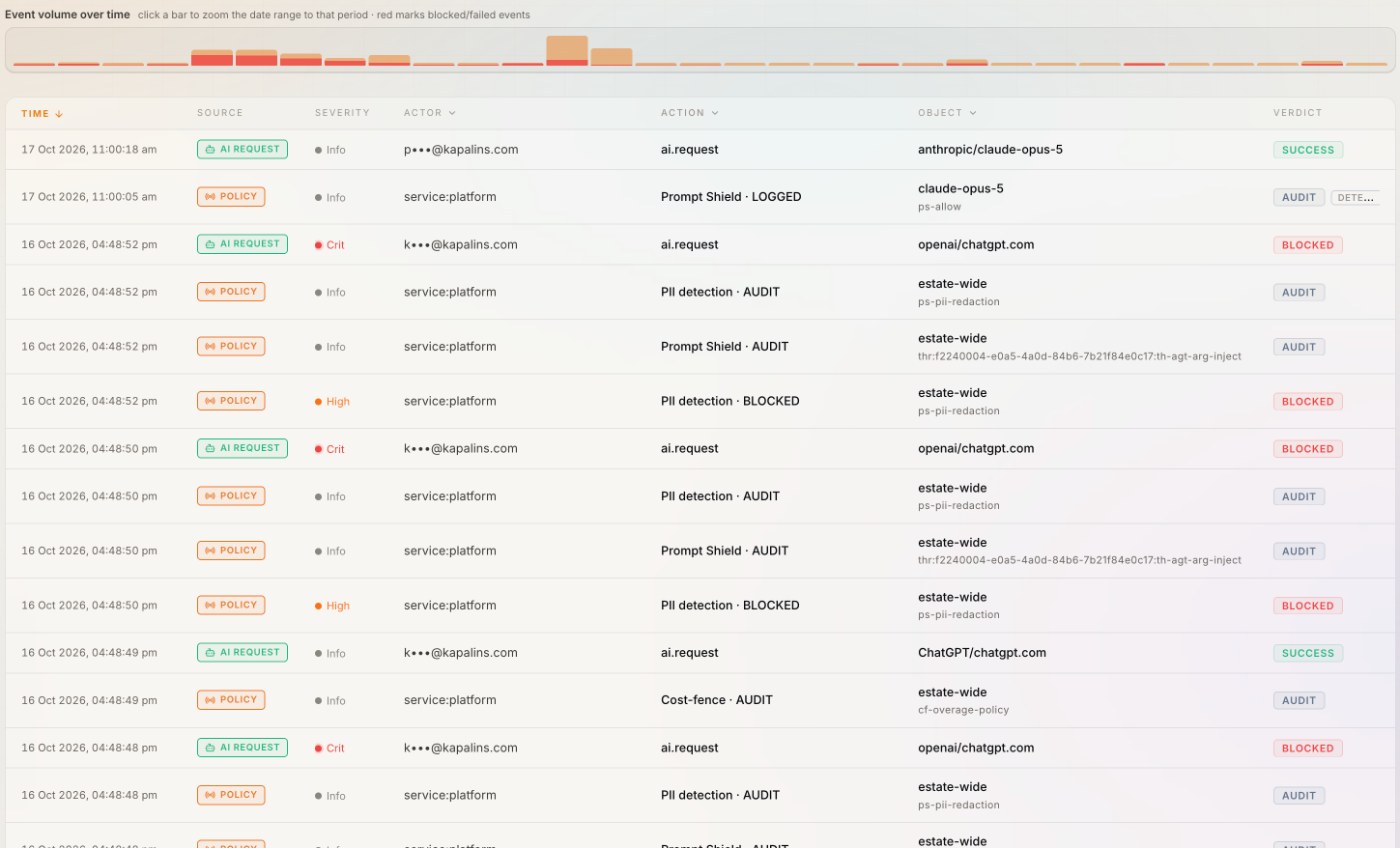
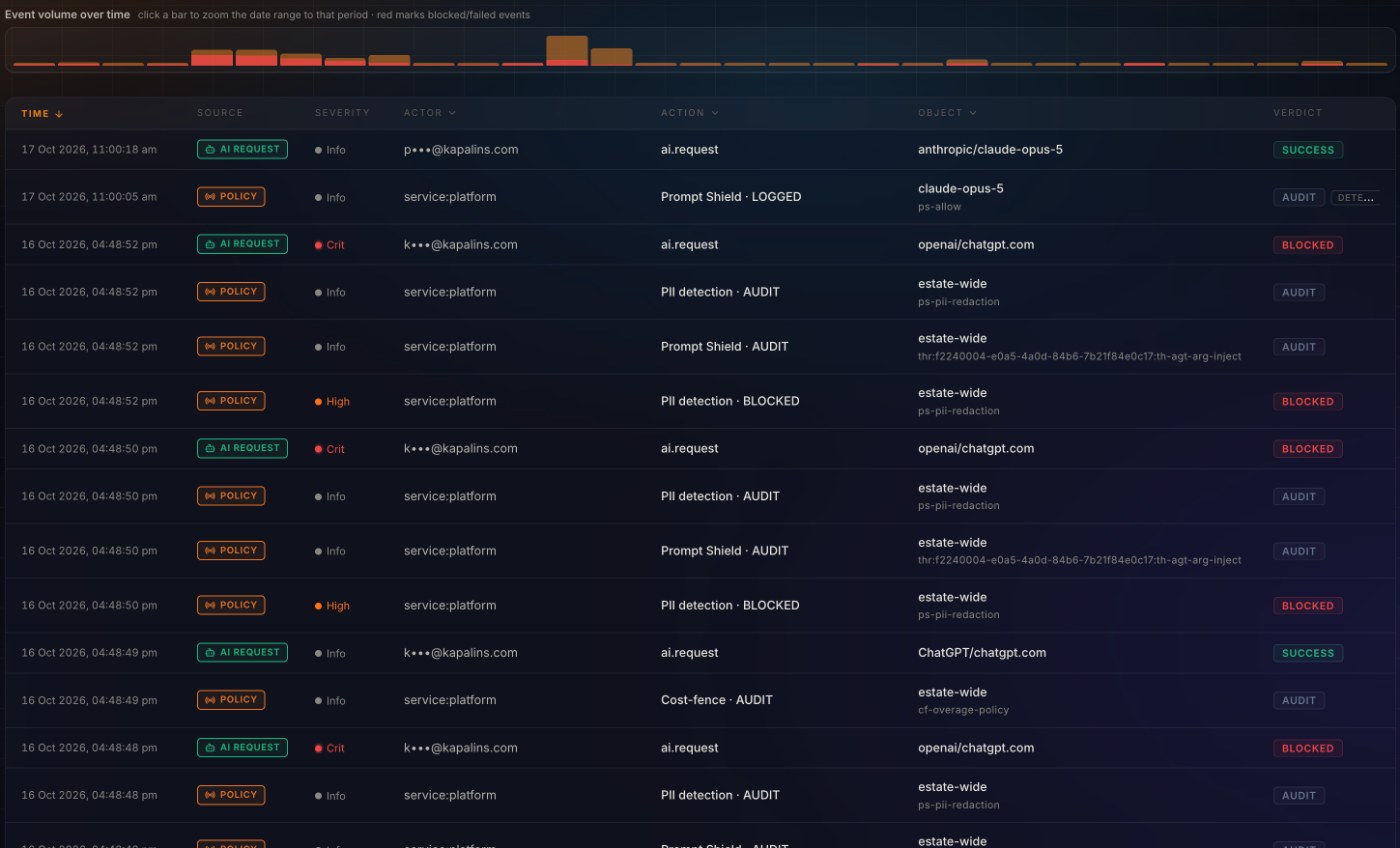
Each event carries its severity, the person, the rule that fired, what was stopped and the Kapālins event id, so the evidence is one search away. Every verdict is sent as it happens; your rules and searches decide what becomes an alert.
- Sent through the Elasticsearch _bulk API, one Elastic Common Schema document per finding, into a data stream your detection rules query by name
- Credential: an API key allowed to write to that data stream, and your Elasticsearch endpoint
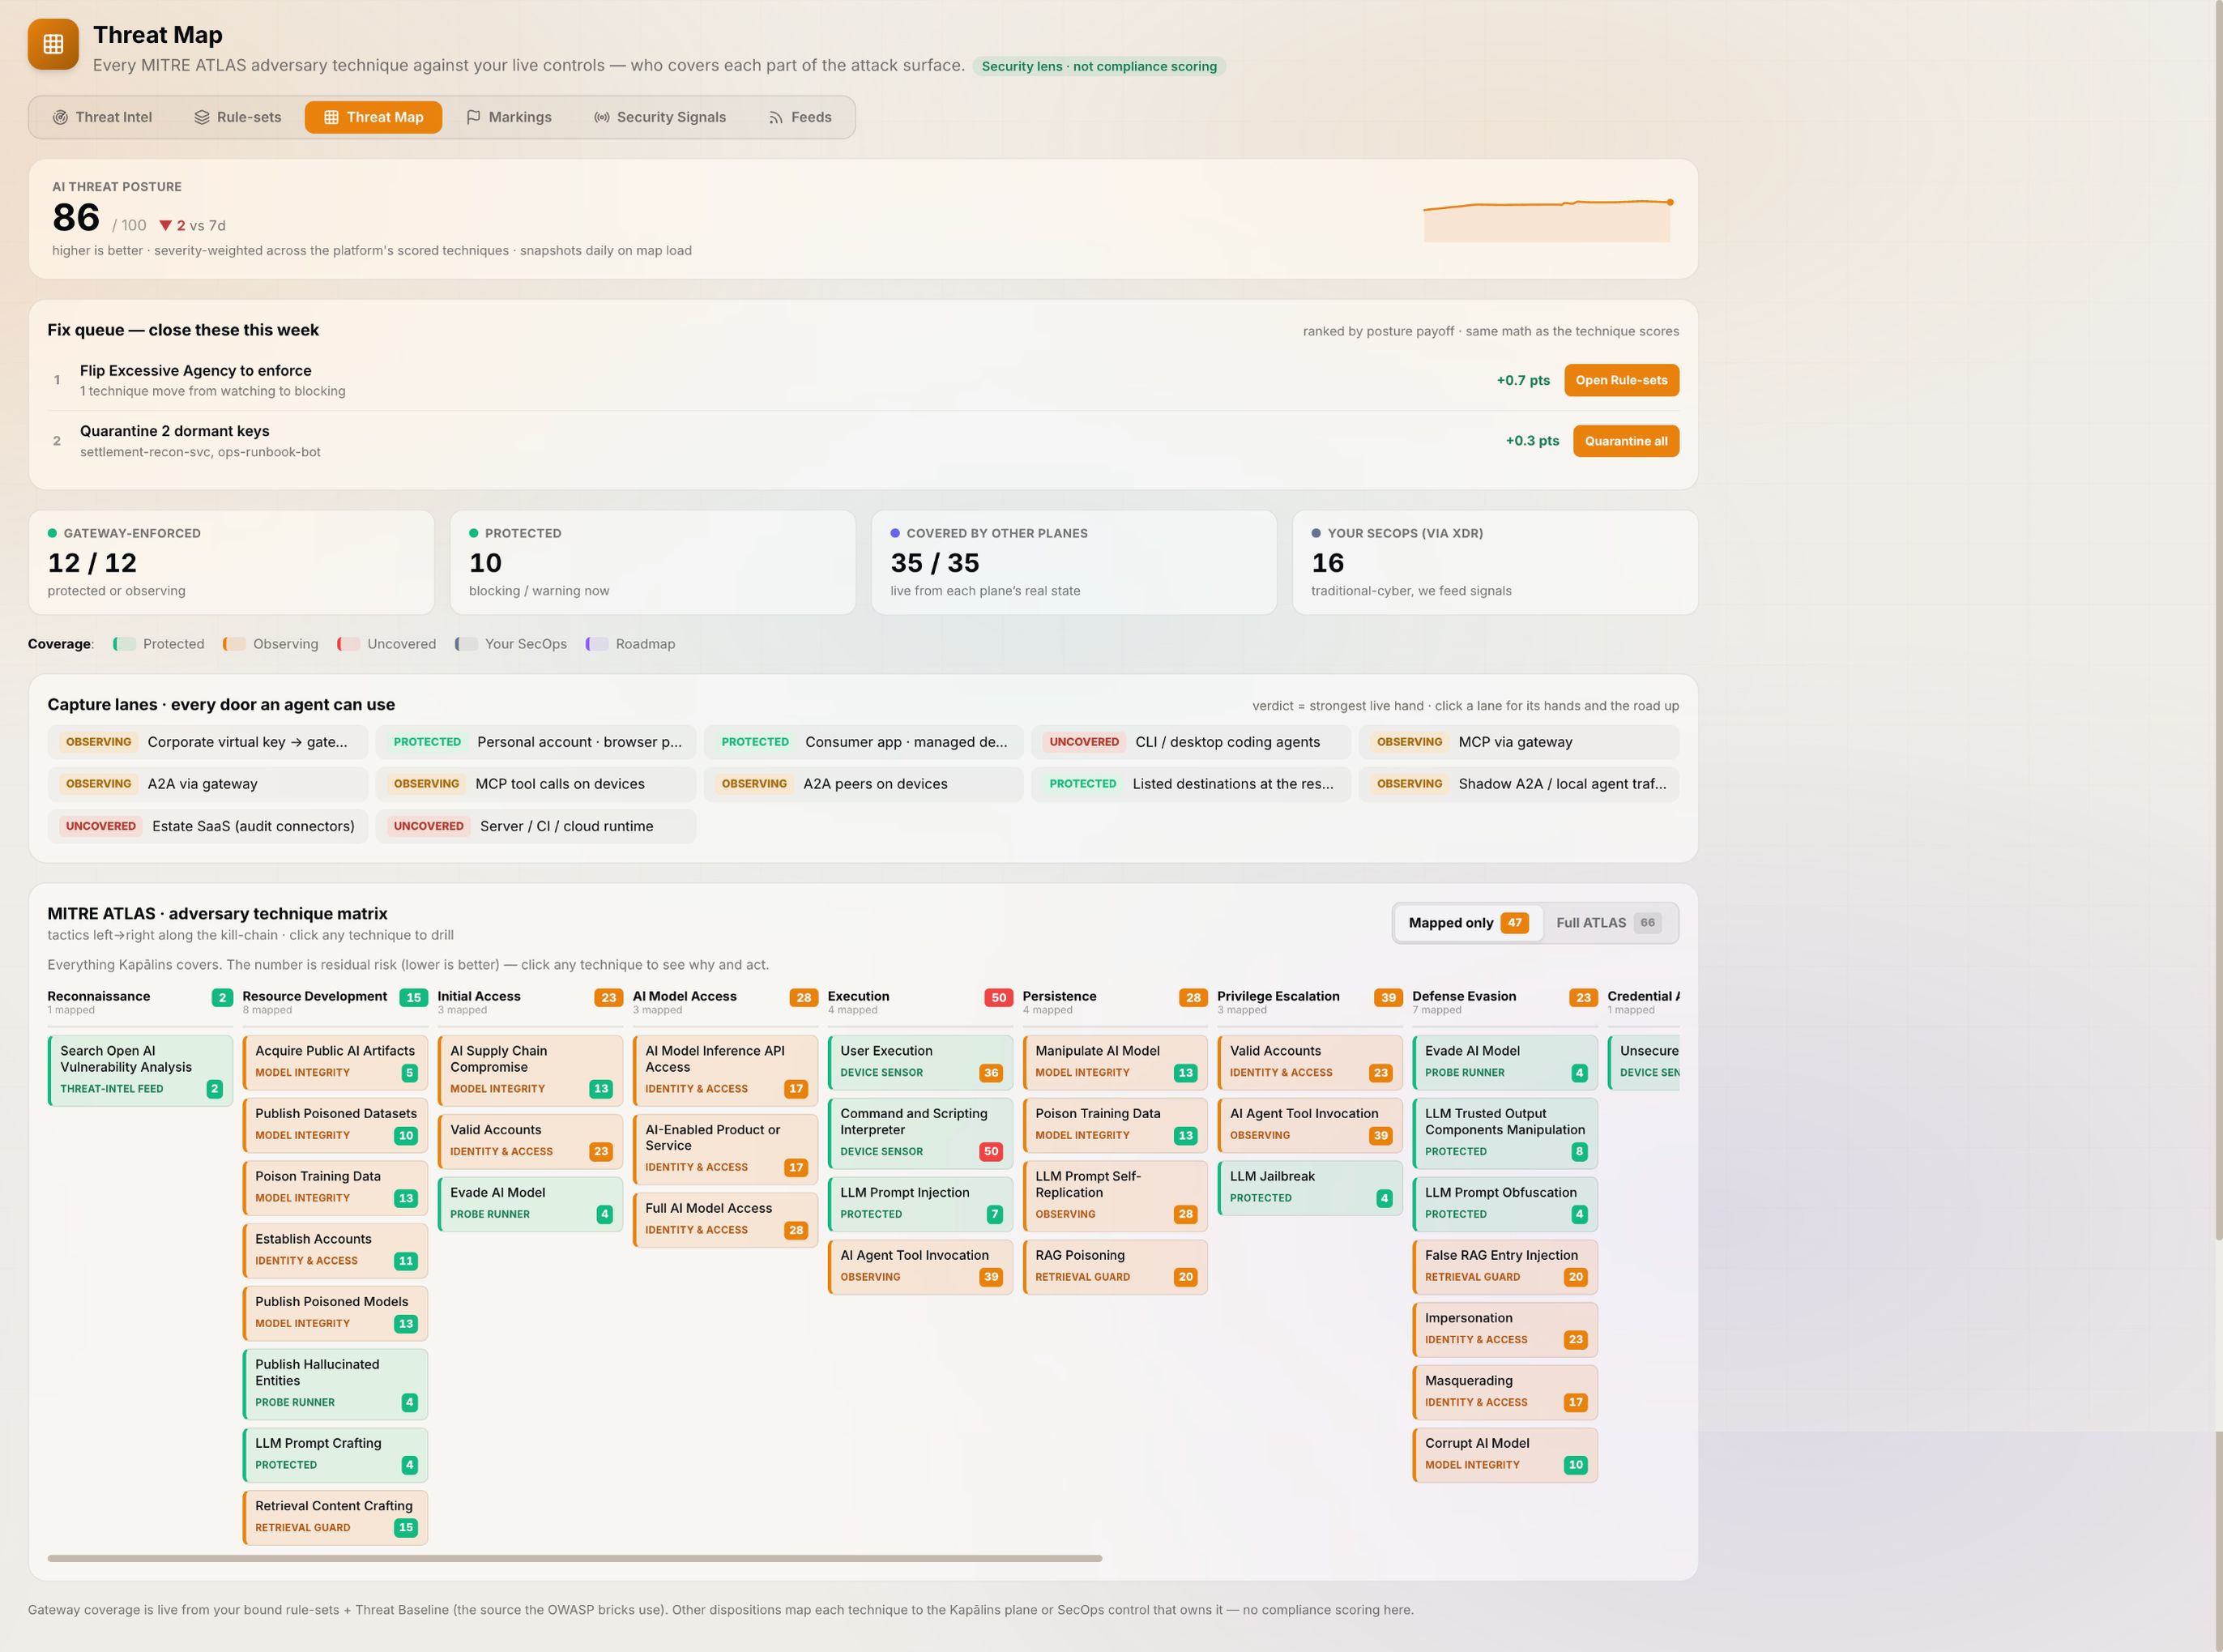
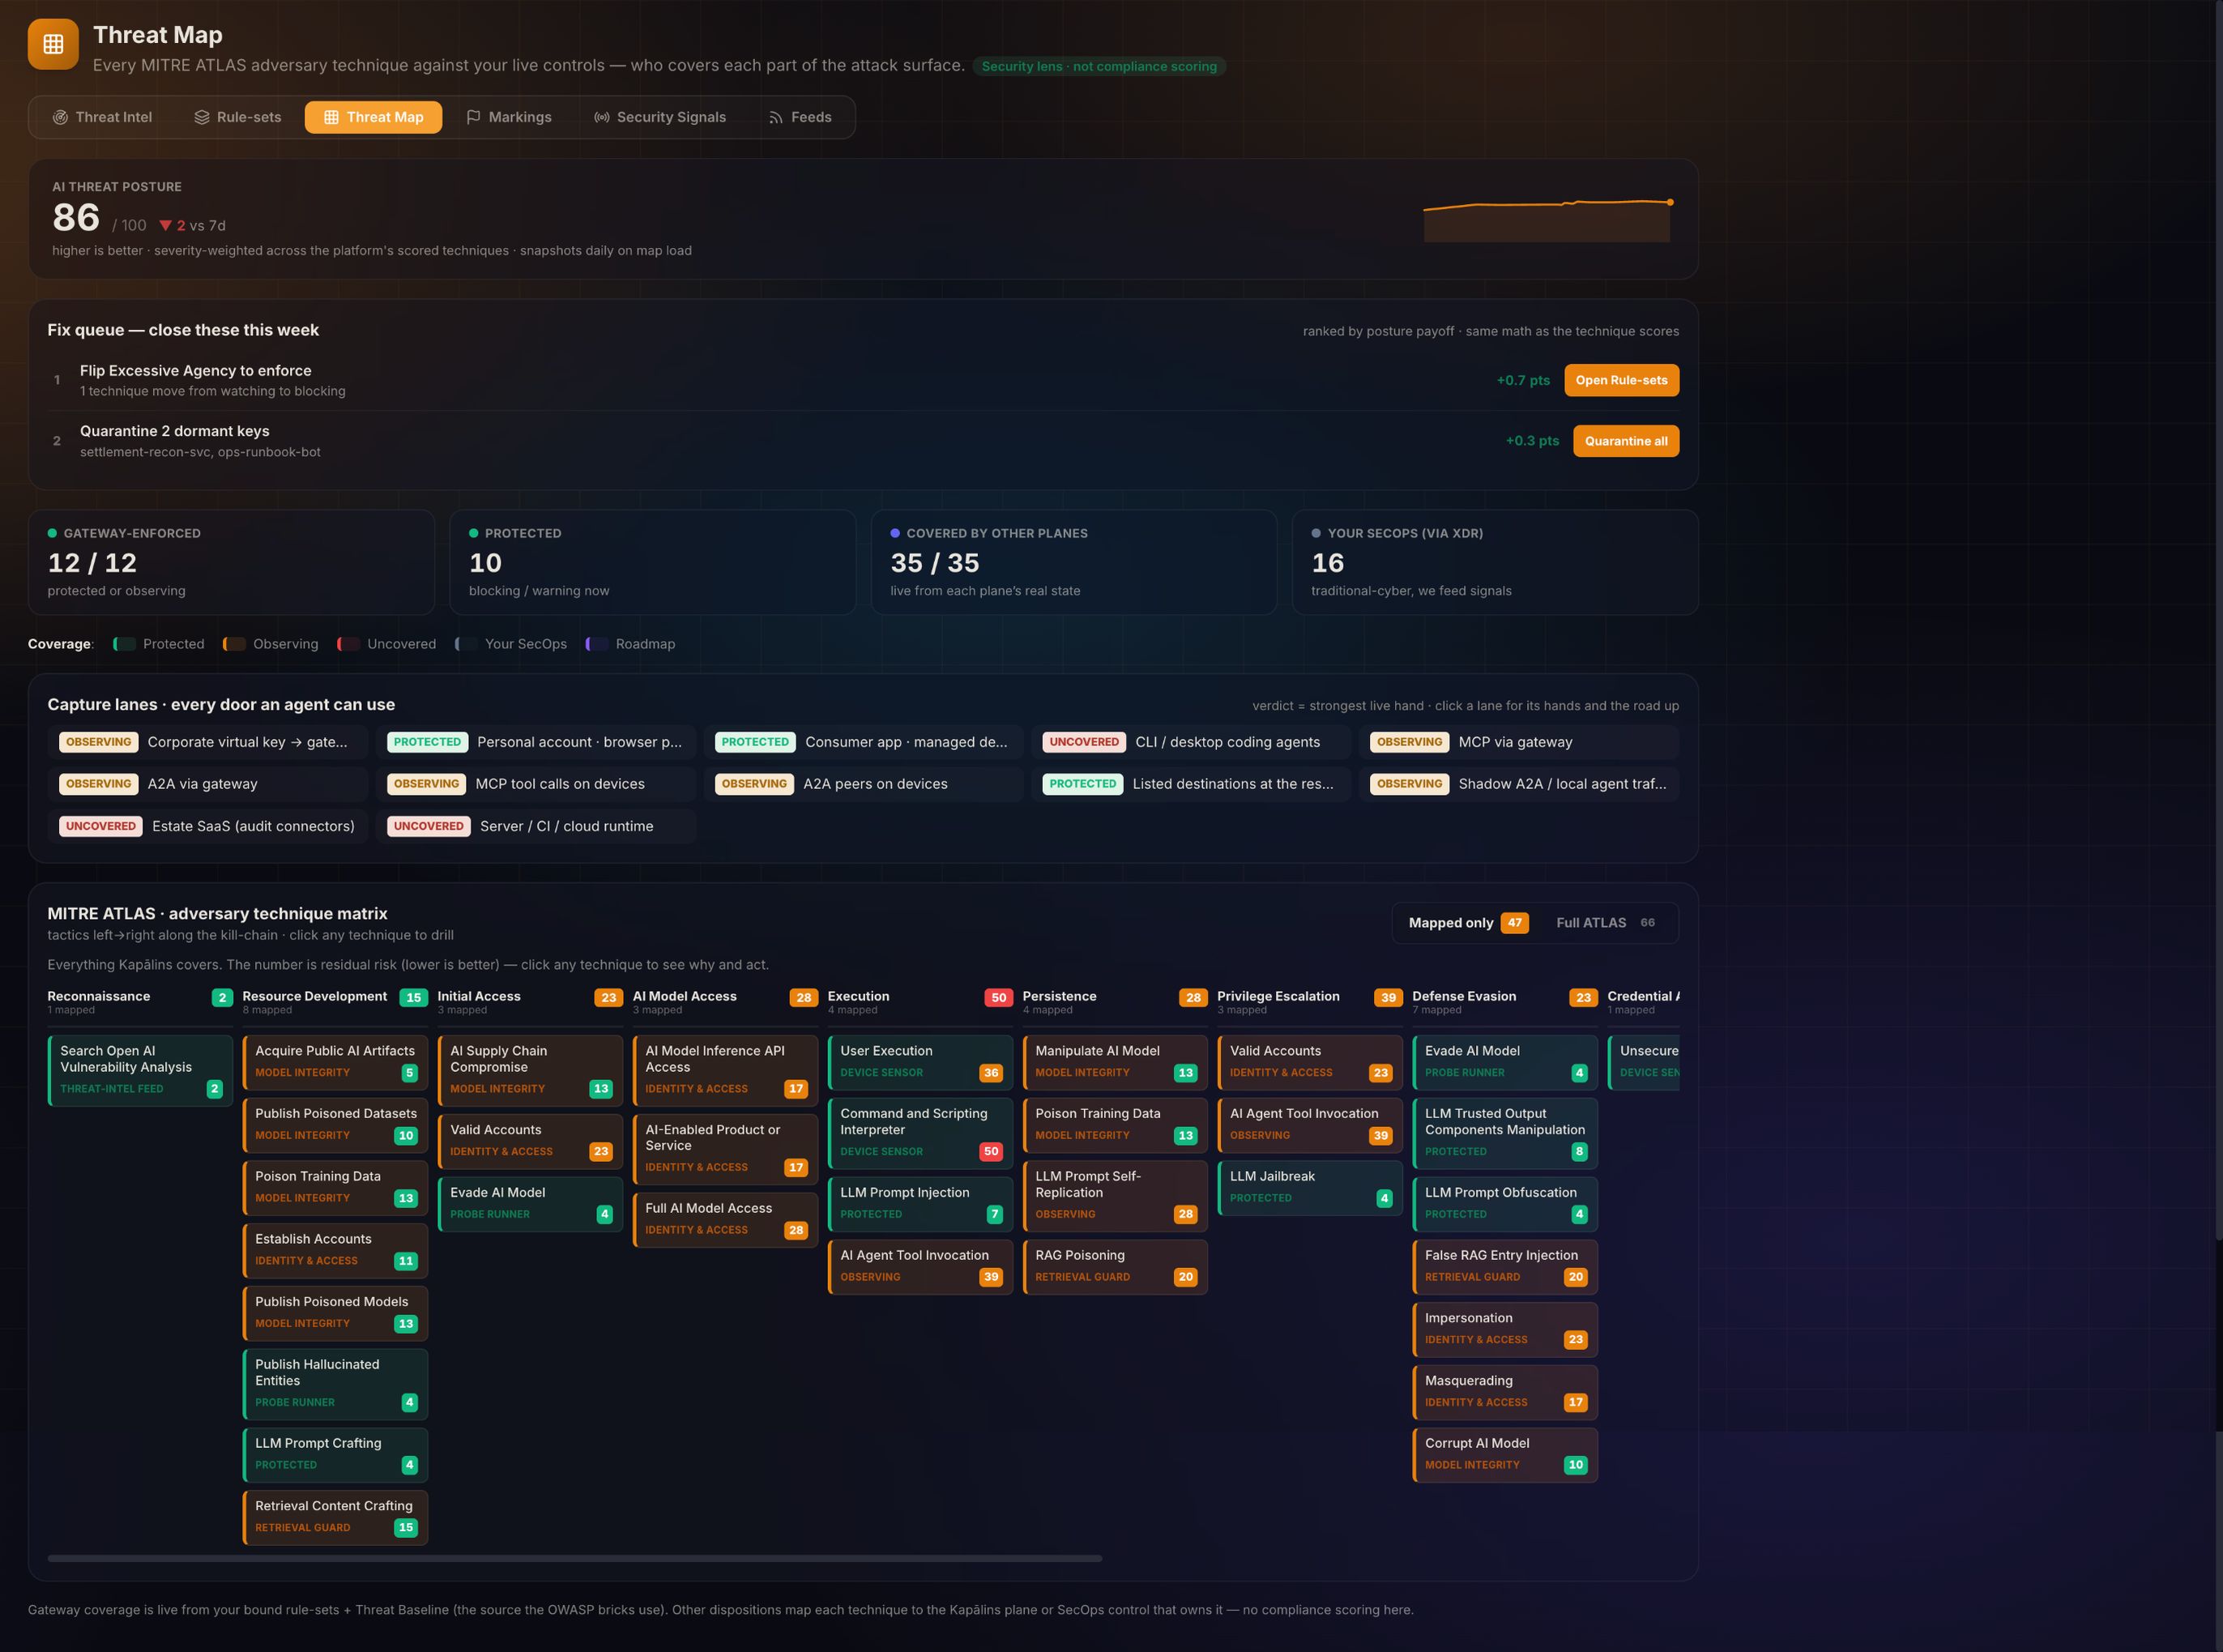
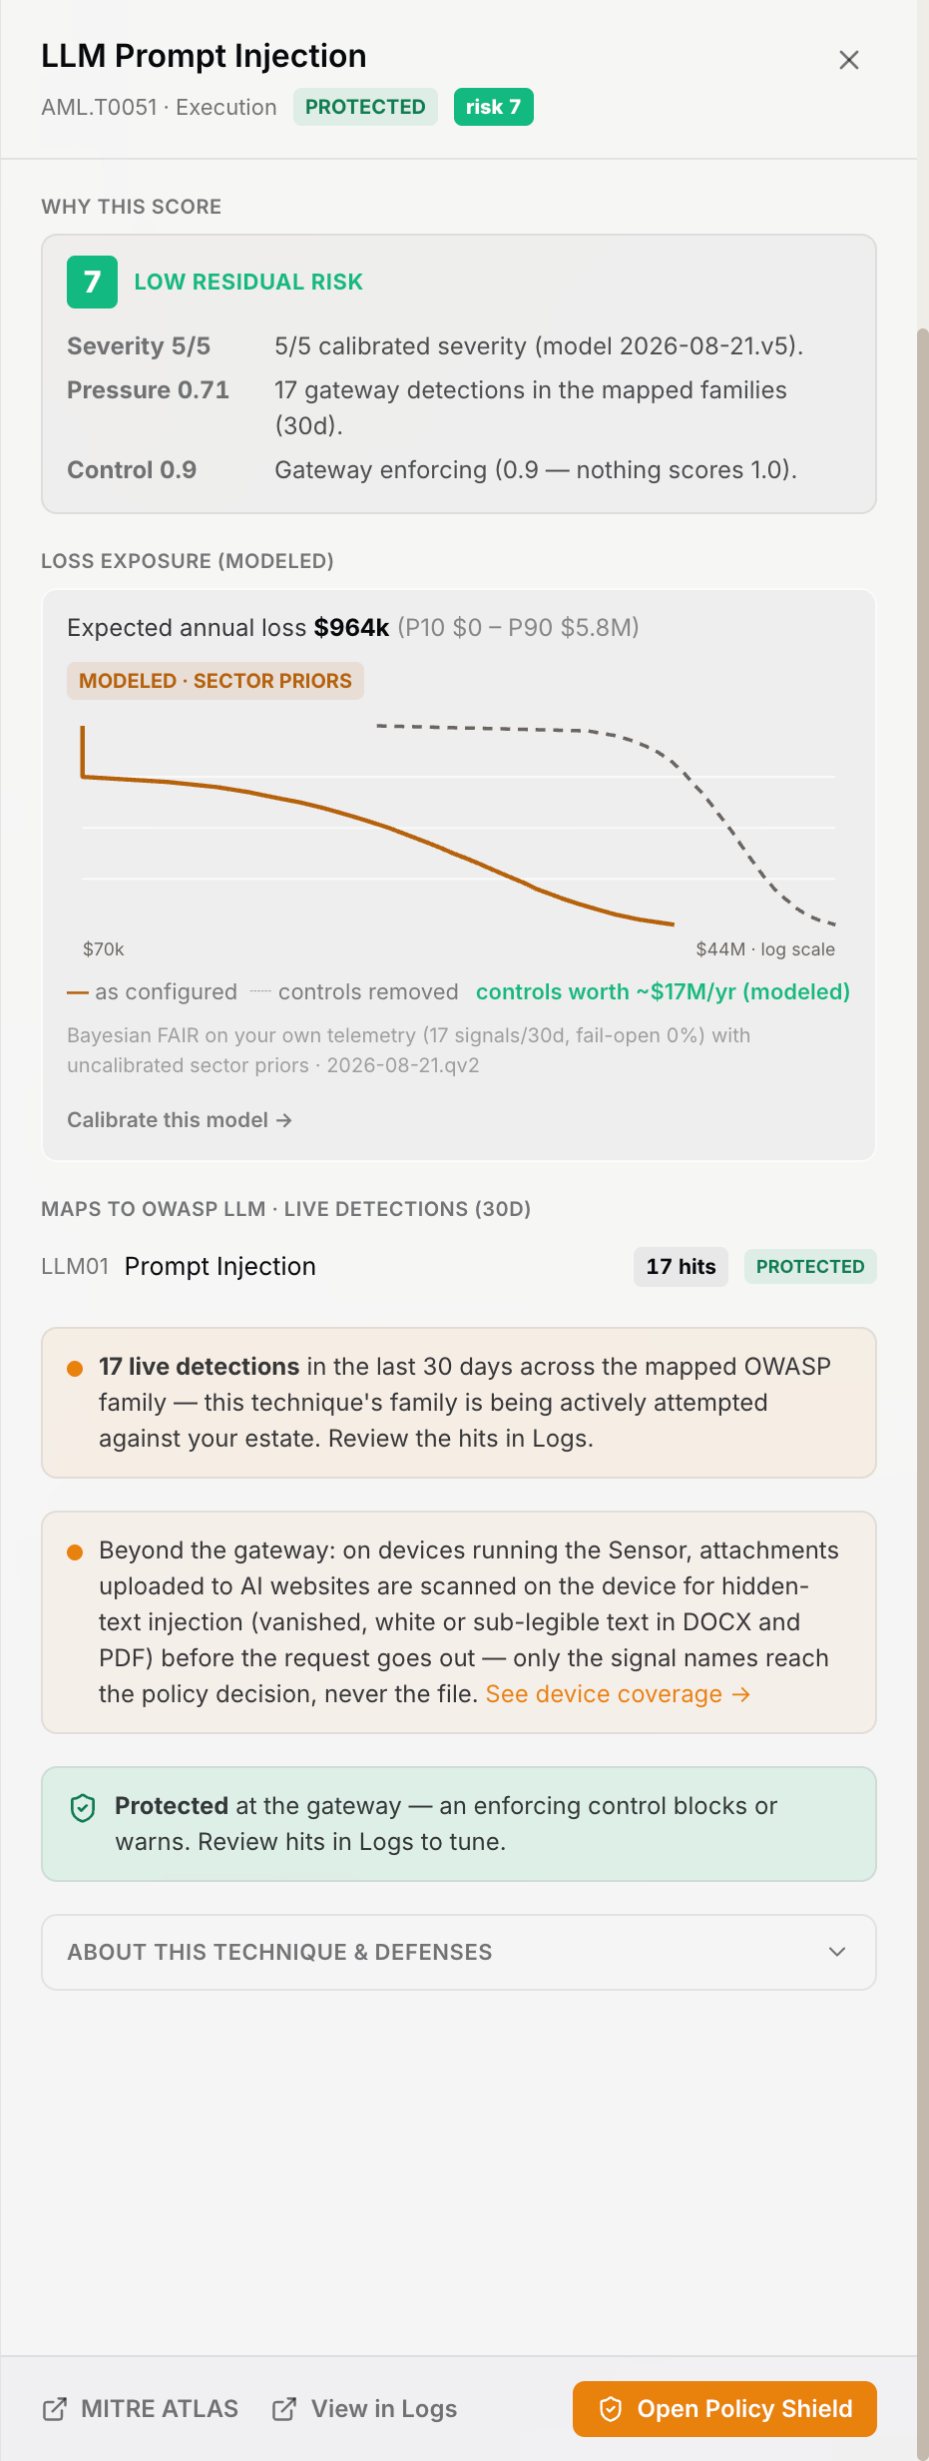
Mapped to the attack. Priced in dollars.
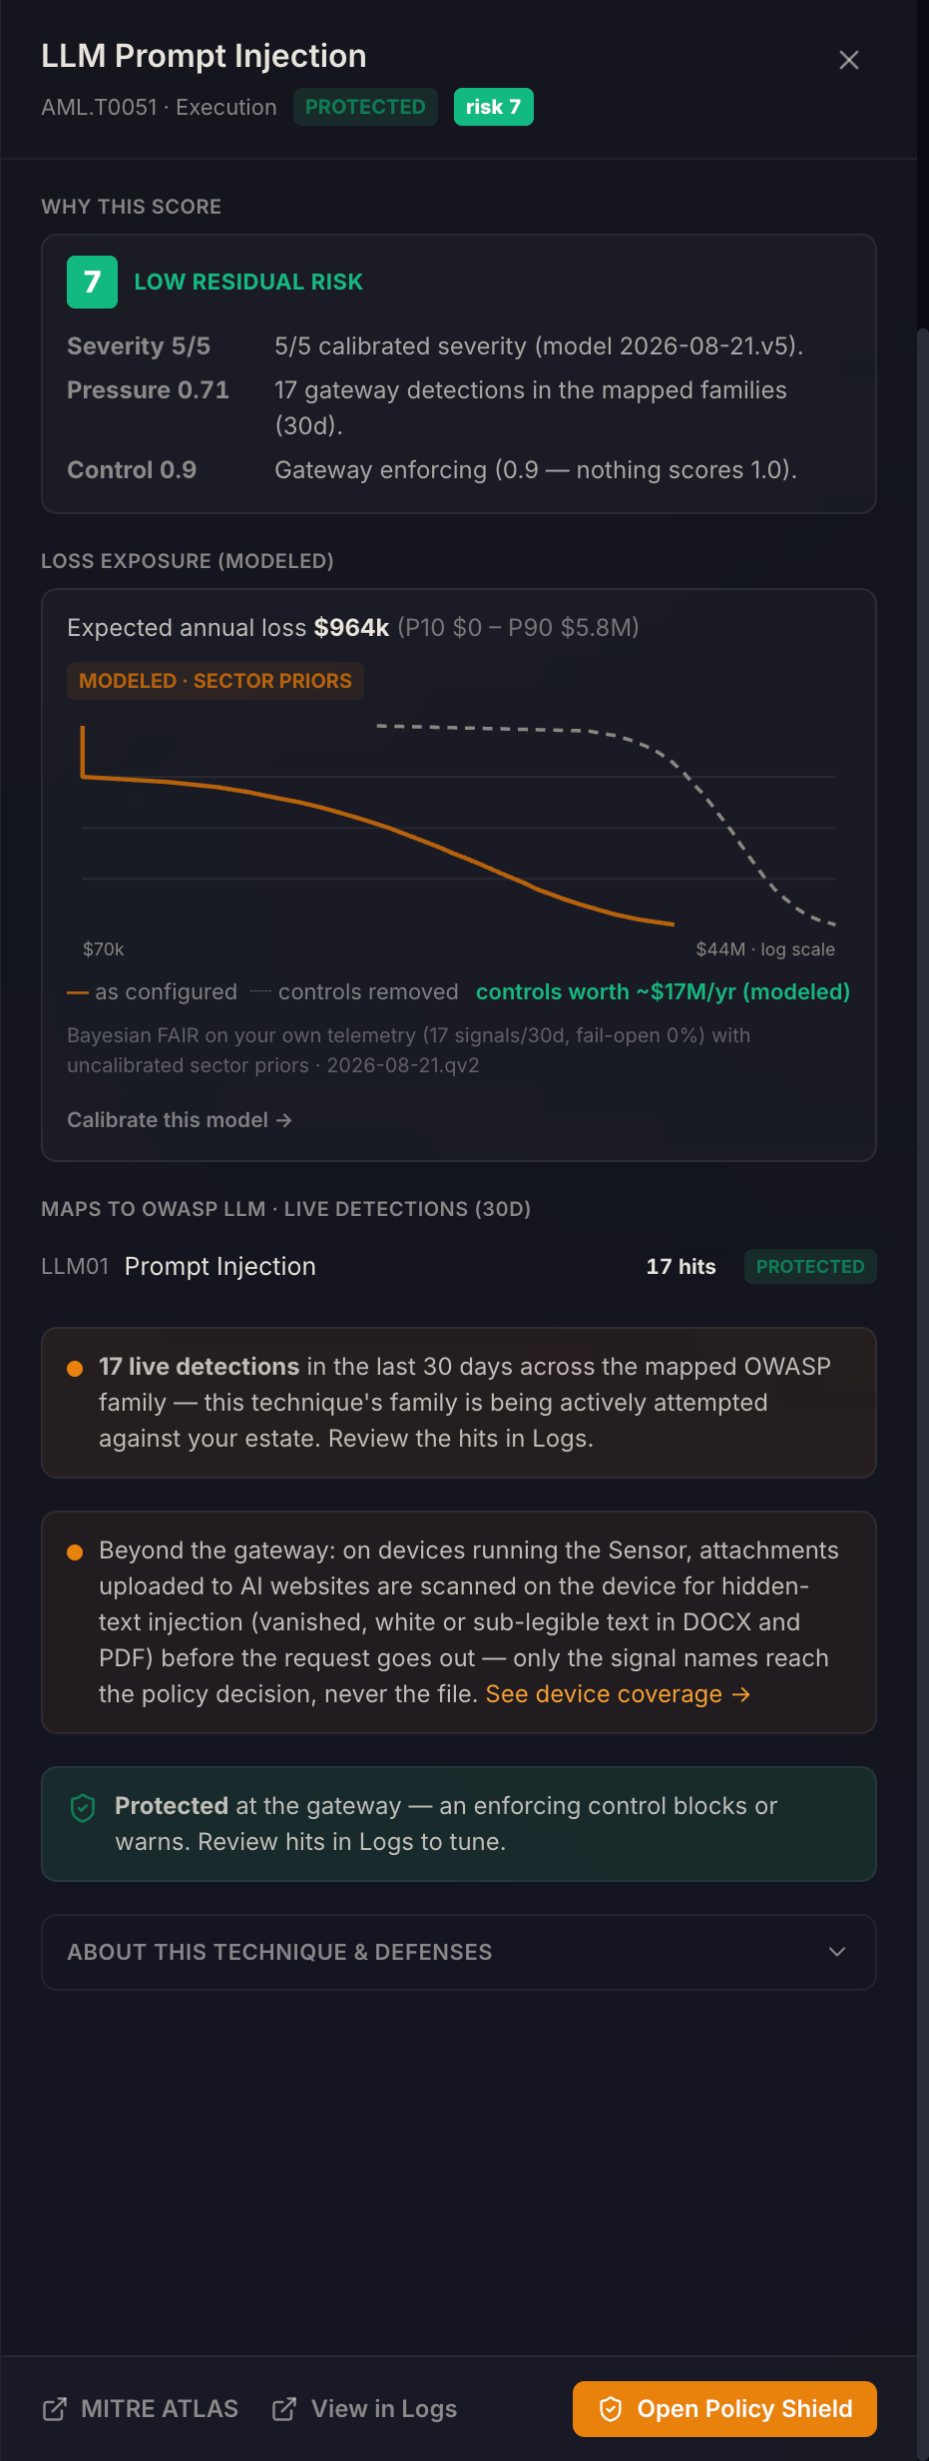
Every finding carries the MITRE ATLAS technique it belongs to and the plane that caught it. Click the technique and Kapālins shows its residual risk and a modelled annual loss, so the SOC can rank AI findings by what they could cost.
- Bayesian FAIR on your own telemetry, labelled as modelled
- Prompt injection, jailbreak, tool misuse, data exfiltration
Everything behind the finding.
The full record stays in Kapālins: the request, the verdict and the rule, so an analyst in Elastic can pivot to the evidence.
- Nothing is pulled from Elastic
Four steps.
- Create the destination credentialAn API key allowed to write to that data stream, and your Elasticsearch endpoint, created in Elastic.
- Add the destinationMy Integrations › Security operations › Elastic: paste the credential and endpoint. The connect page shows where to find each one.
- Send a testKapālins sends a test event and shows Elastic’s response; Connect unlocks when it passes.
- Watch the first events landEvery verdict from then on is sent as it happens, and each push is in the integration’s history.
See Elastic governed in thirty minutes.
Bring the person who holds the credential. We connect it live and watch the first events land.
Questions buyers ask.
Does Kapālins read anything from Elastic?
No. The integration is one-way: Kapālins pushes, nothing is pulled.
Which findings are sent?
Every verdict, as it happens, so Elastic holds the full record. Your own rules and searches decide what becomes an alert.
What if a push fails?
The attempt and Elastic’s response are recorded in the push log, and the integration shows the error until the next push succeeds.