Kapālins for ServiceNow
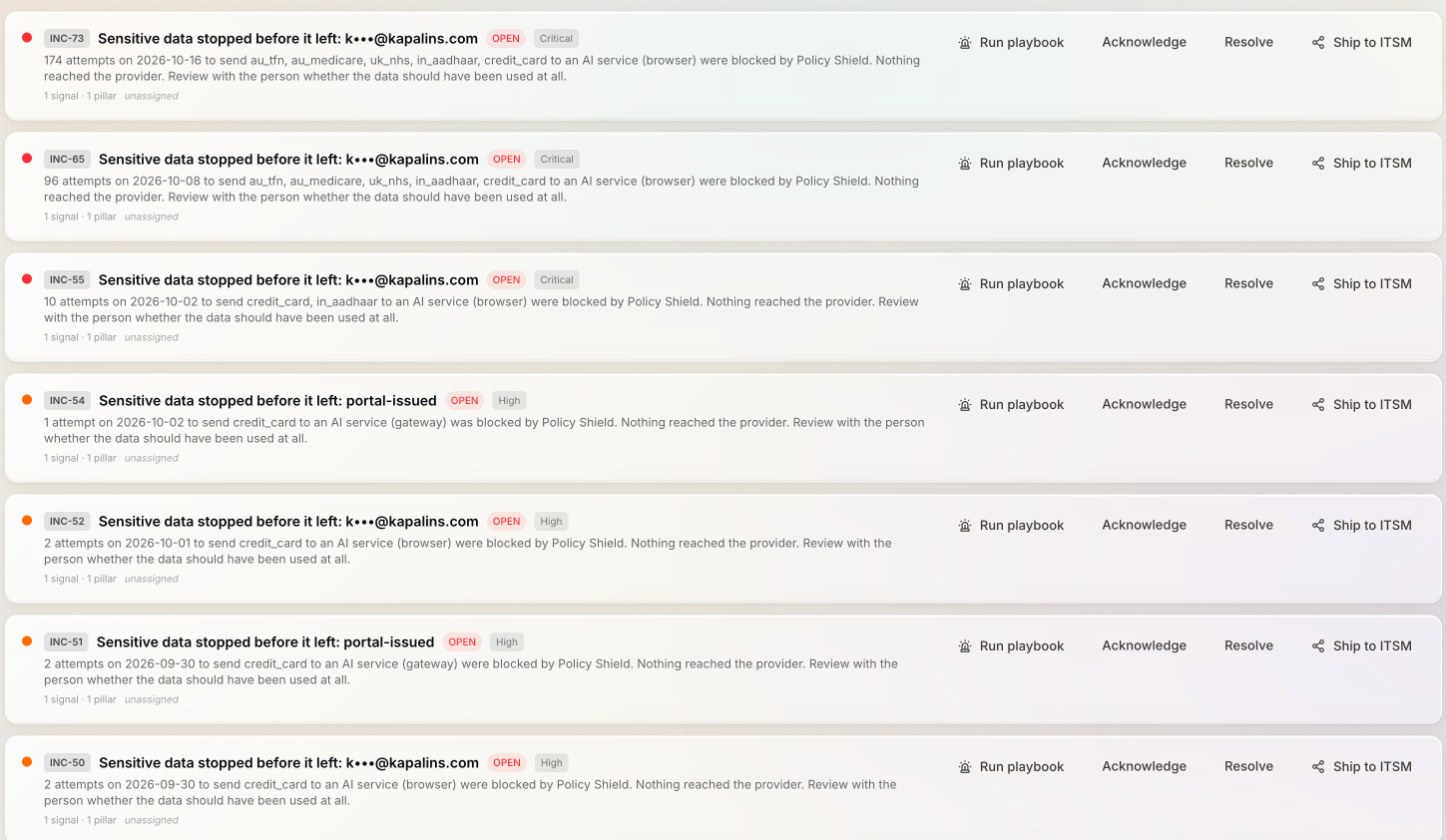
Your SOC keeps working in ServiceNow ITSM. Kapālins pushes every AI finding, block and incident there as the Table API, one incident per finding with severity mapped to priority 1 to 4, with the person, the rule and the evidence on each one.
No new console for the SOC
Analysts triage AI findings in ServiceNow, next to everything else, in its own field names.
AI-specific signal you do not have today
Prompt injection, sensitive data in prompts, unapproved models and agent tool calls, mapped to MITRE ATLAS before they arrive.
Every finding once
Deduplicated on the Kapālins event id, so a retry never doubles a ticket, and every attempt is in the push log.
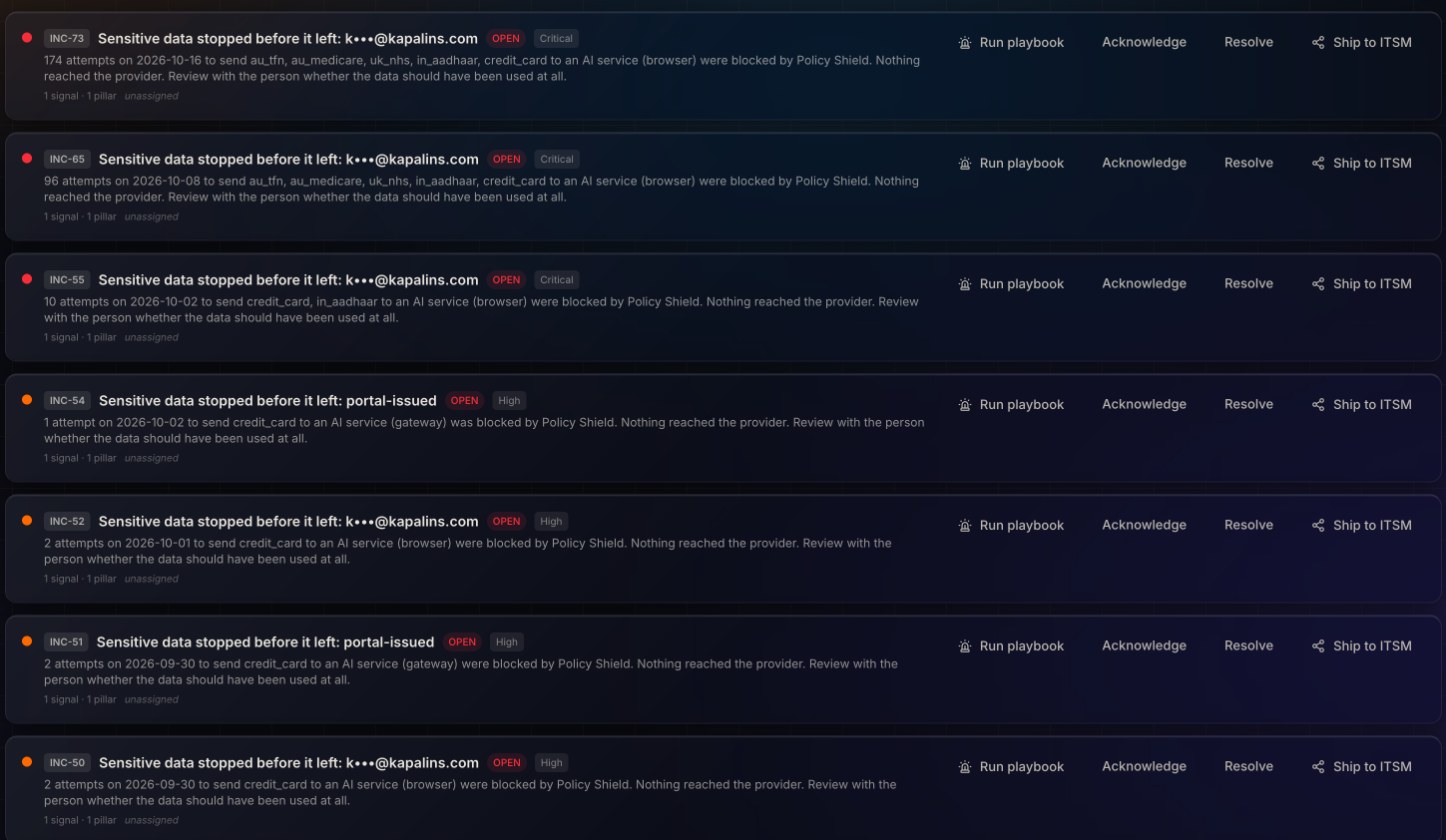
What lands in ServiceNow.
Each incident carries its severity, the person, the rule that fired, what was stopped, and a link back to the evidence. "Ship to ITSM" on the card sends it on demand; findings you choose are pushed as they happen.
- Sent as the Table API, one incident per finding with severity mapped to priority 1 to 4
- Credential: an instance user allowed to create incidents
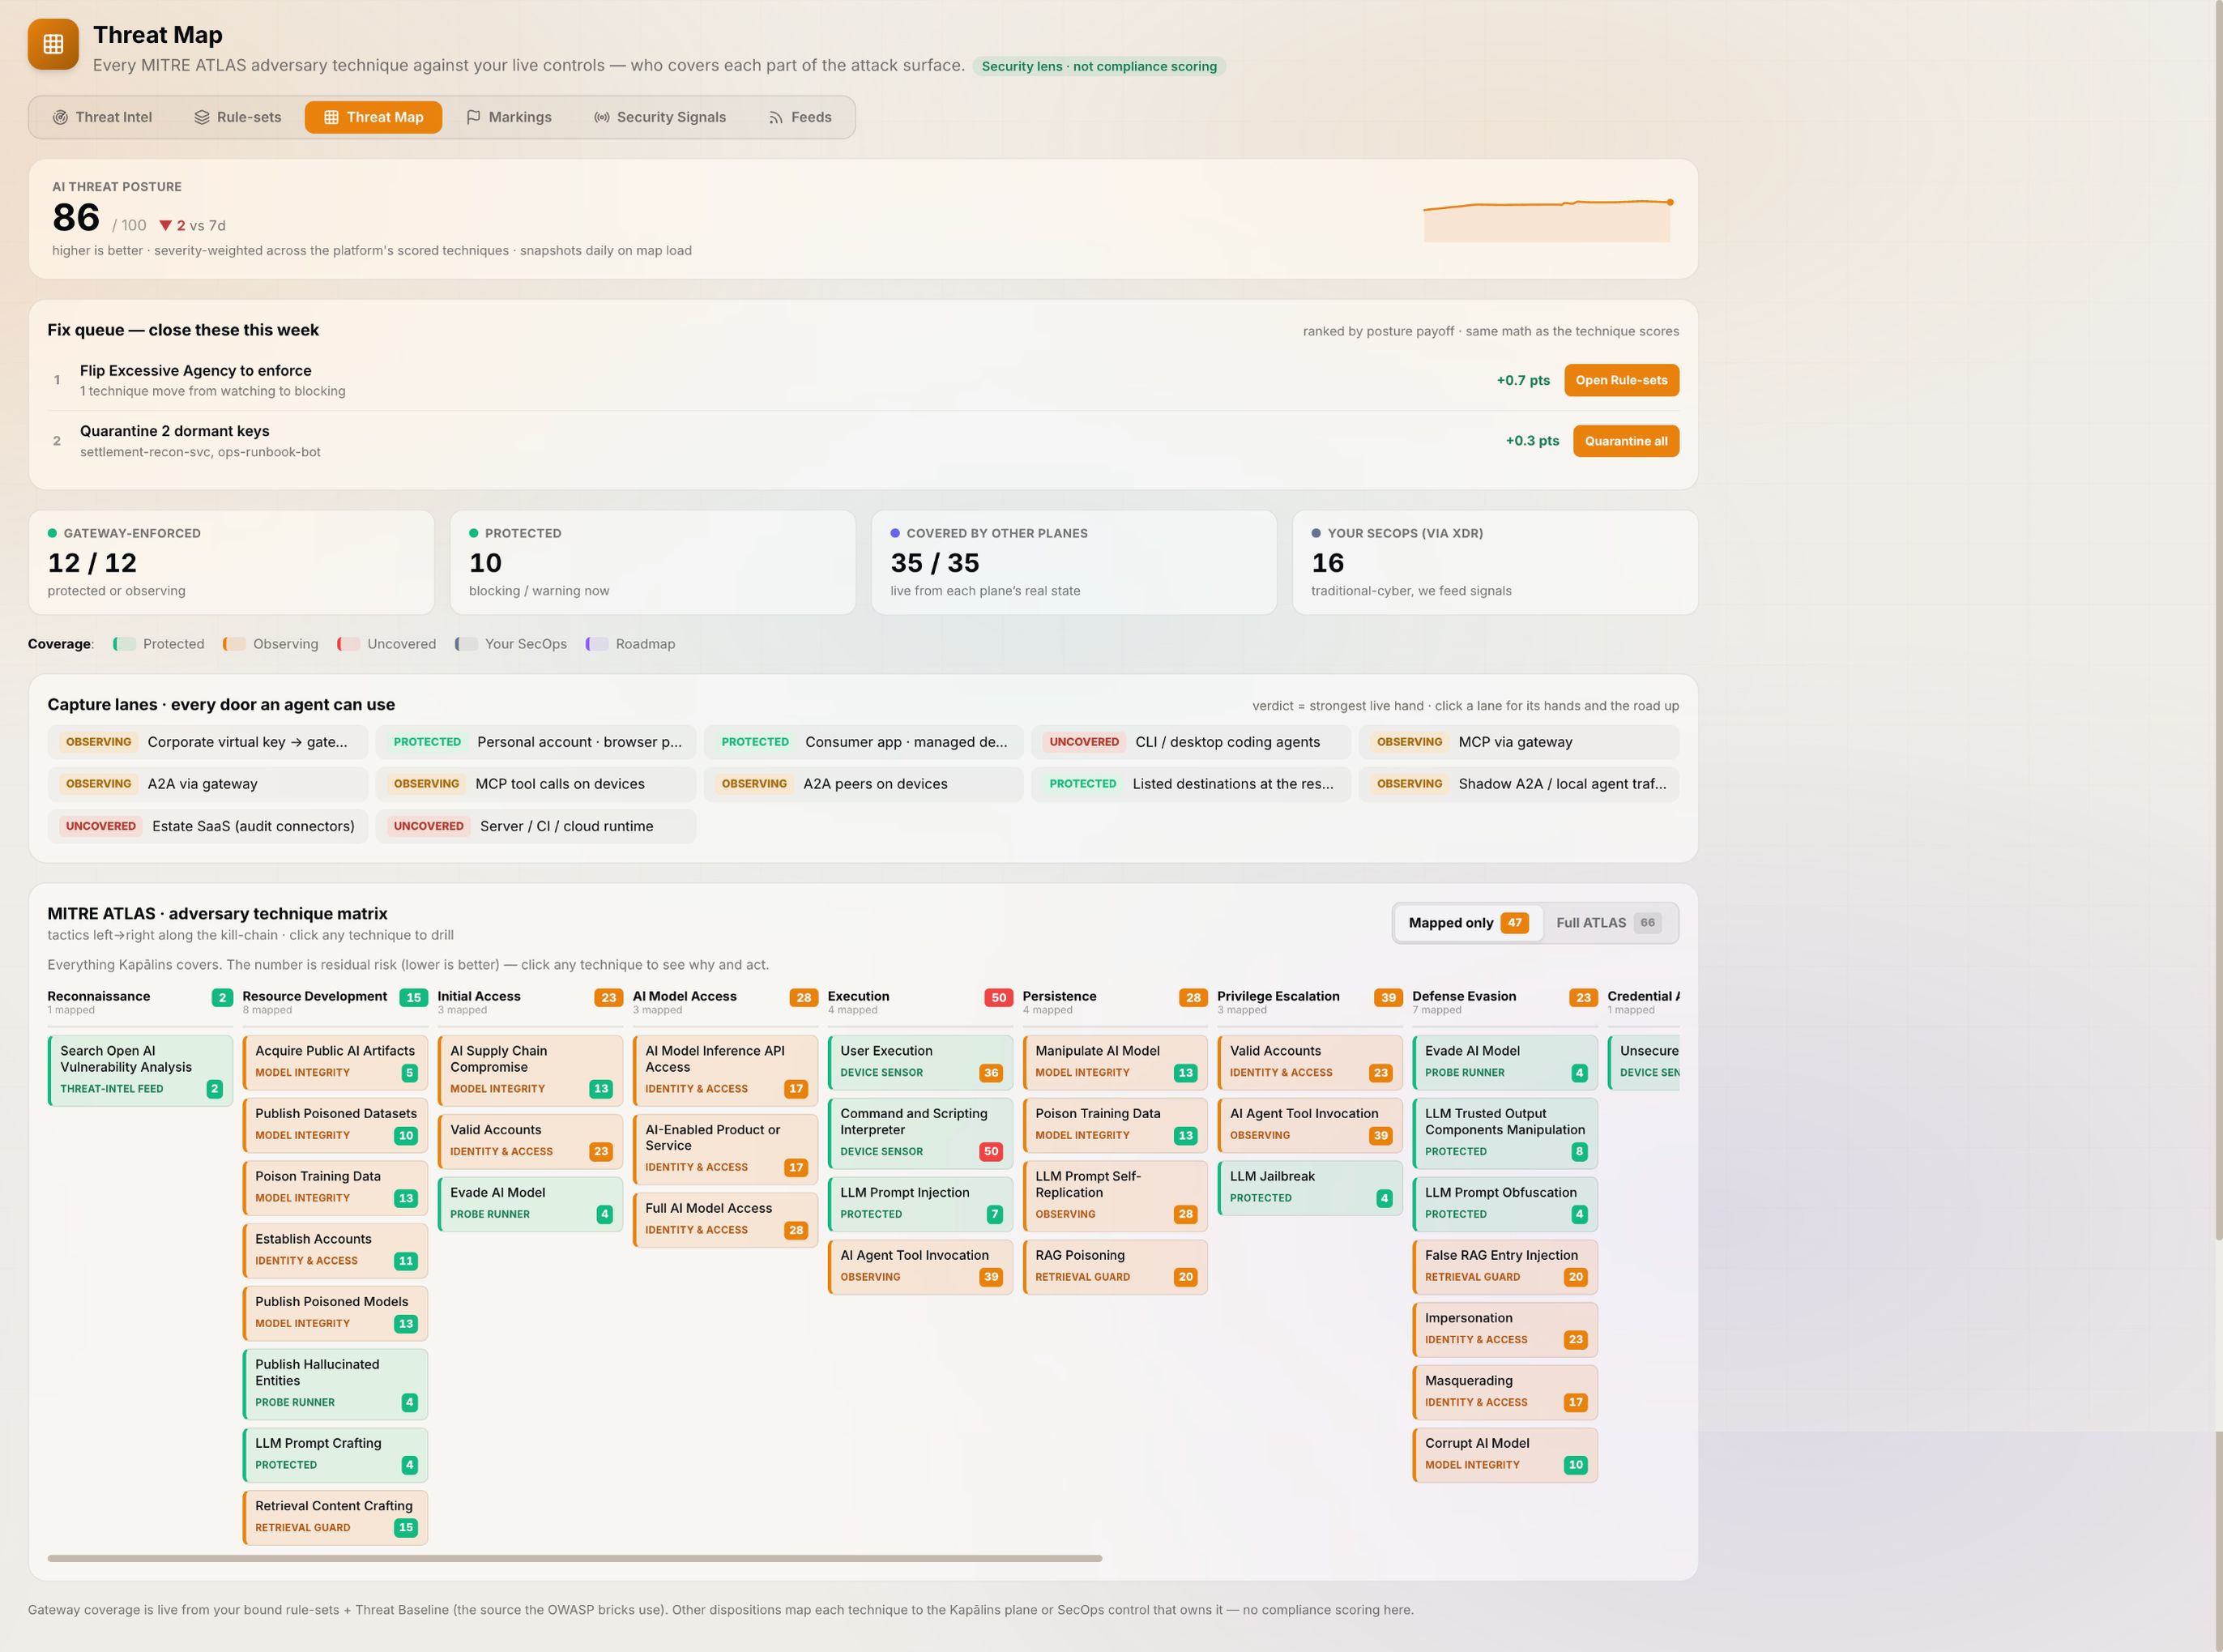
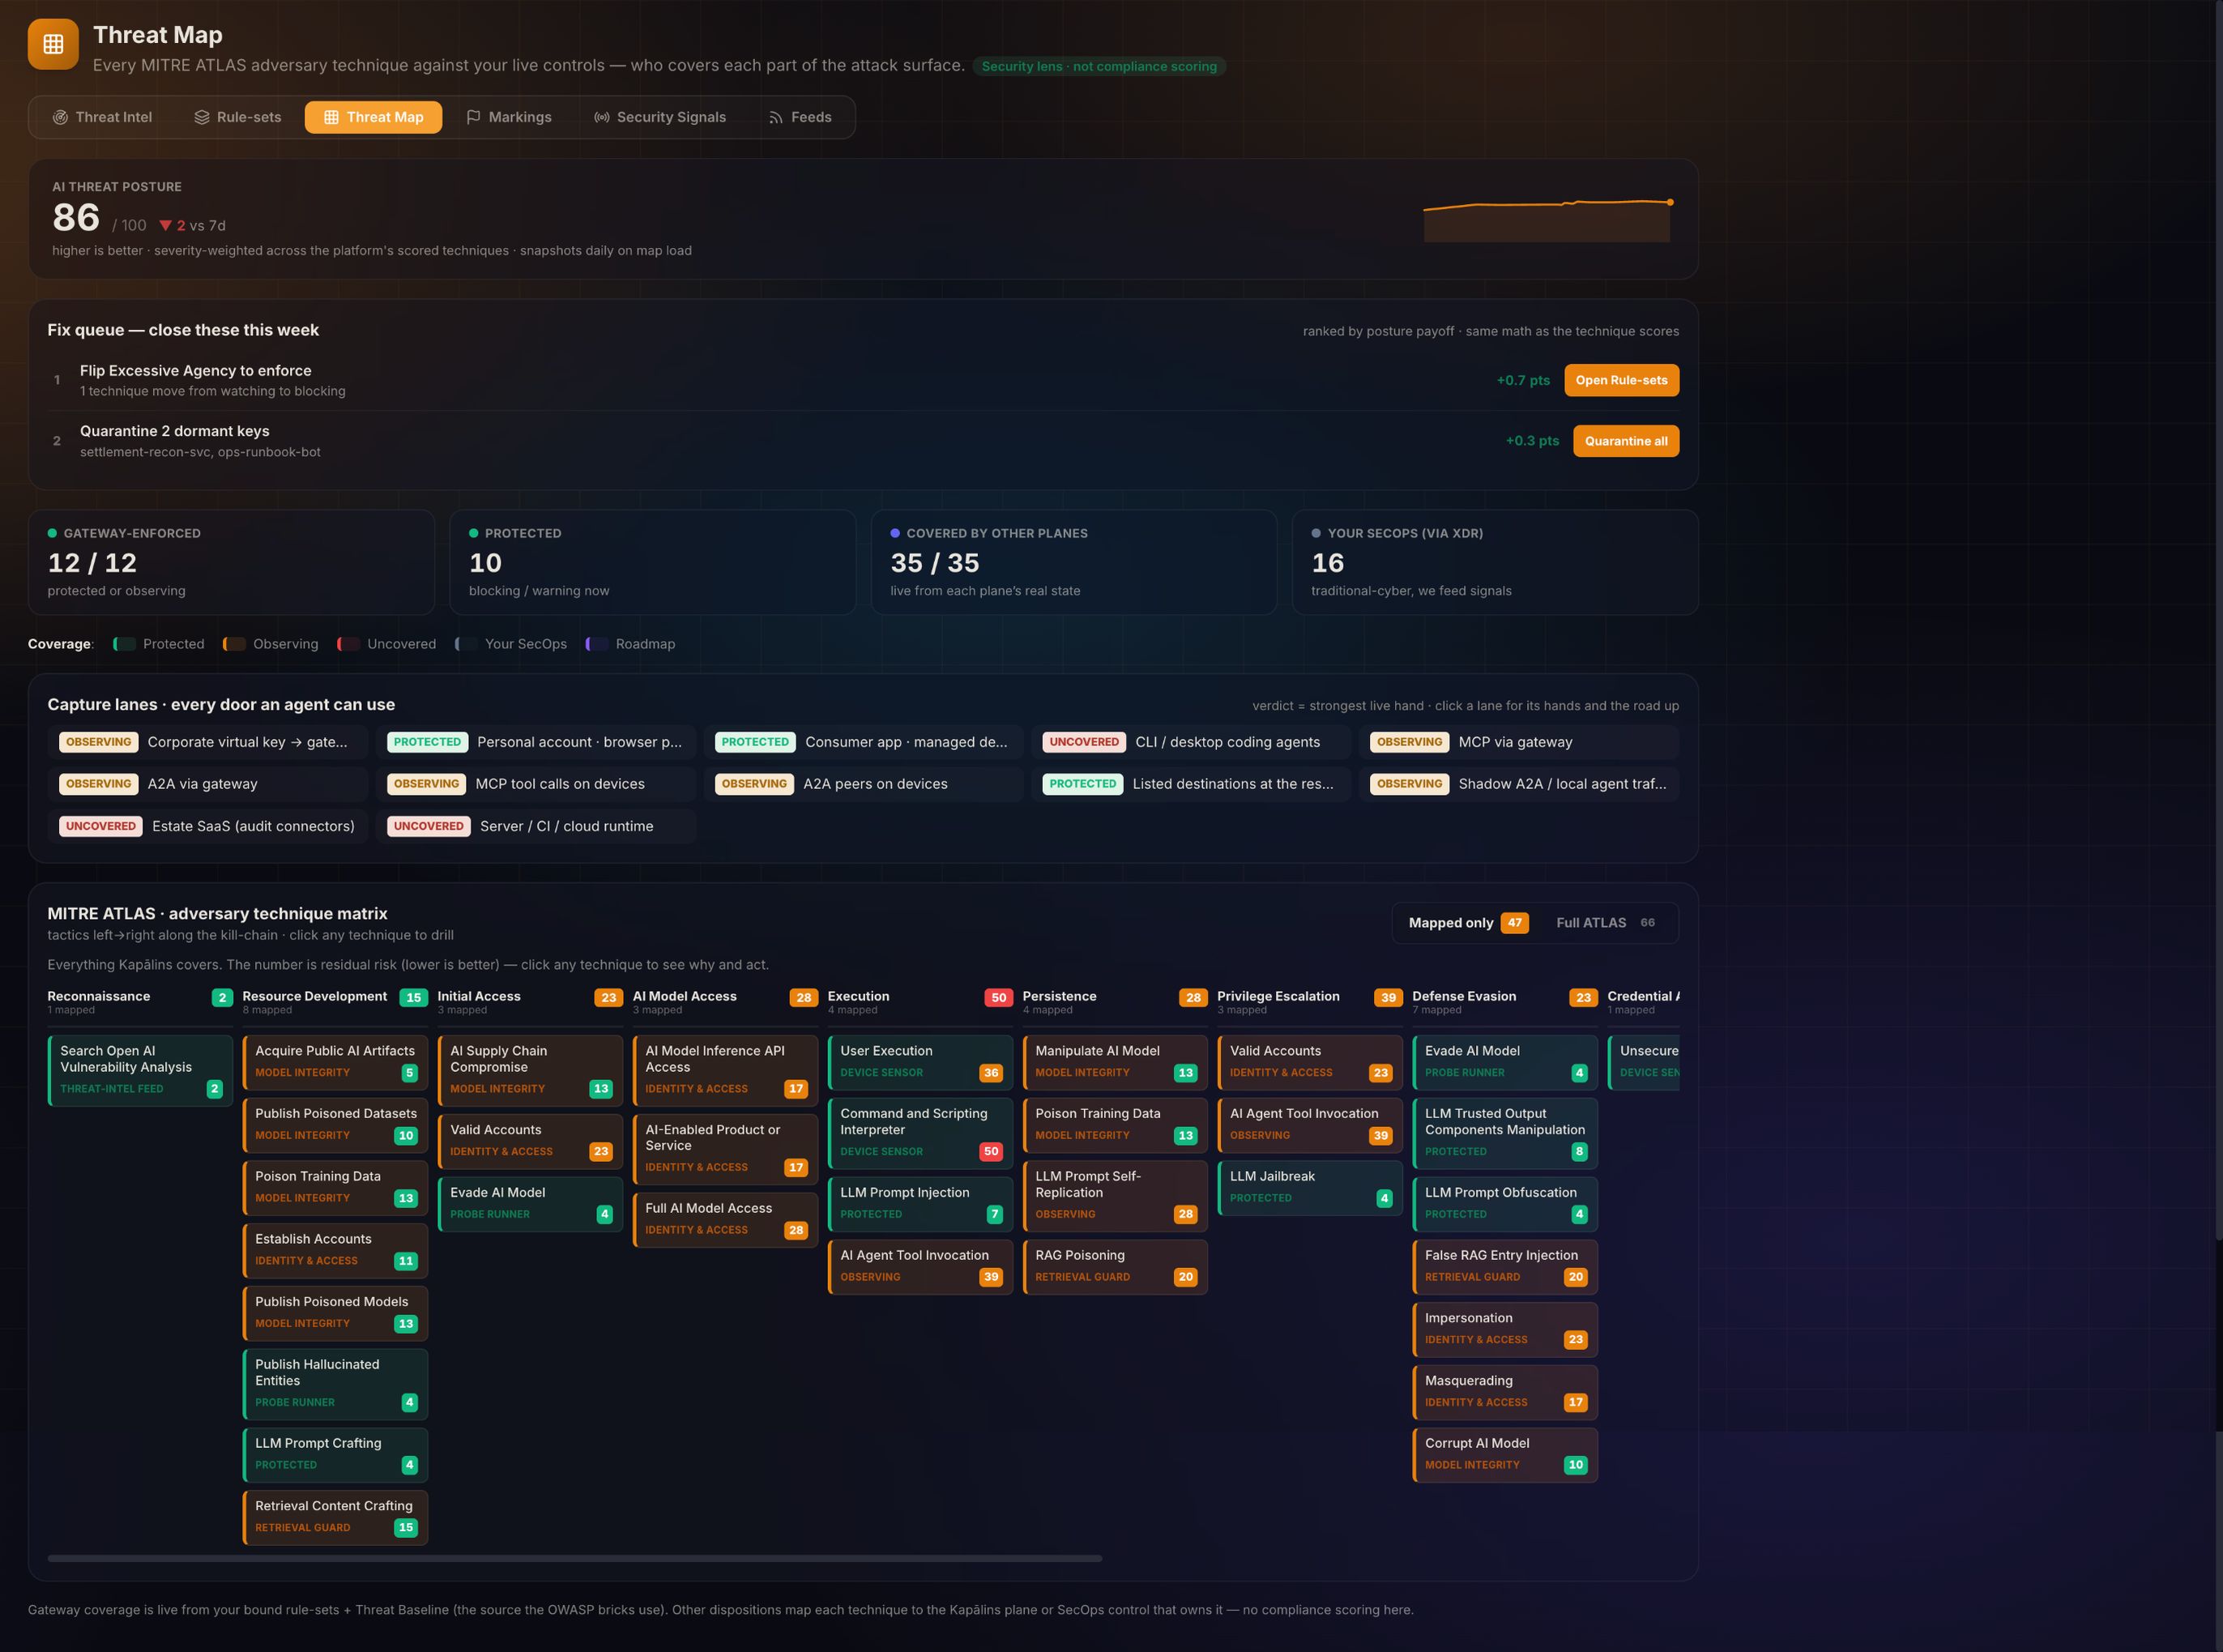
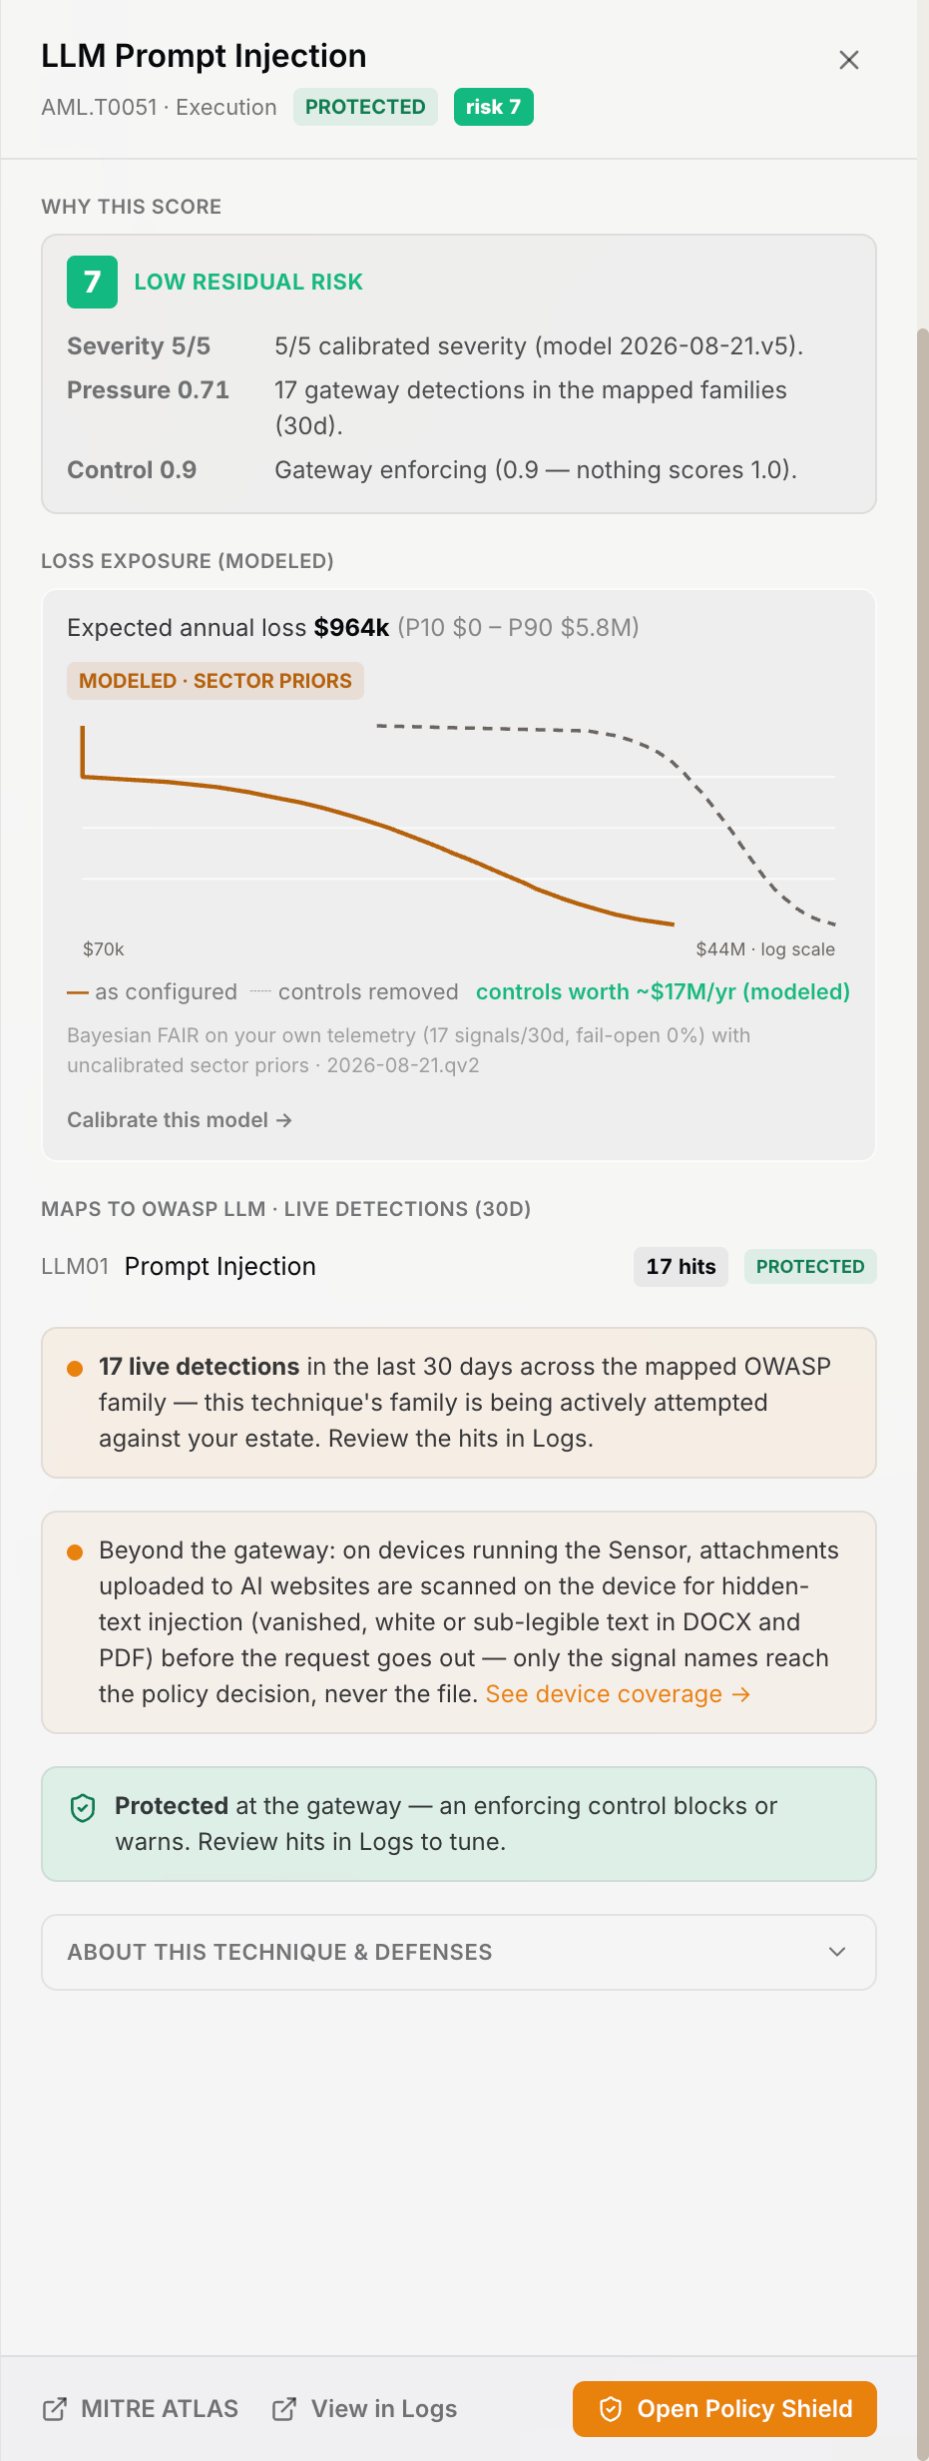
Mapped to the attack. Priced in dollars.
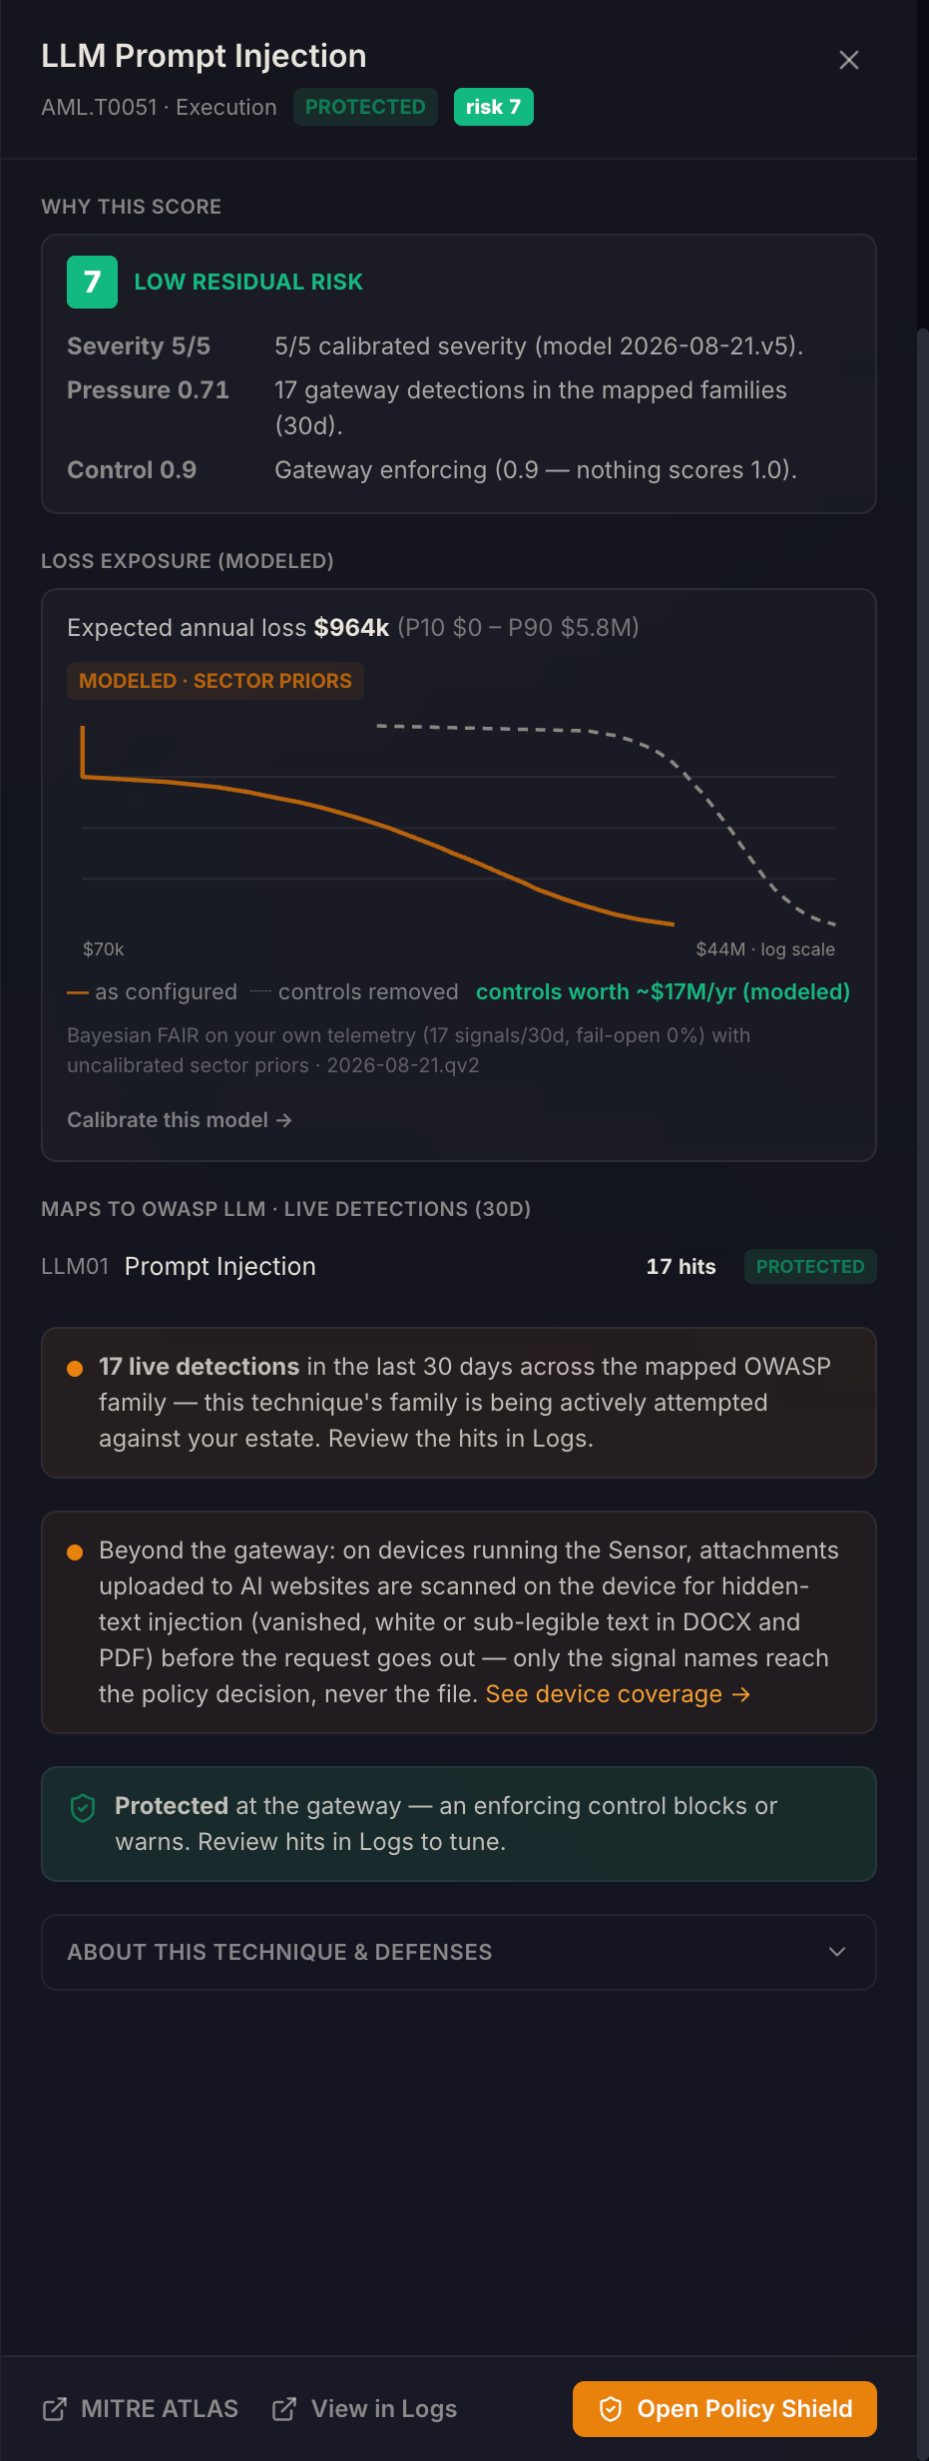
Every finding carries the MITRE ATLAS technique it belongs to and the plane that caught it. Click the technique and Kapālins shows its residual risk and a modelled annual loss, so the SOC can rank AI findings by what they could cost.
- Bayesian FAIR on your own telemetry, labelled as modelled
- Prompt injection, jailbreak, tool misuse, data exfiltration
Everything behind the finding.
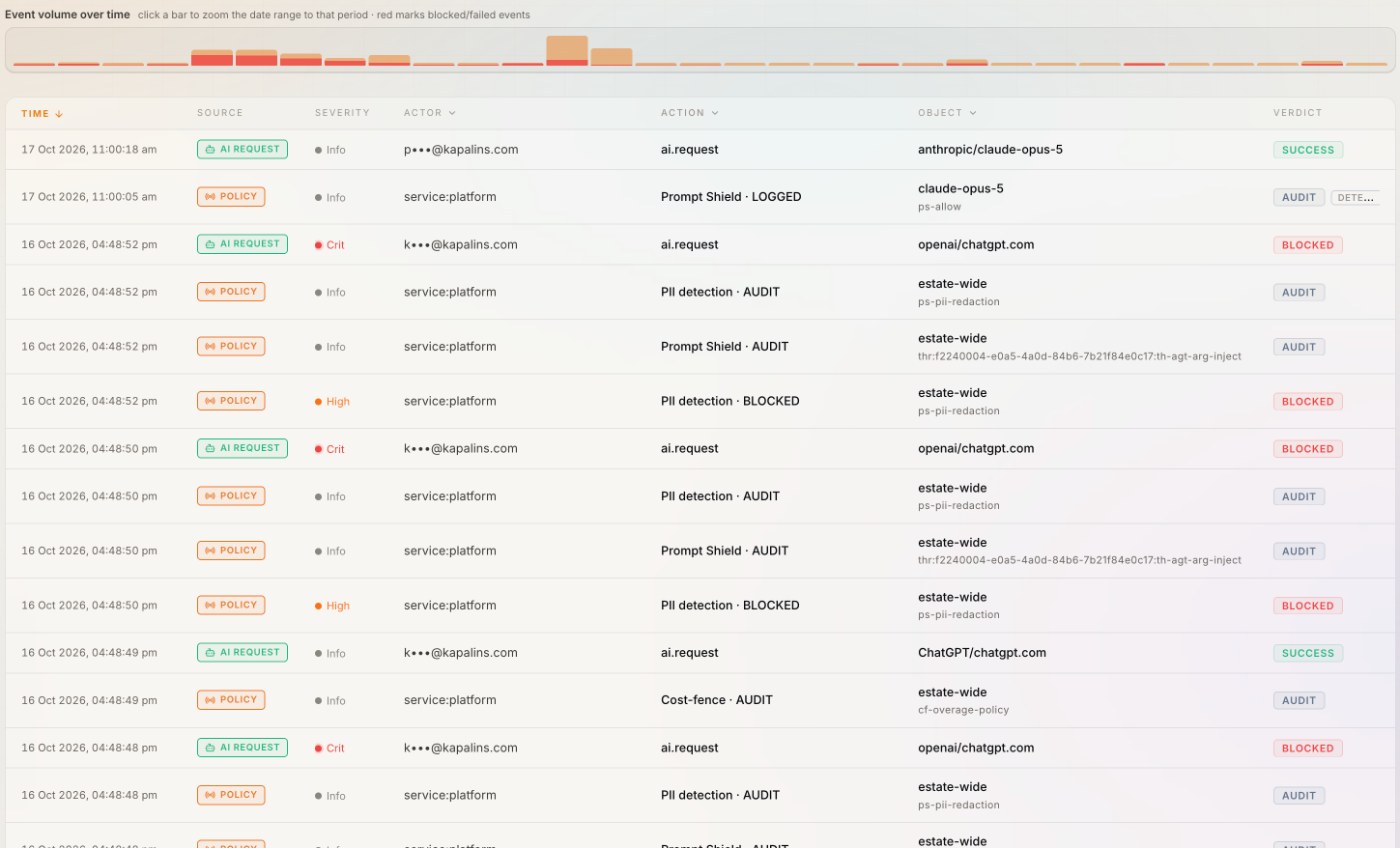
The full record stays in Kapālins: the request, the verdict and the rule, so an analyst in your SIEM can pivot to the evidence.
- Nothing is pulled from your SIEM
Four steps.
- Create the destination credentialAn instance user allowed to create incidents, created in ServiceNow.
- Add the destinationSecurity operations › ServiceNow › paste the credential and endpoint.
- Choose what to pushFindings, blocks or incidents, with a minimum severity.
- Send a testKapālins pushes a test event and shows the response.
See ServiceNow governed in thirty minutes.
Bring the person who holds the credential. We connect it live and watch the first events land.
Questions buyers ask.
Does Kapālins read anything from ServiceNow?
No. The integration is one-way: Kapālins pushes, nothing is pulled.
Can I limit what is pushed?
Yes. Choose the finding types and the minimum severity; the rest stays in Kapālins.
What if a push fails?
The attempt and the response are recorded in the push log and shown on the integration; the next attempt retries it.