Kapālins for Claude Enterprise
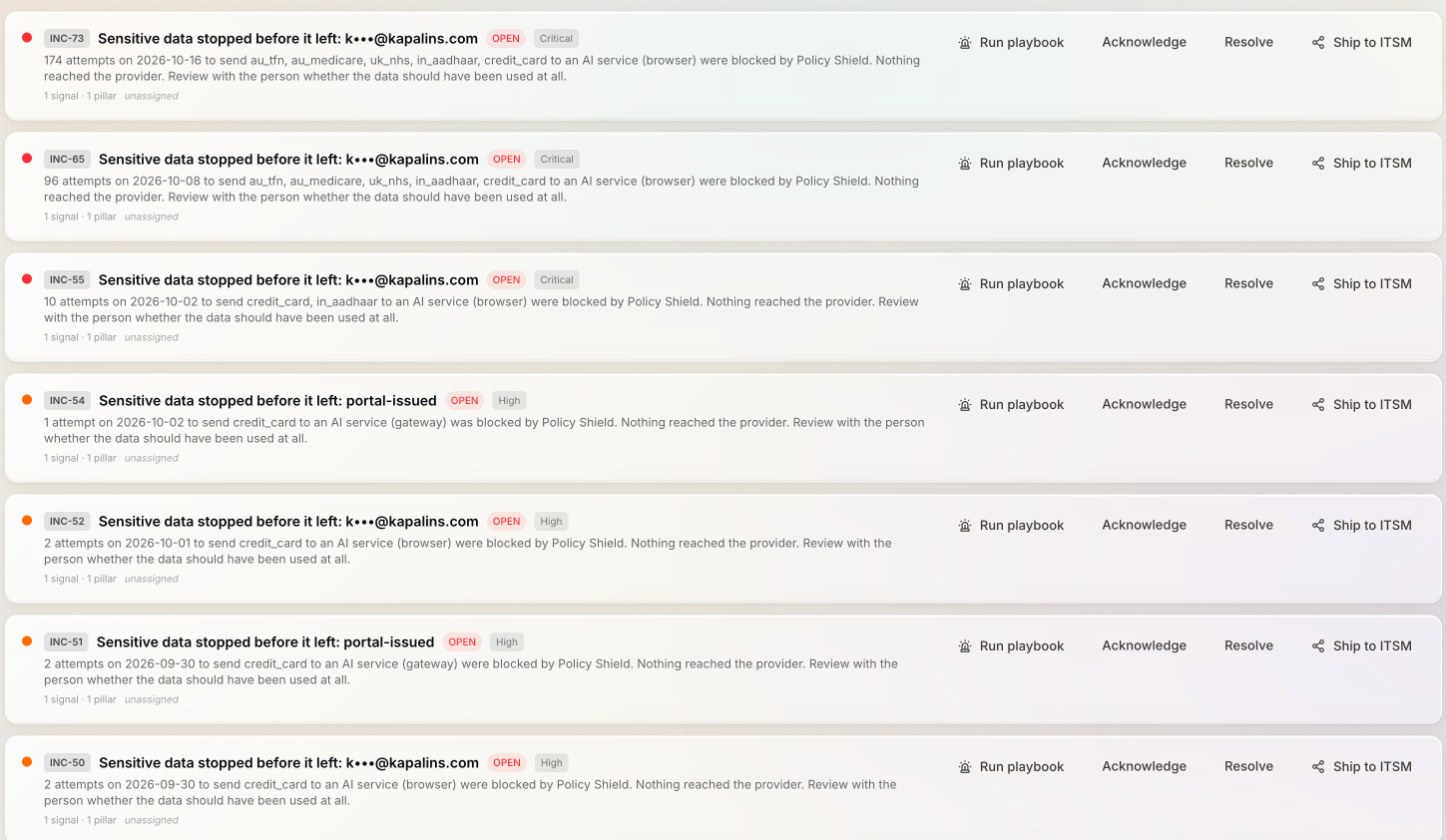
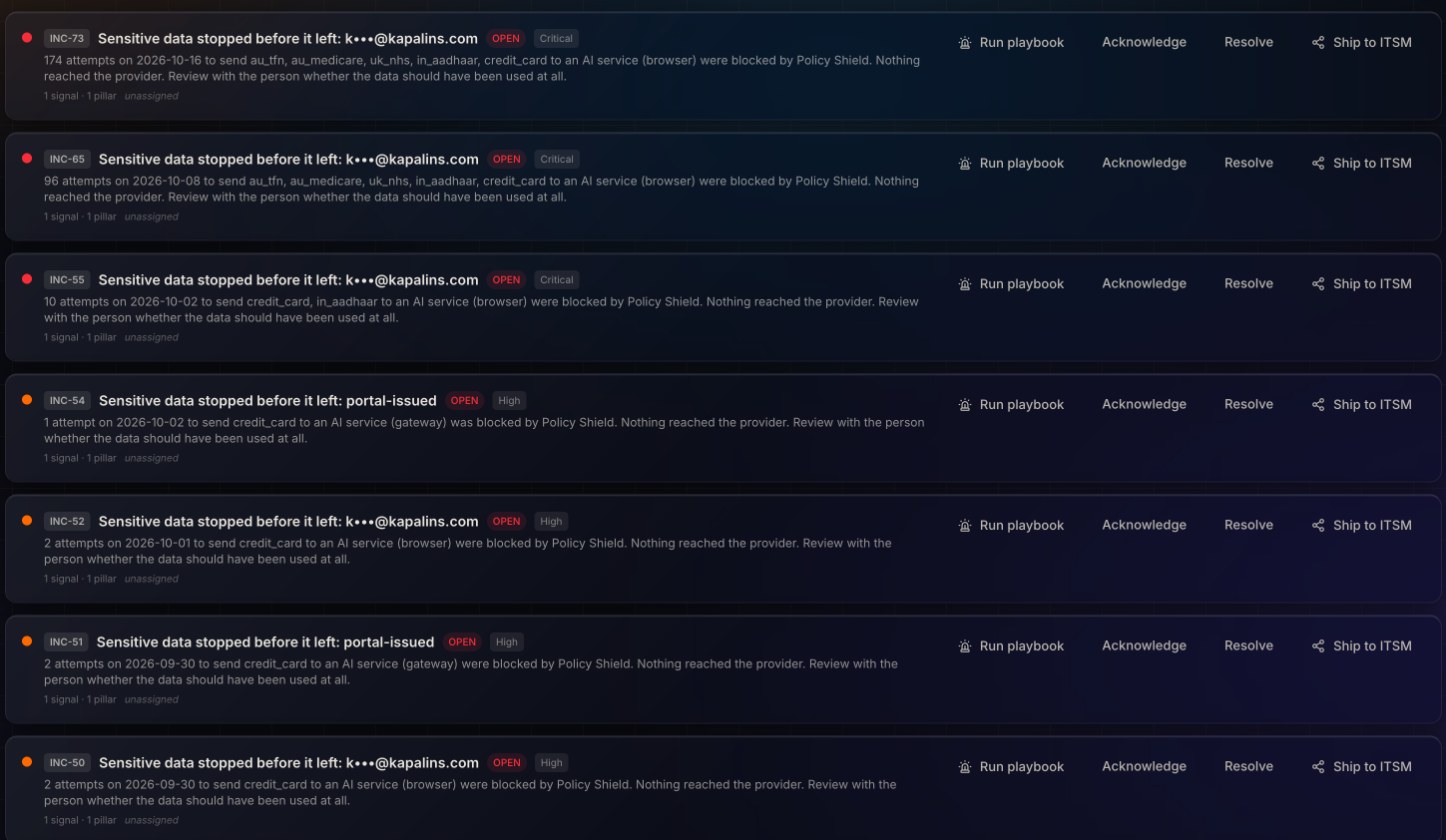
Claude is the AI your people use most, and the one no gateway can sit in front of. Kapālins decides each prompt before Claude runs it, and puts every Claude activity in the same timeline, incident queue and evidence chain as the rest of your estate.

Stop it before the model
Anthropic asks Kapālins first. A prompt or tool call that breaks your policy is denied, and the person is told why.
Every activity, one timeline
Sign-ins, chats, uploads, exports and admin changes, attributed to a person, beside gateway and device events.
Evidence an auditor accepts
Anthropic’s denial record carries the Kapālins verdict id, so the two records can be walked in either direction.
Claude Enterprise, governed in ninety seconds.
One Compliance Access Key, verified live with Anthropic. Every Claude admin action in one timeline, a weakened governance setting flagged within minutes, the incident with its notification clocks, and the evidence pack an auditor reads.
The Claude API, through one door.
Your Claude API key connected once and never handed out. One virtual key and endpoint for every team, any Anthropic SDK or Claude Code governed, customer details caught before they leave, and the routing reason on every request.
A verdict before Claude runs the prompt.
Each governed prompt from claude.ai, Cowork, Claude Code and Claude in Slack reaches Kapālins before inference. The same 32 Policy Shield rules and 57 sensitive-data patterns that guard your gateway and your browsers answer allow or deny in under 2.5 seconds. With Validate tool calls on, Claude’s tool calls are judged too.
- Shadow mode first: verdicts on live traffic, nobody blocked
- A reason the person can act on, plus your standing message
- Signed, deduplicated, and measured against Anthropic’s timeout
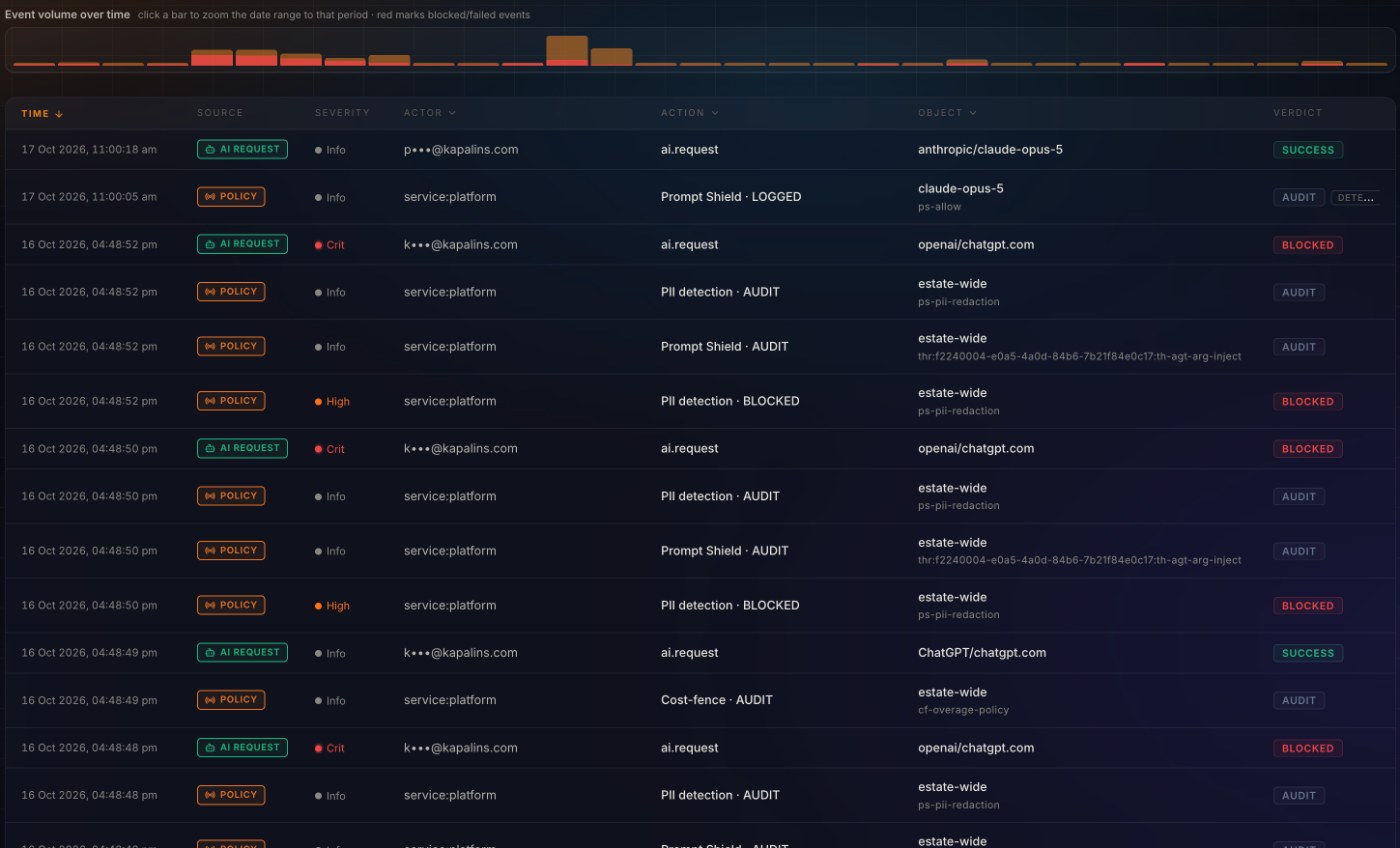
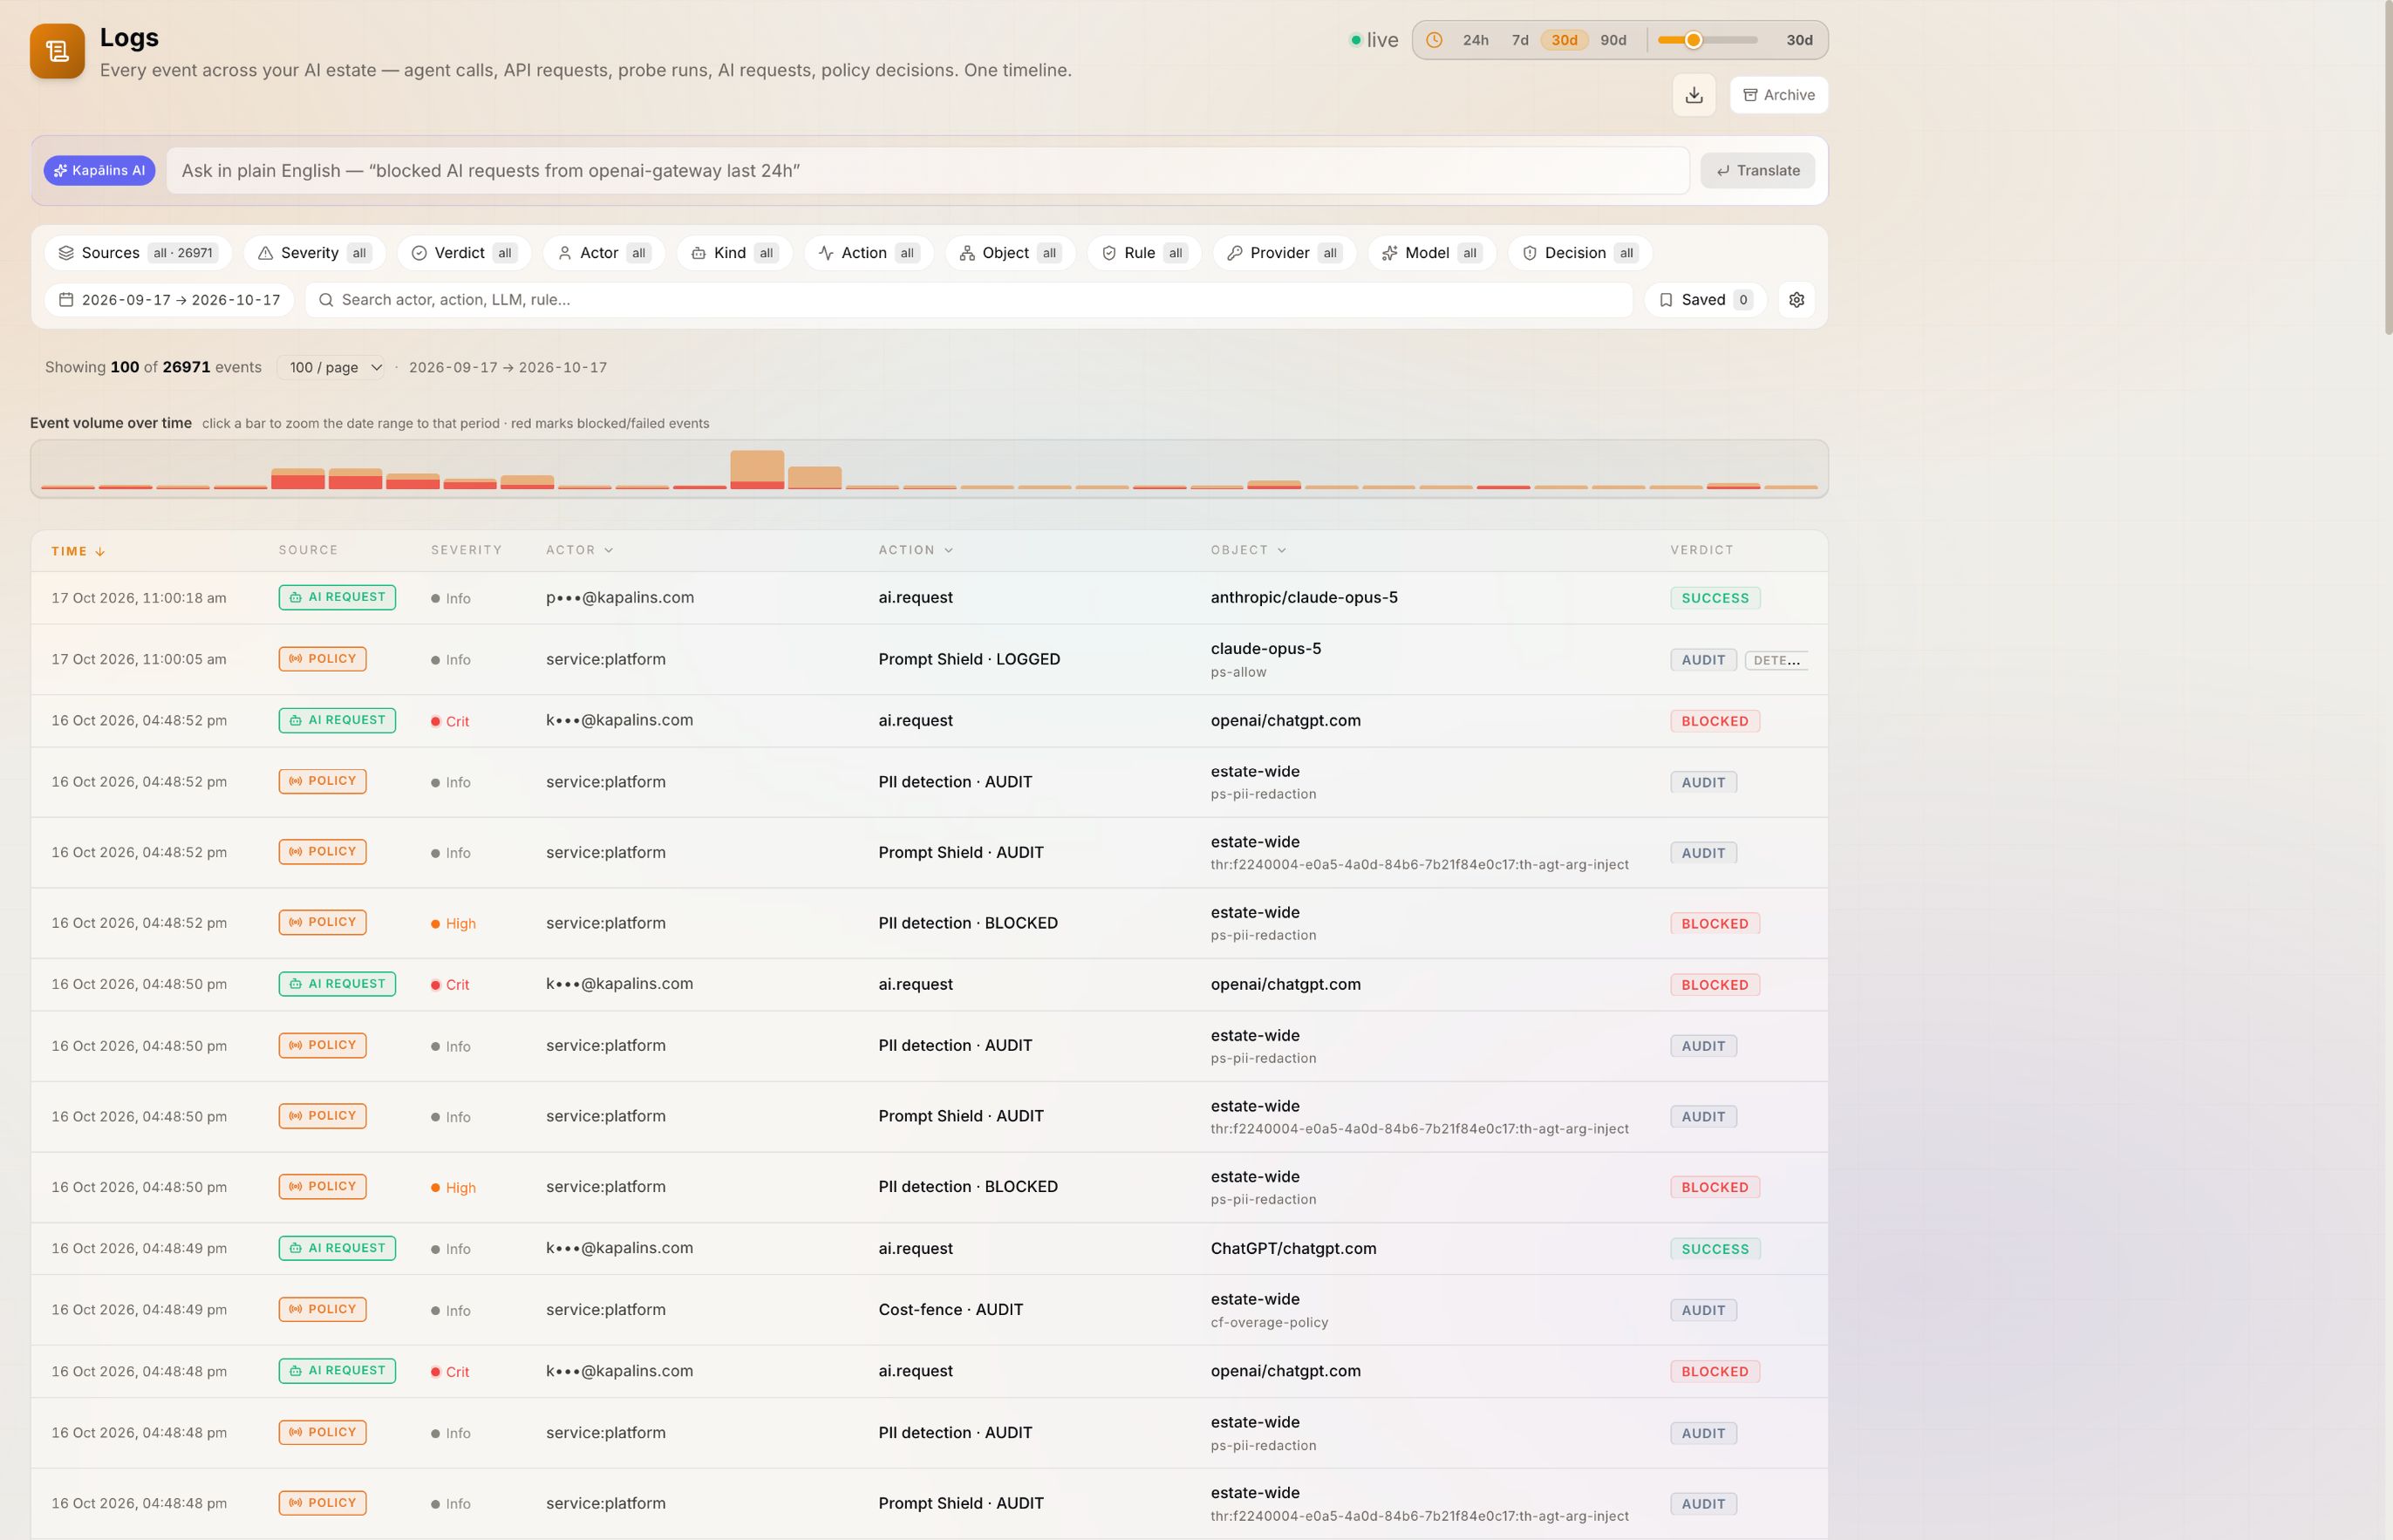
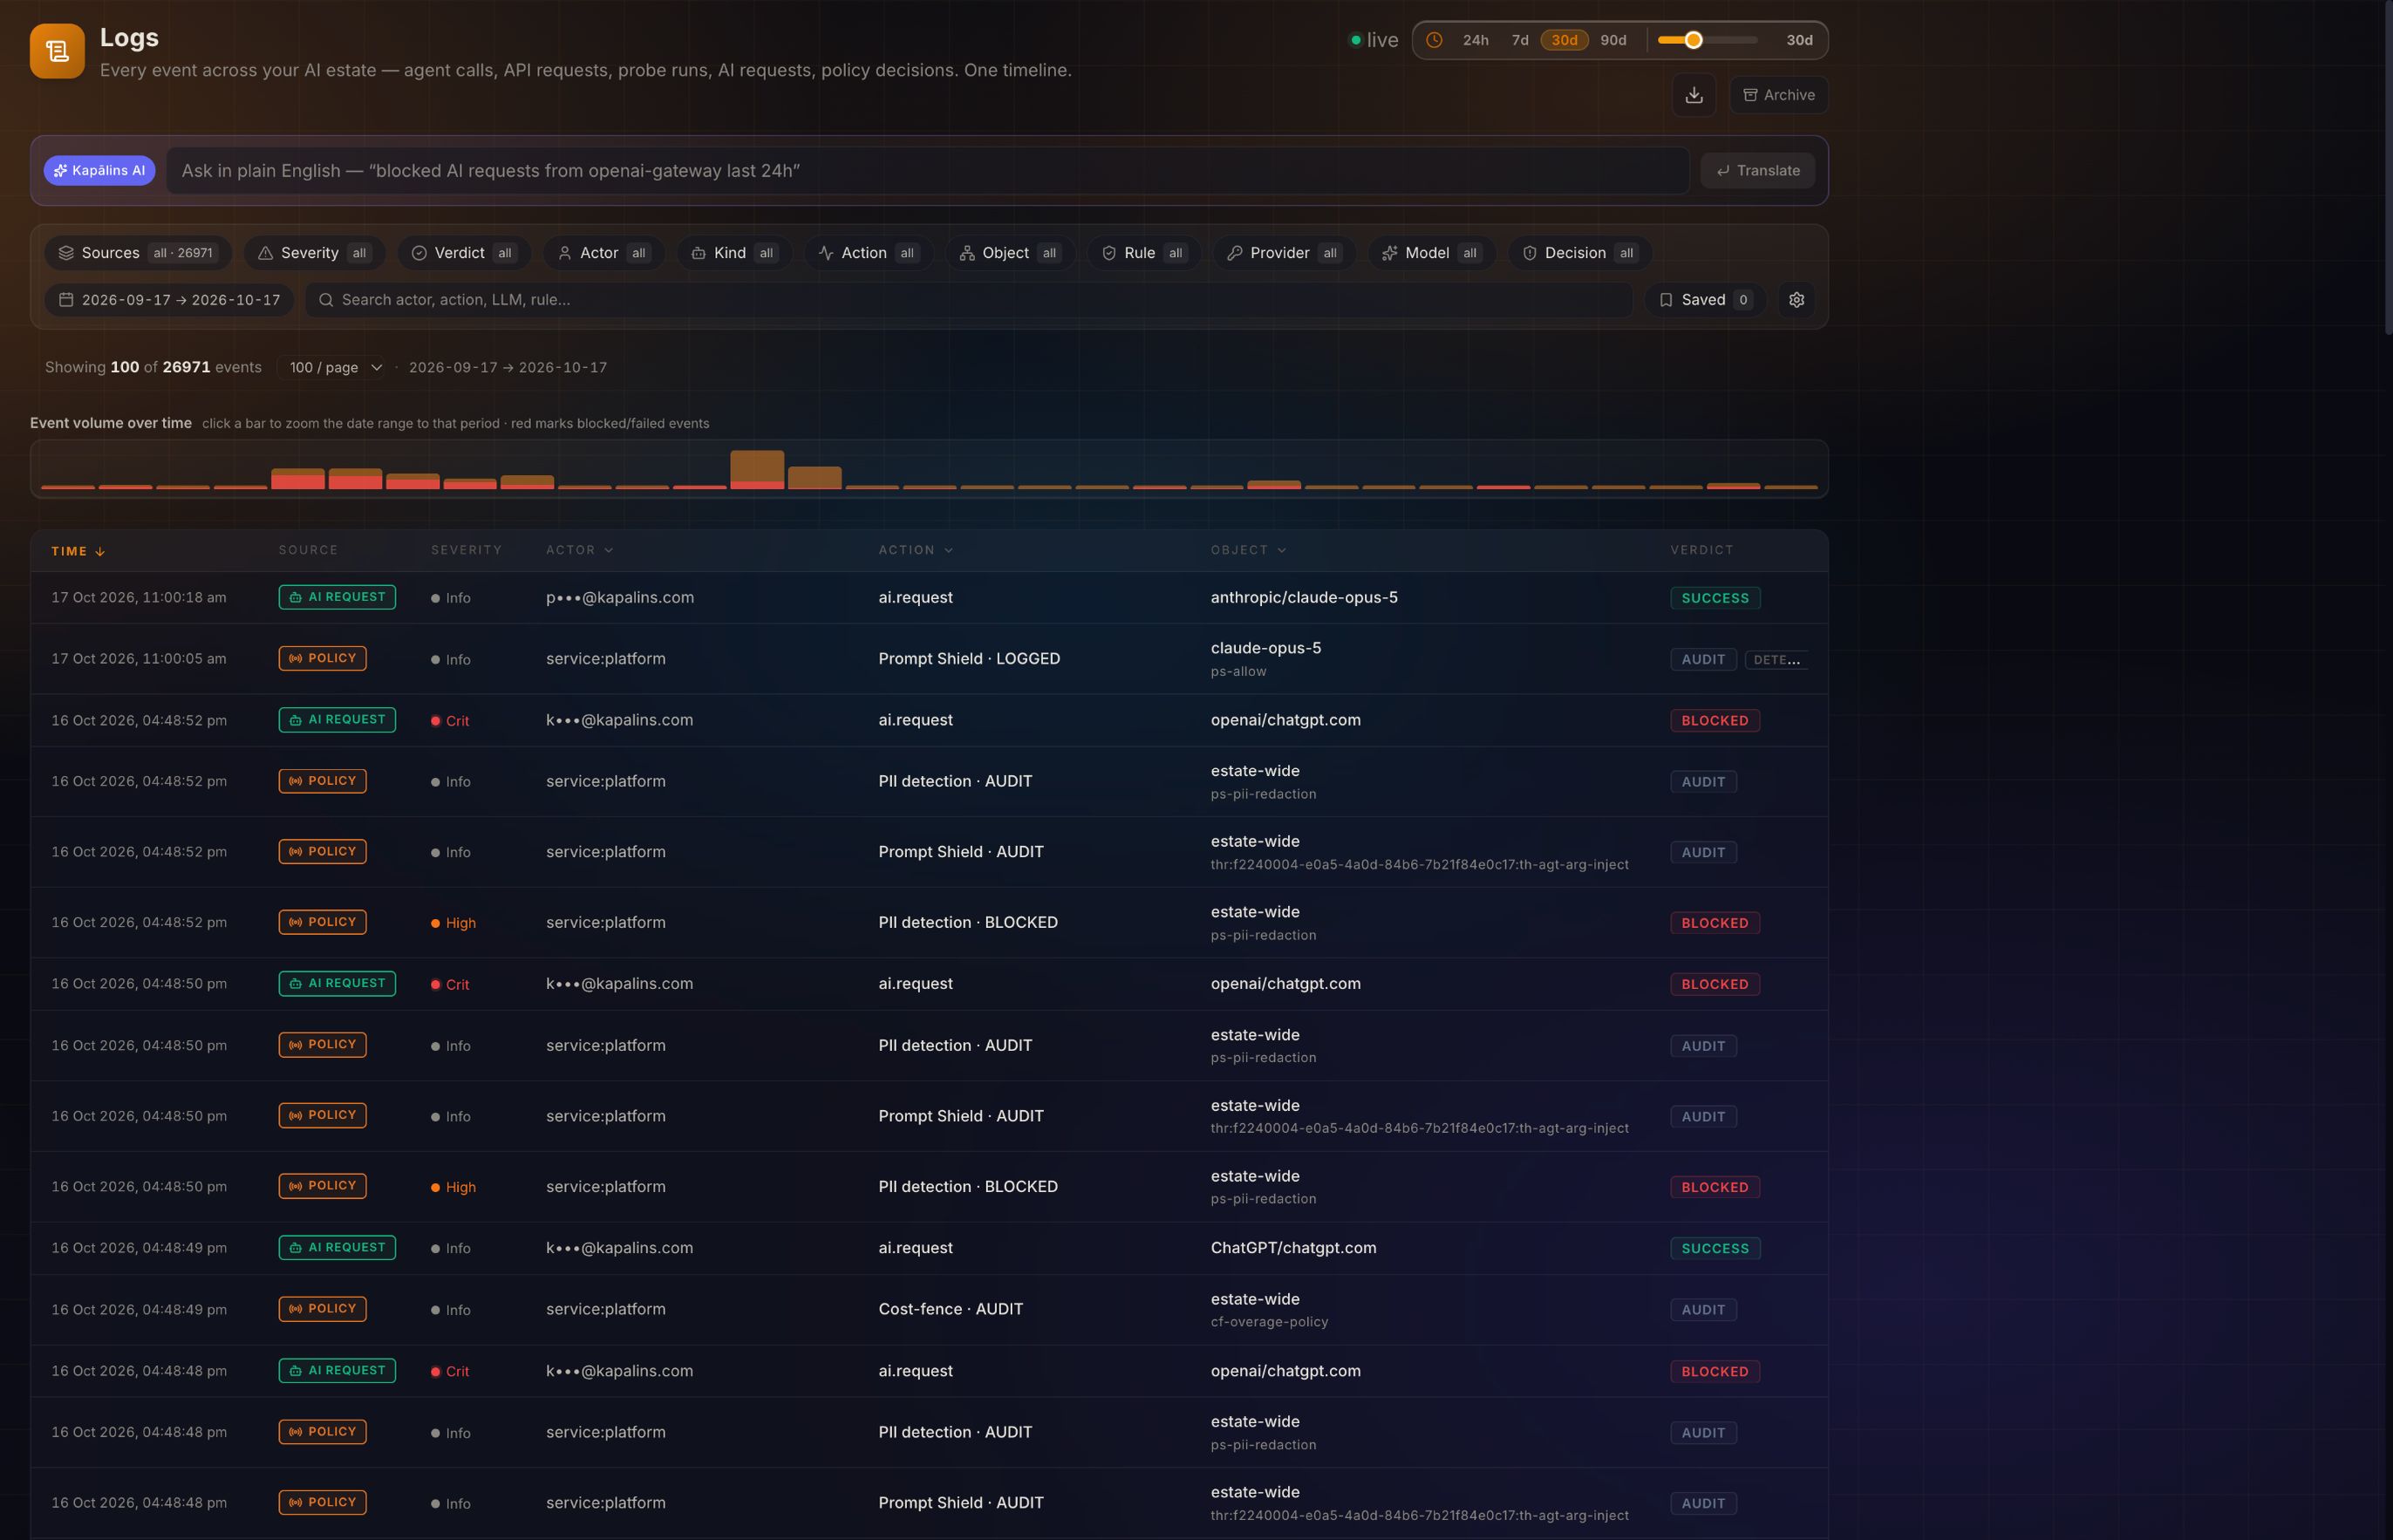
Claude in the same timeline as everything else.
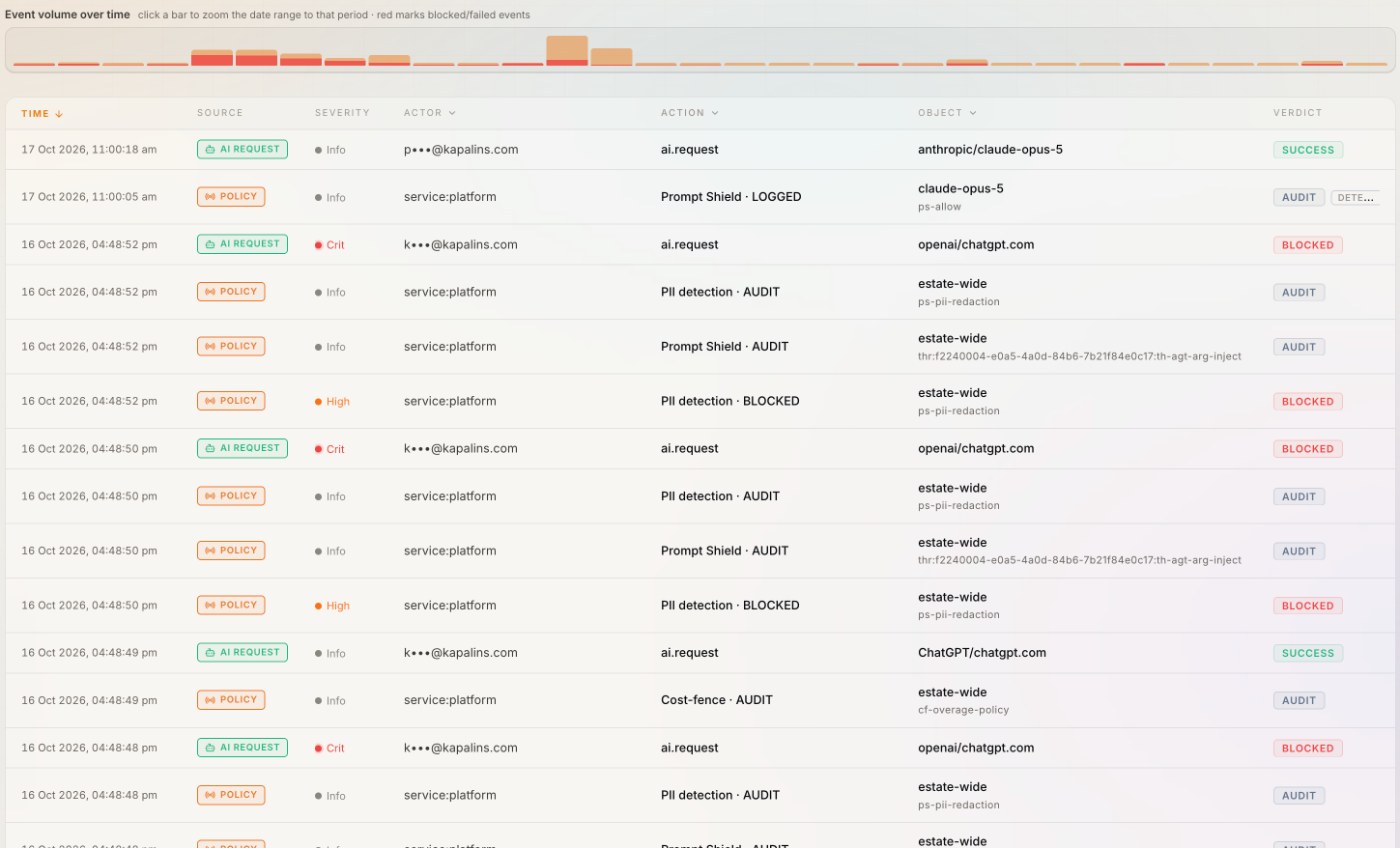
The connector reads Anthropic’s Activity Feed every 15 minutes and turns each activity into the event shape your gateway, devices and copilots already use. One search finds a person’s Claude sign-ins next to their blocked ChatGPT prompt.
- Window polling with overlap, so a late-indexed activity is never lost
- The raw Activity object kept exactly as Anthropic returned it
- Source label "Claude Enterprise" on every row
Personal Claude accounts and the API, too.
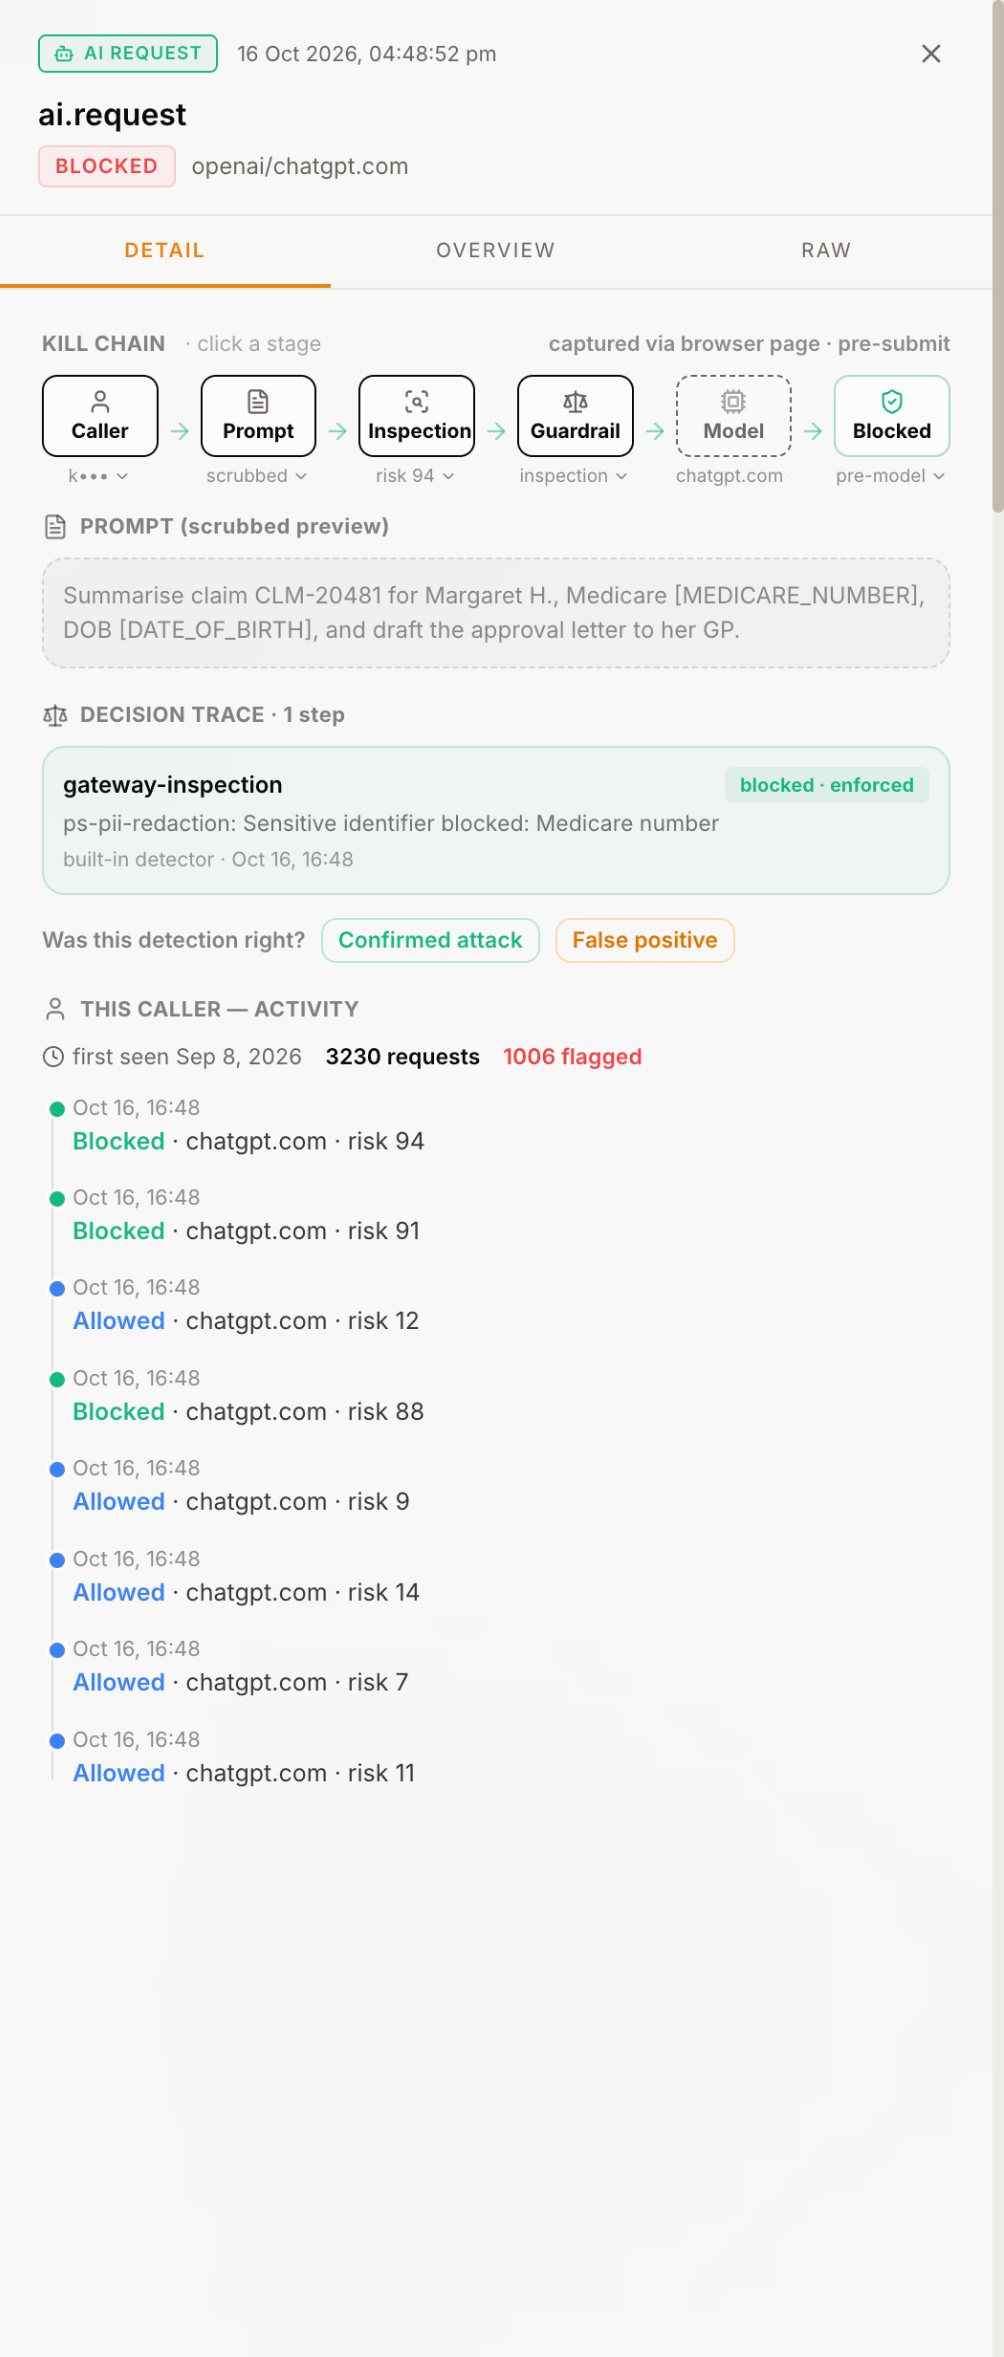
The Compliance API covers your organisation’s Claude tenant. A personal claude.ai account, or a direct call to the Claude API, never appears there. The Kapālins browser extension and gateway see those, and each one opens to its kill chain: who called, what was inspected, which rule decided.
- Prompts checked in the browser before they are submitted
- The same rules as the inline hooks
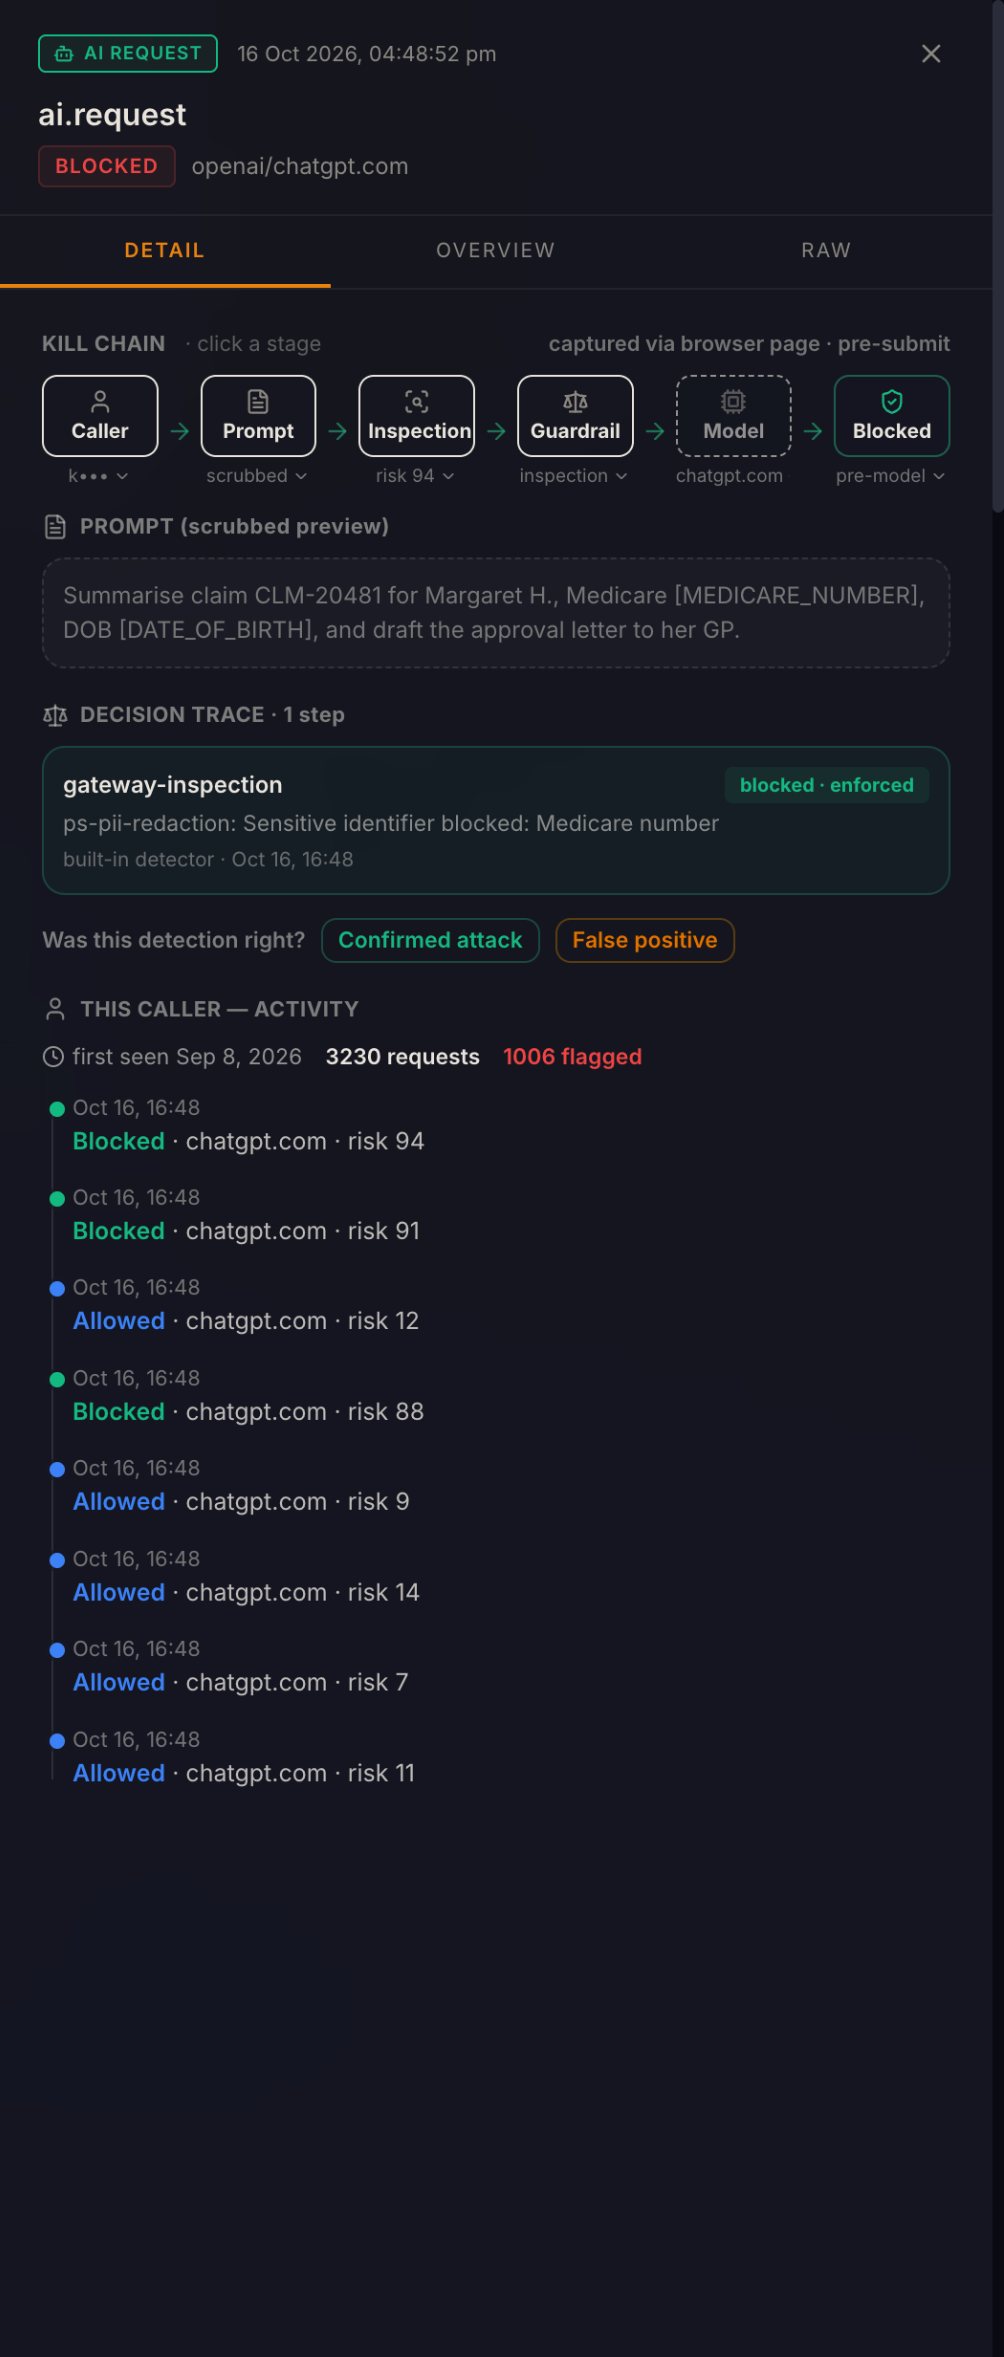
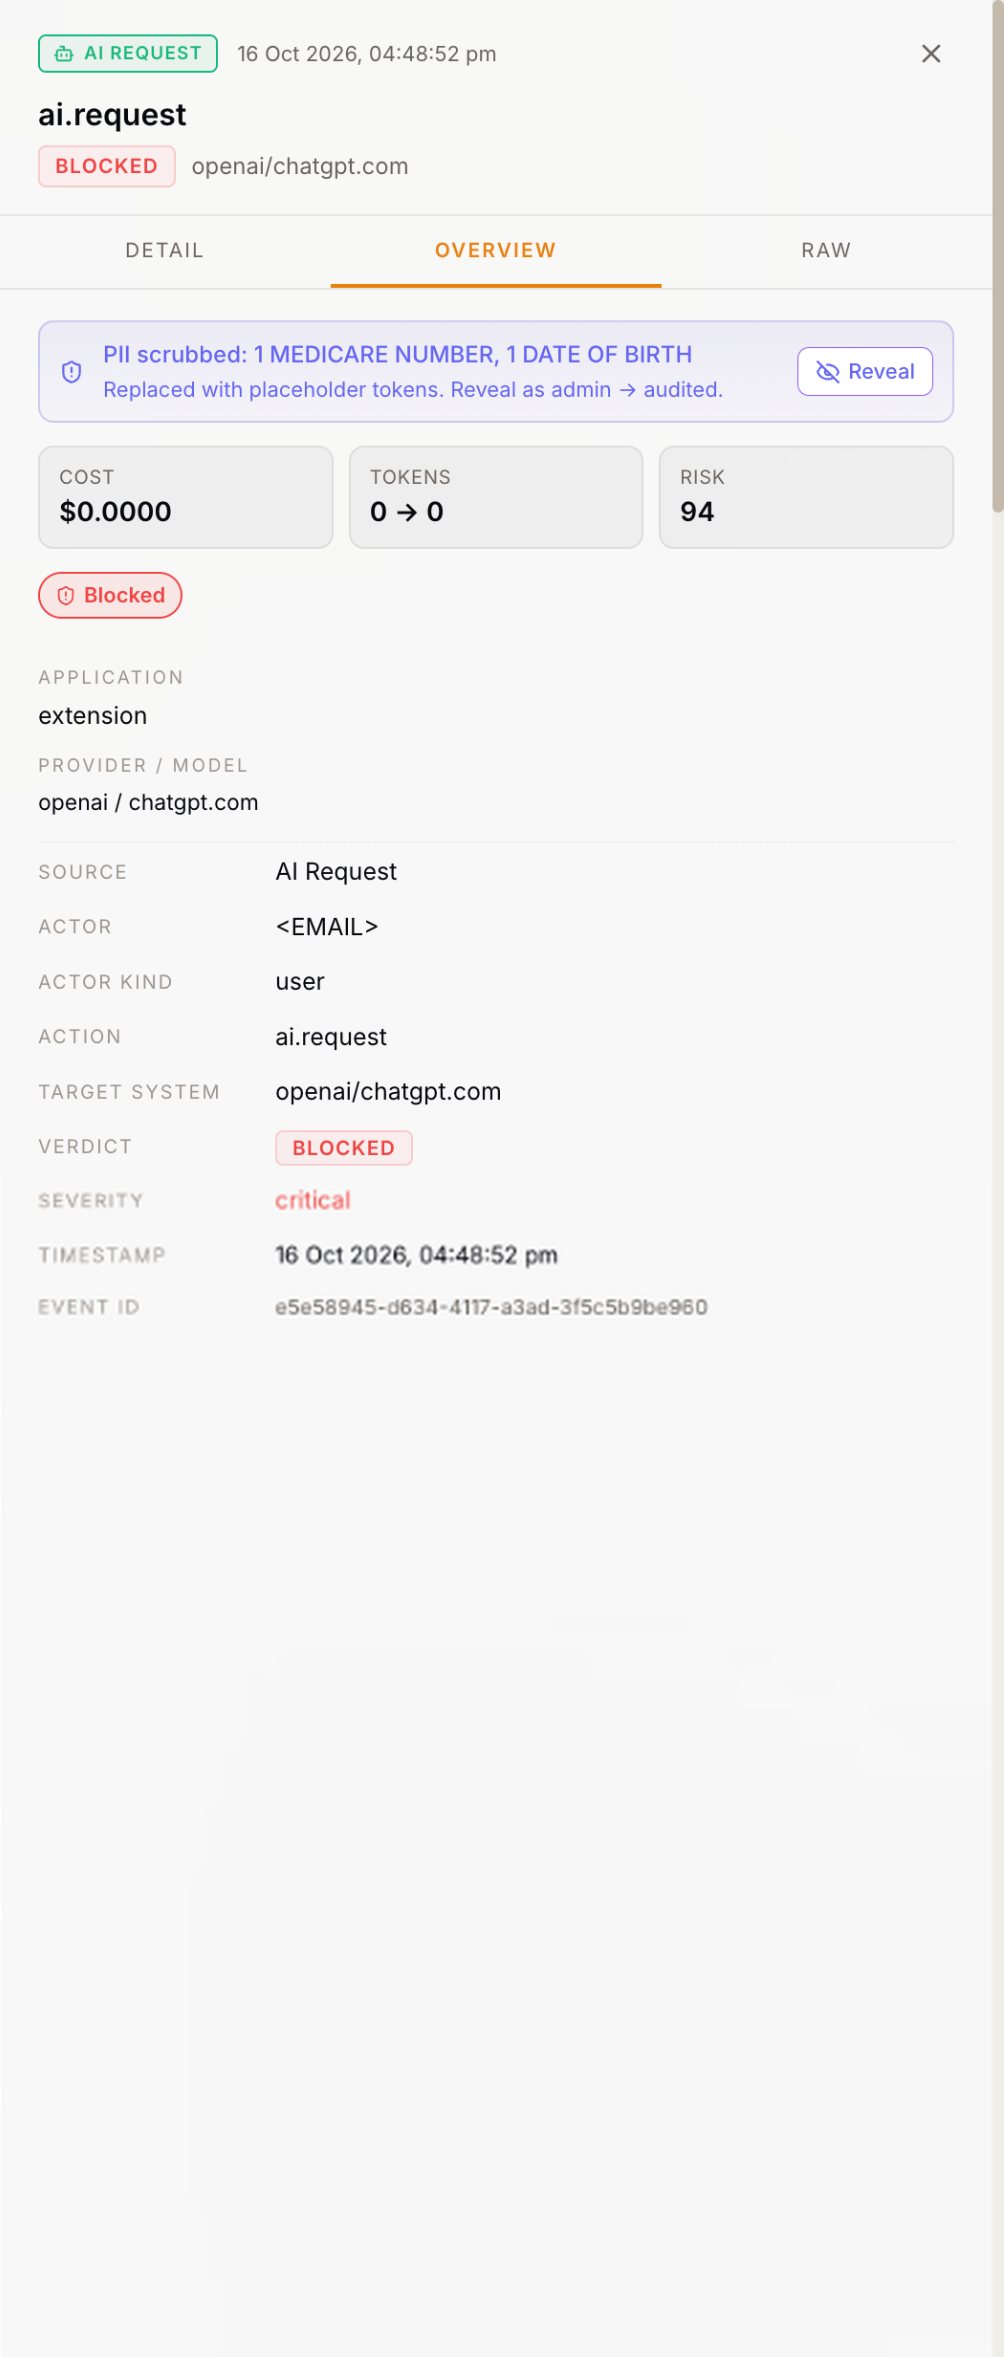
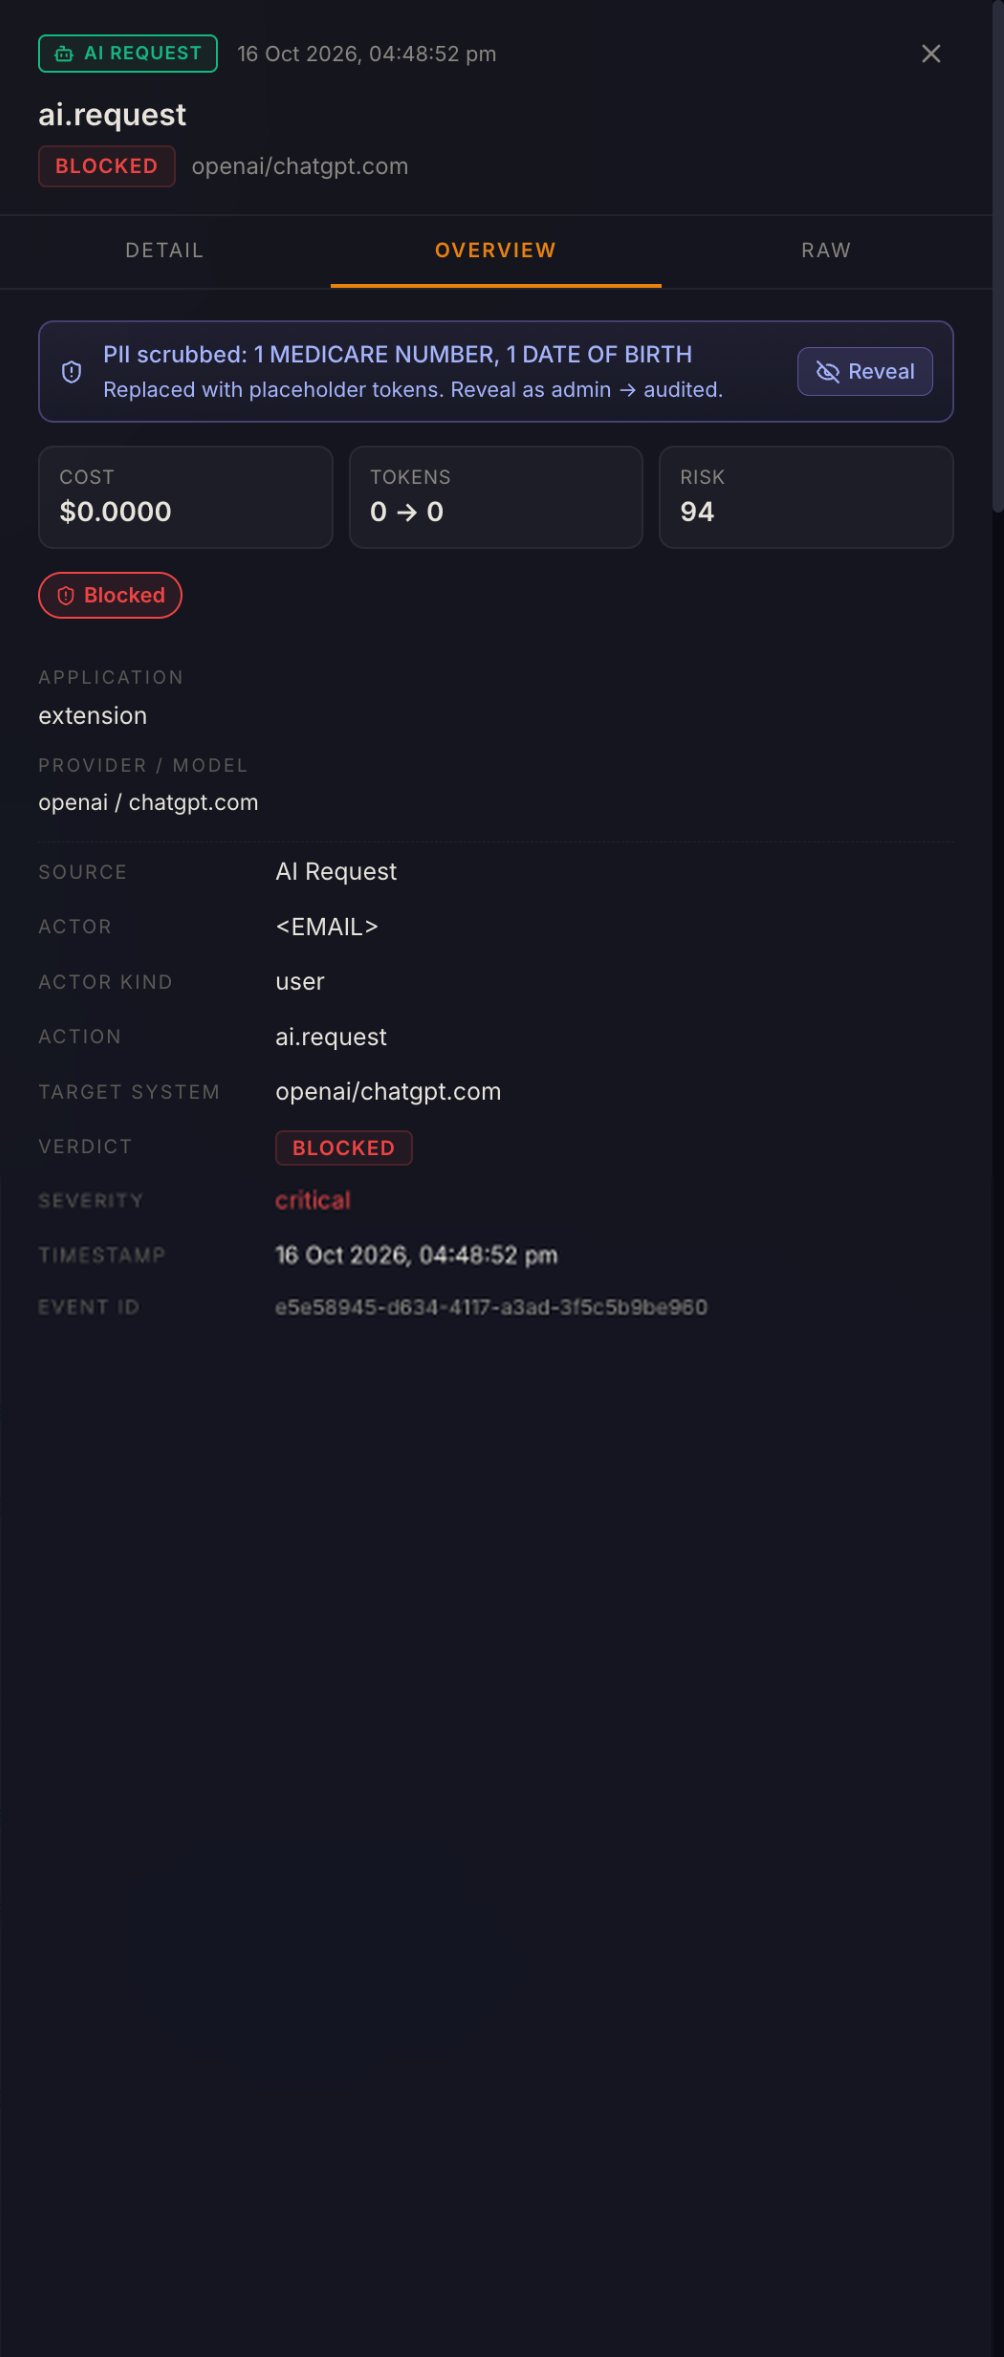
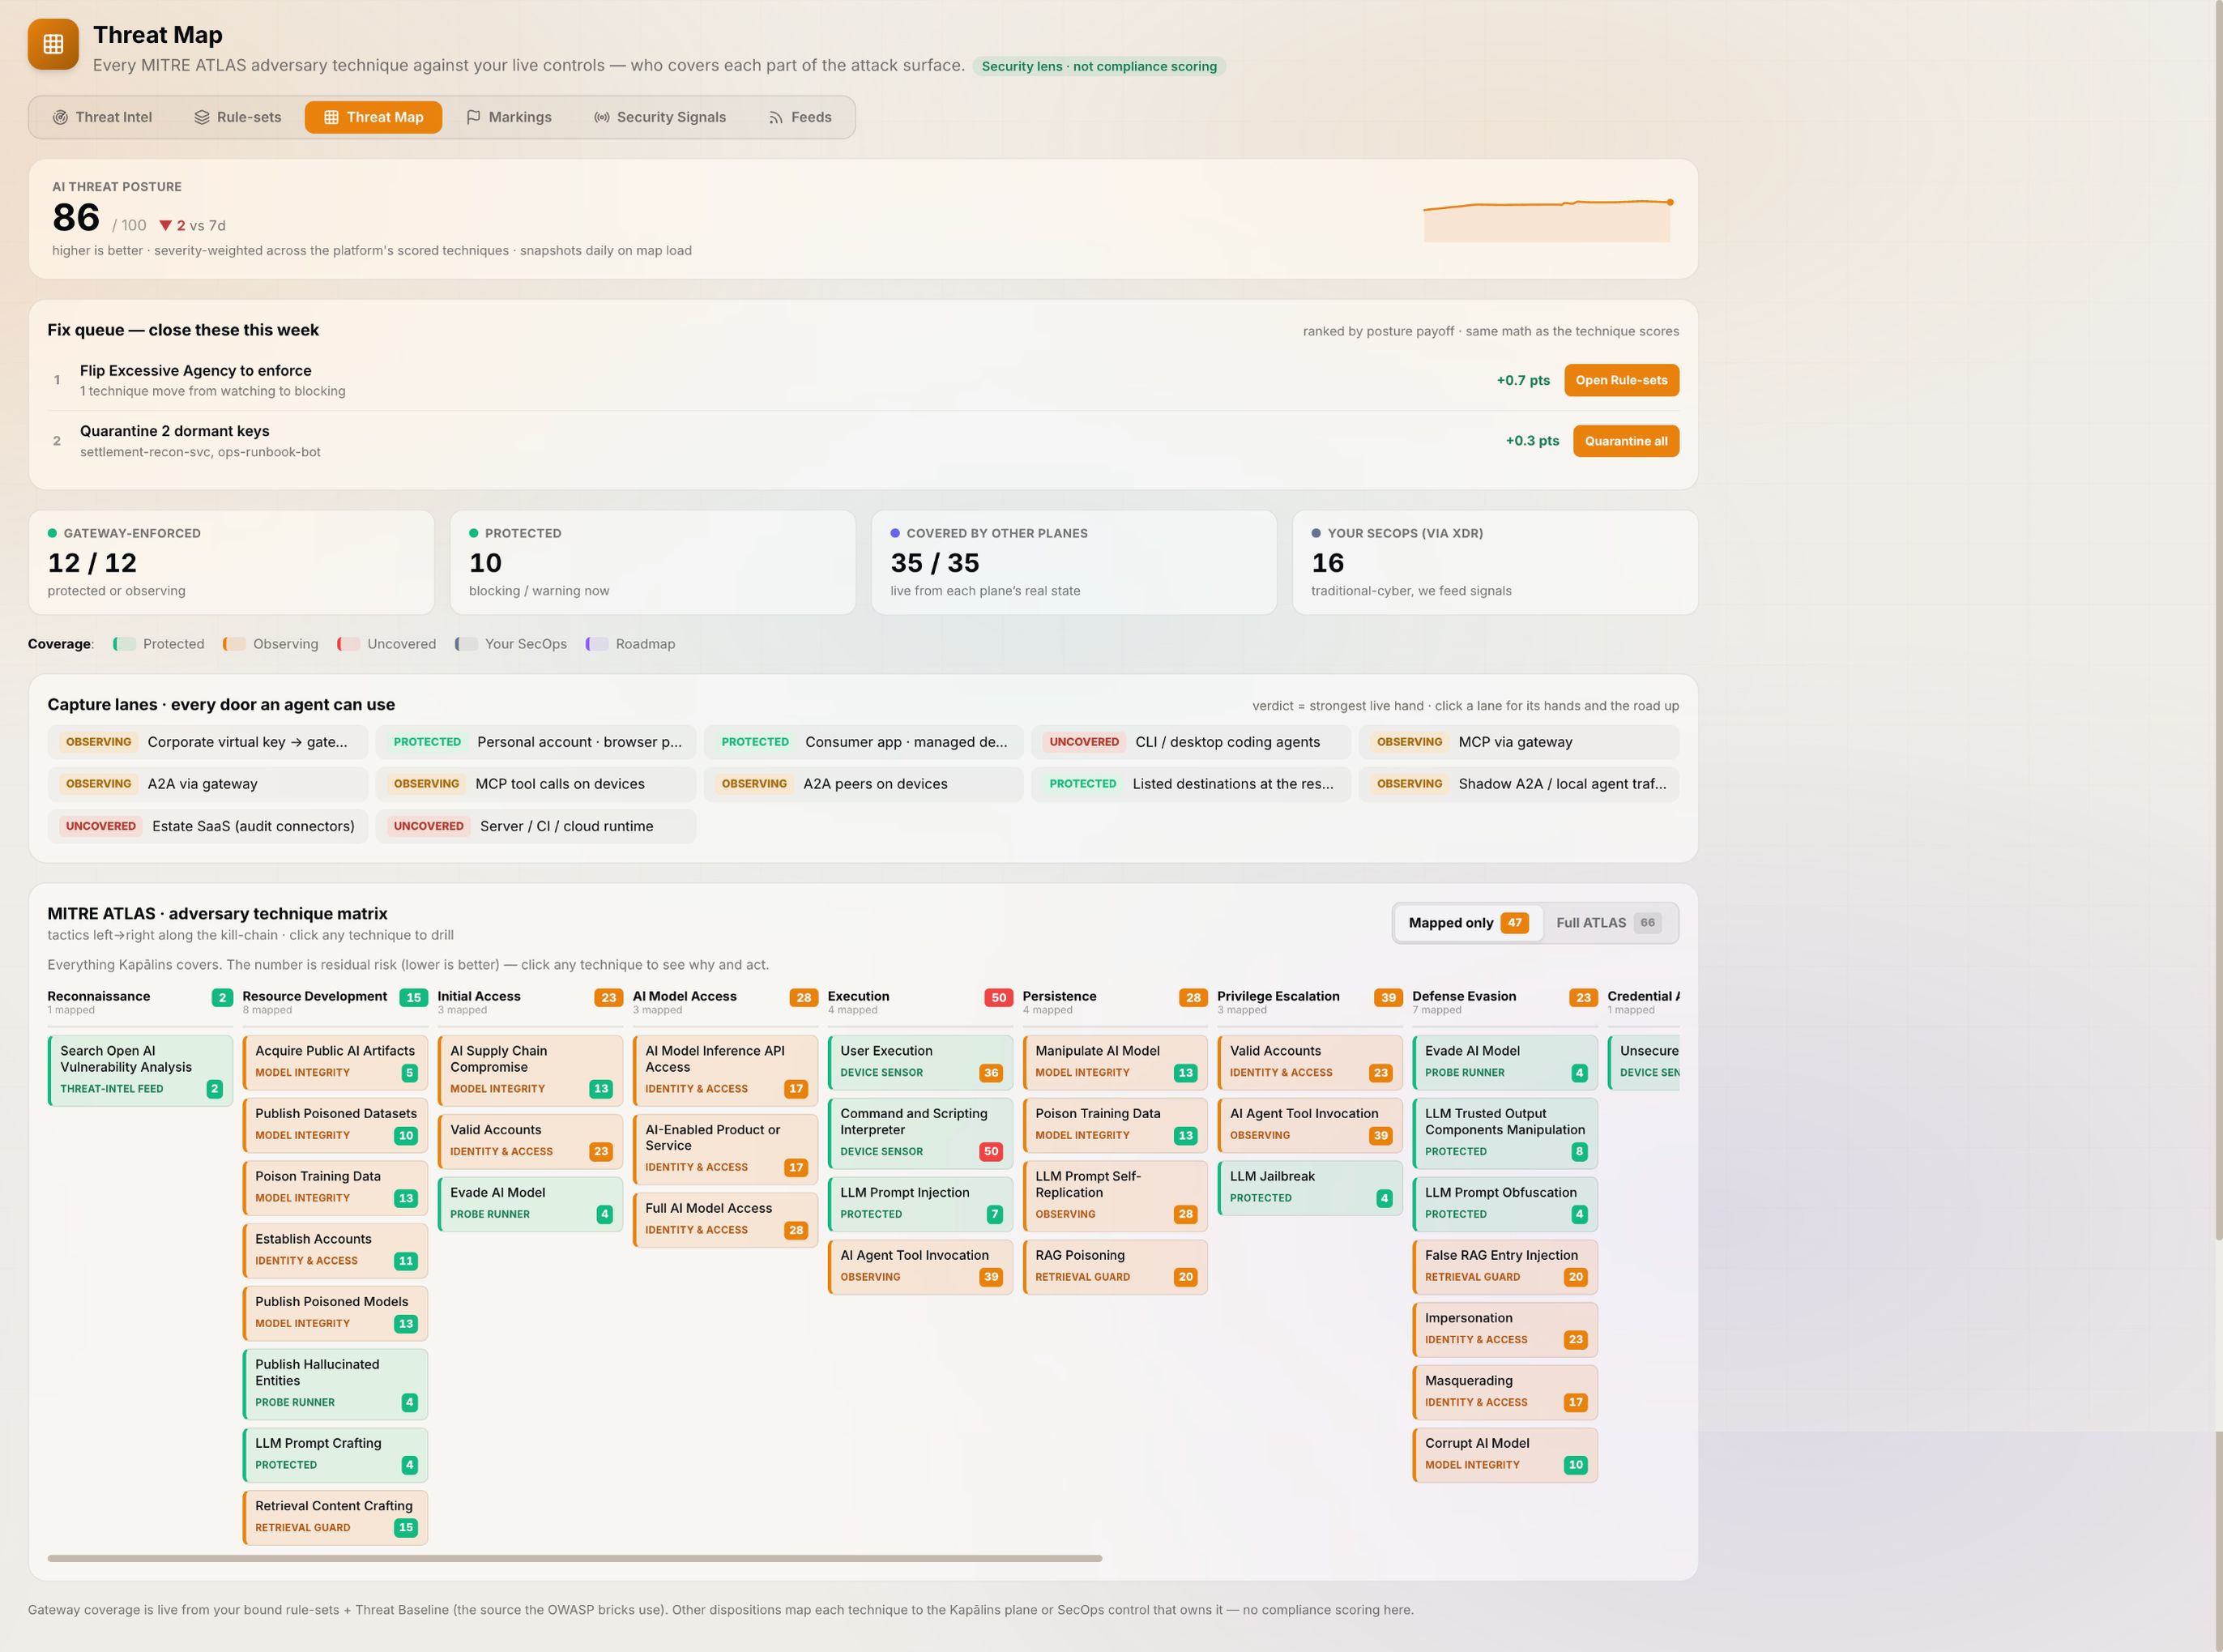
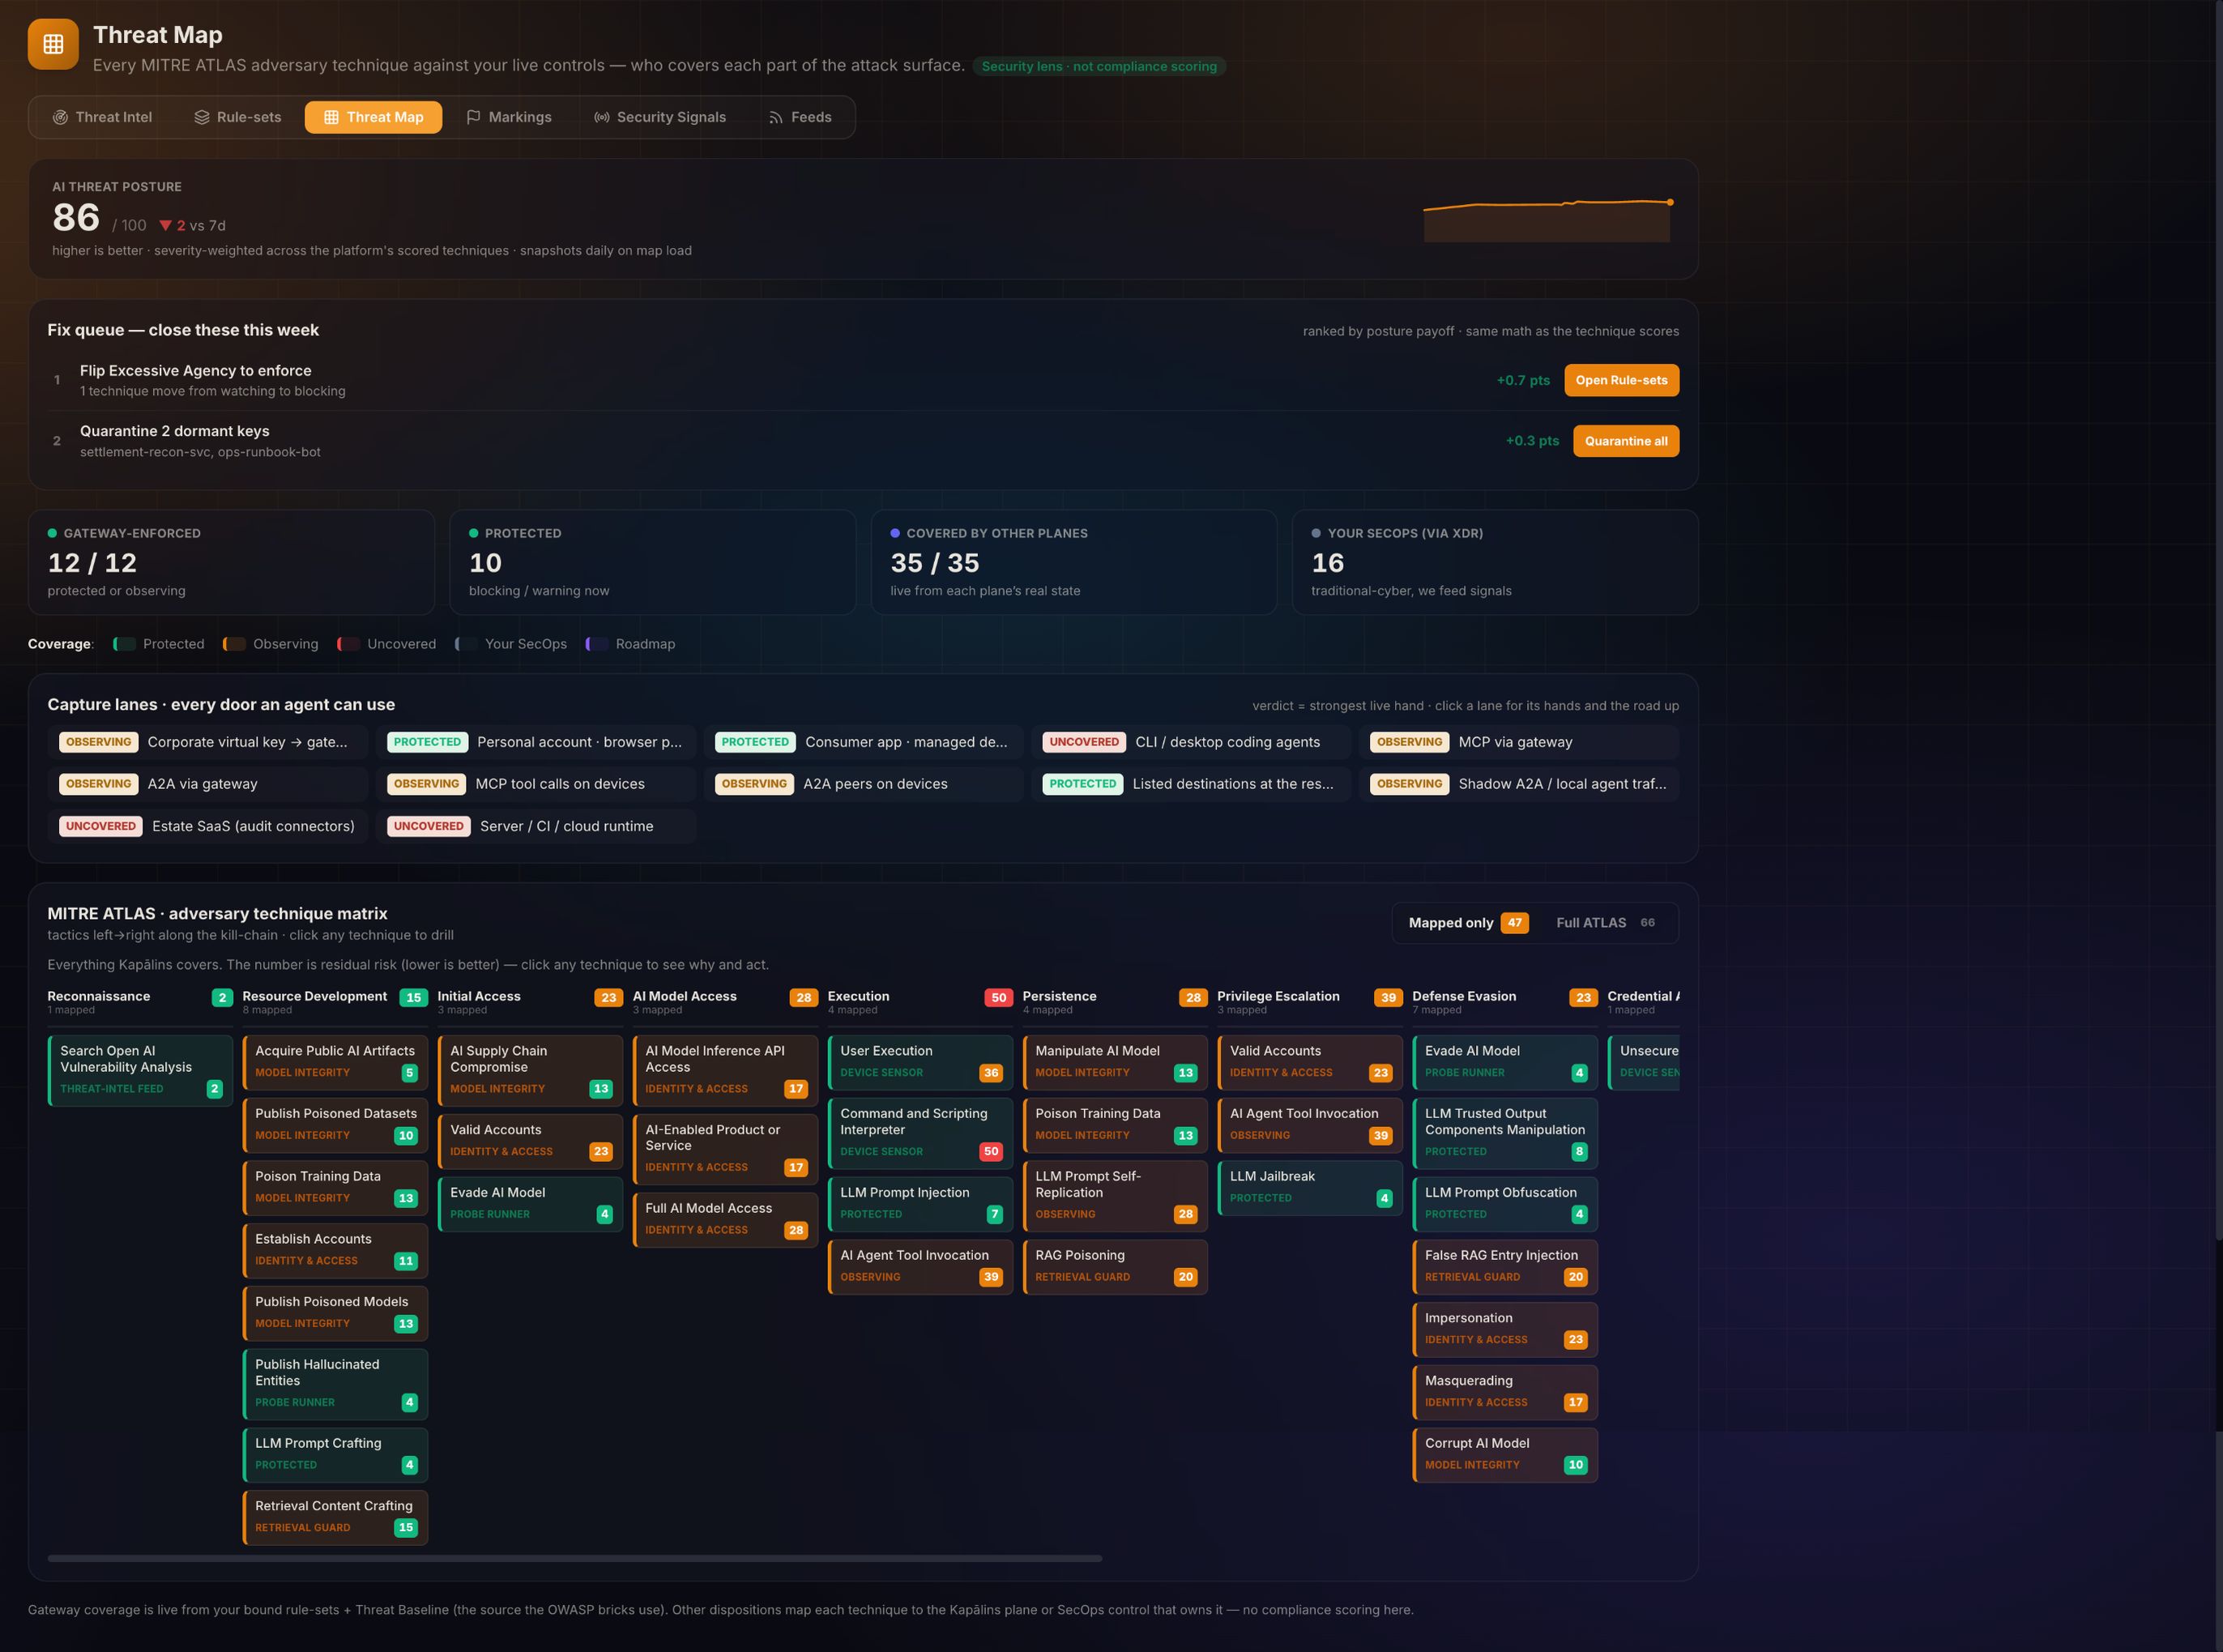
Mapped to the attack. Priced in dollars.
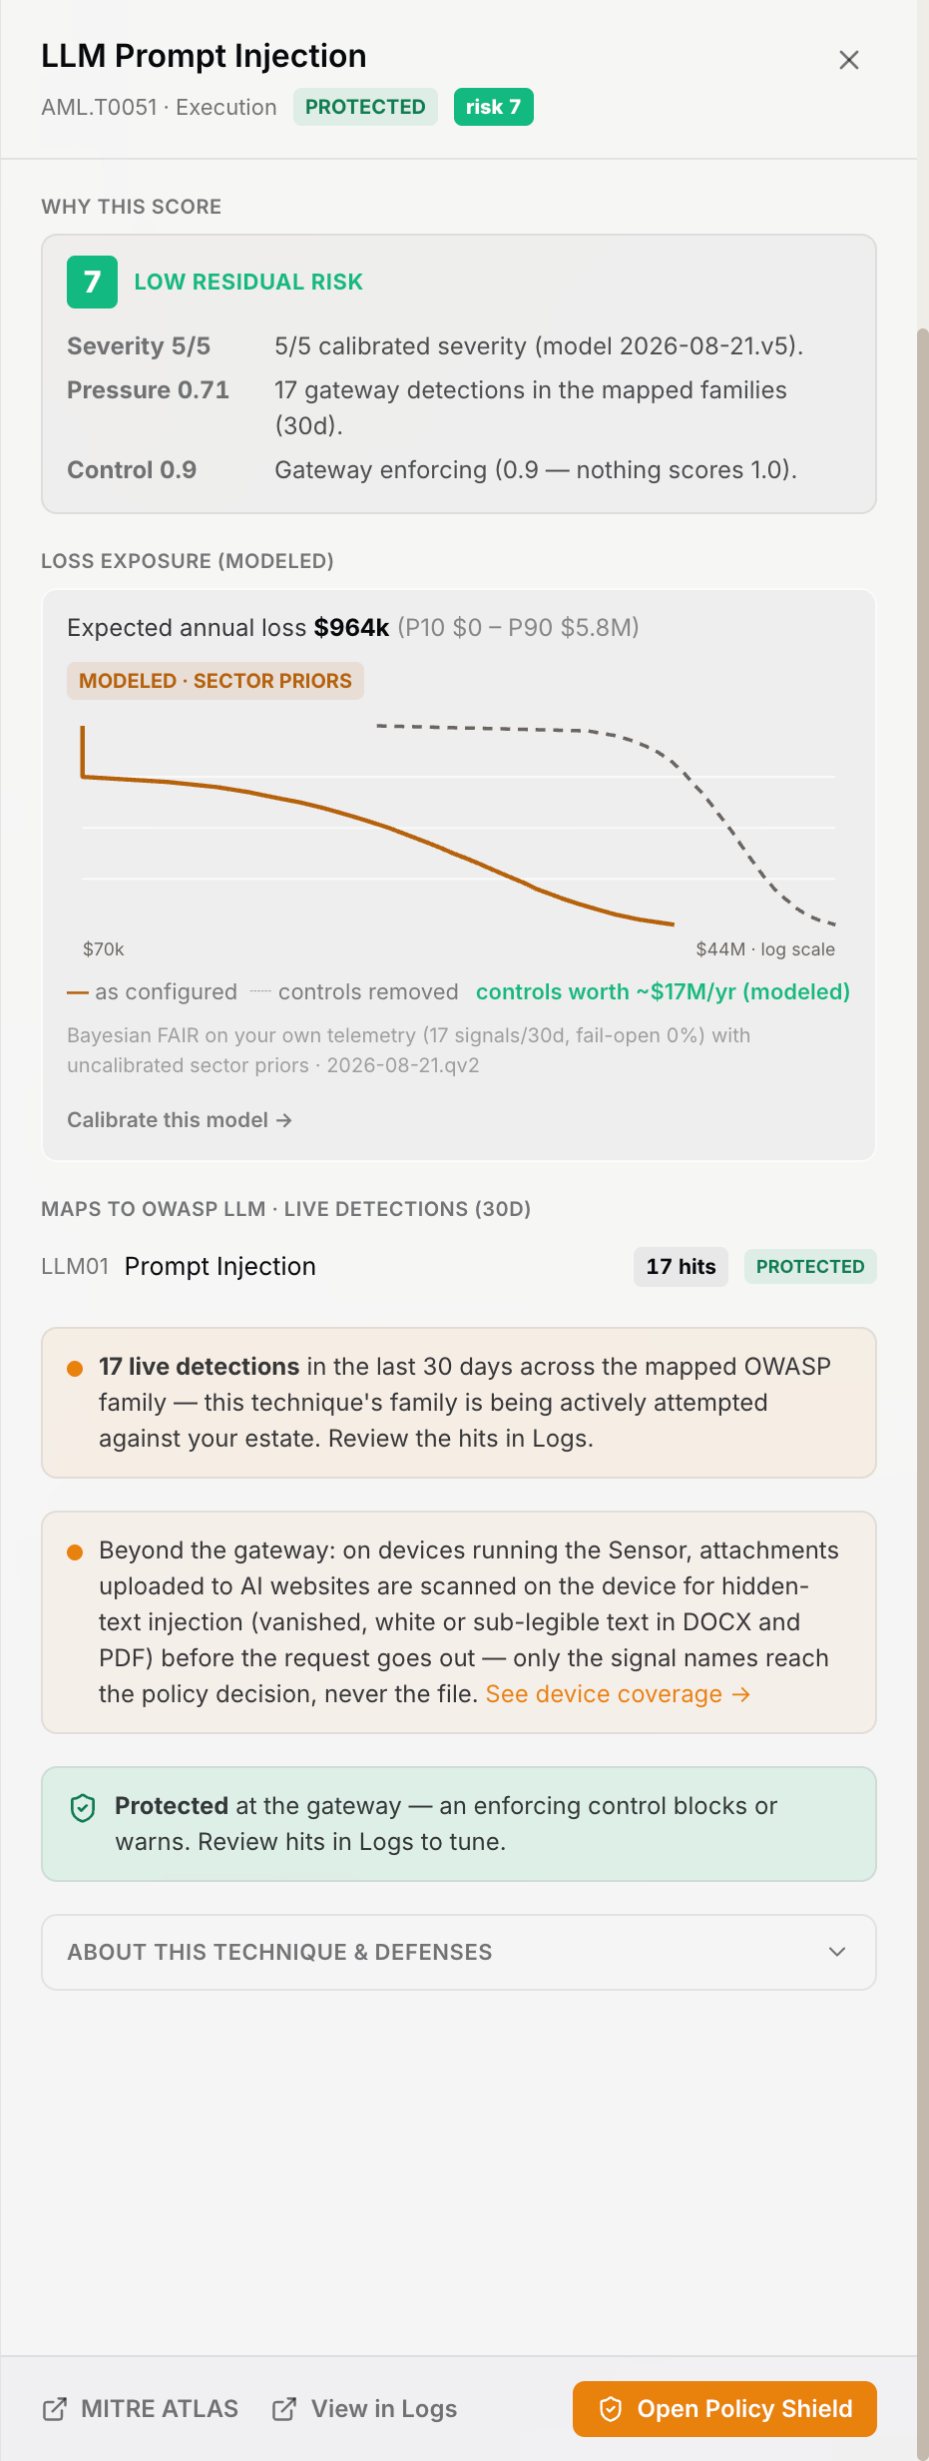
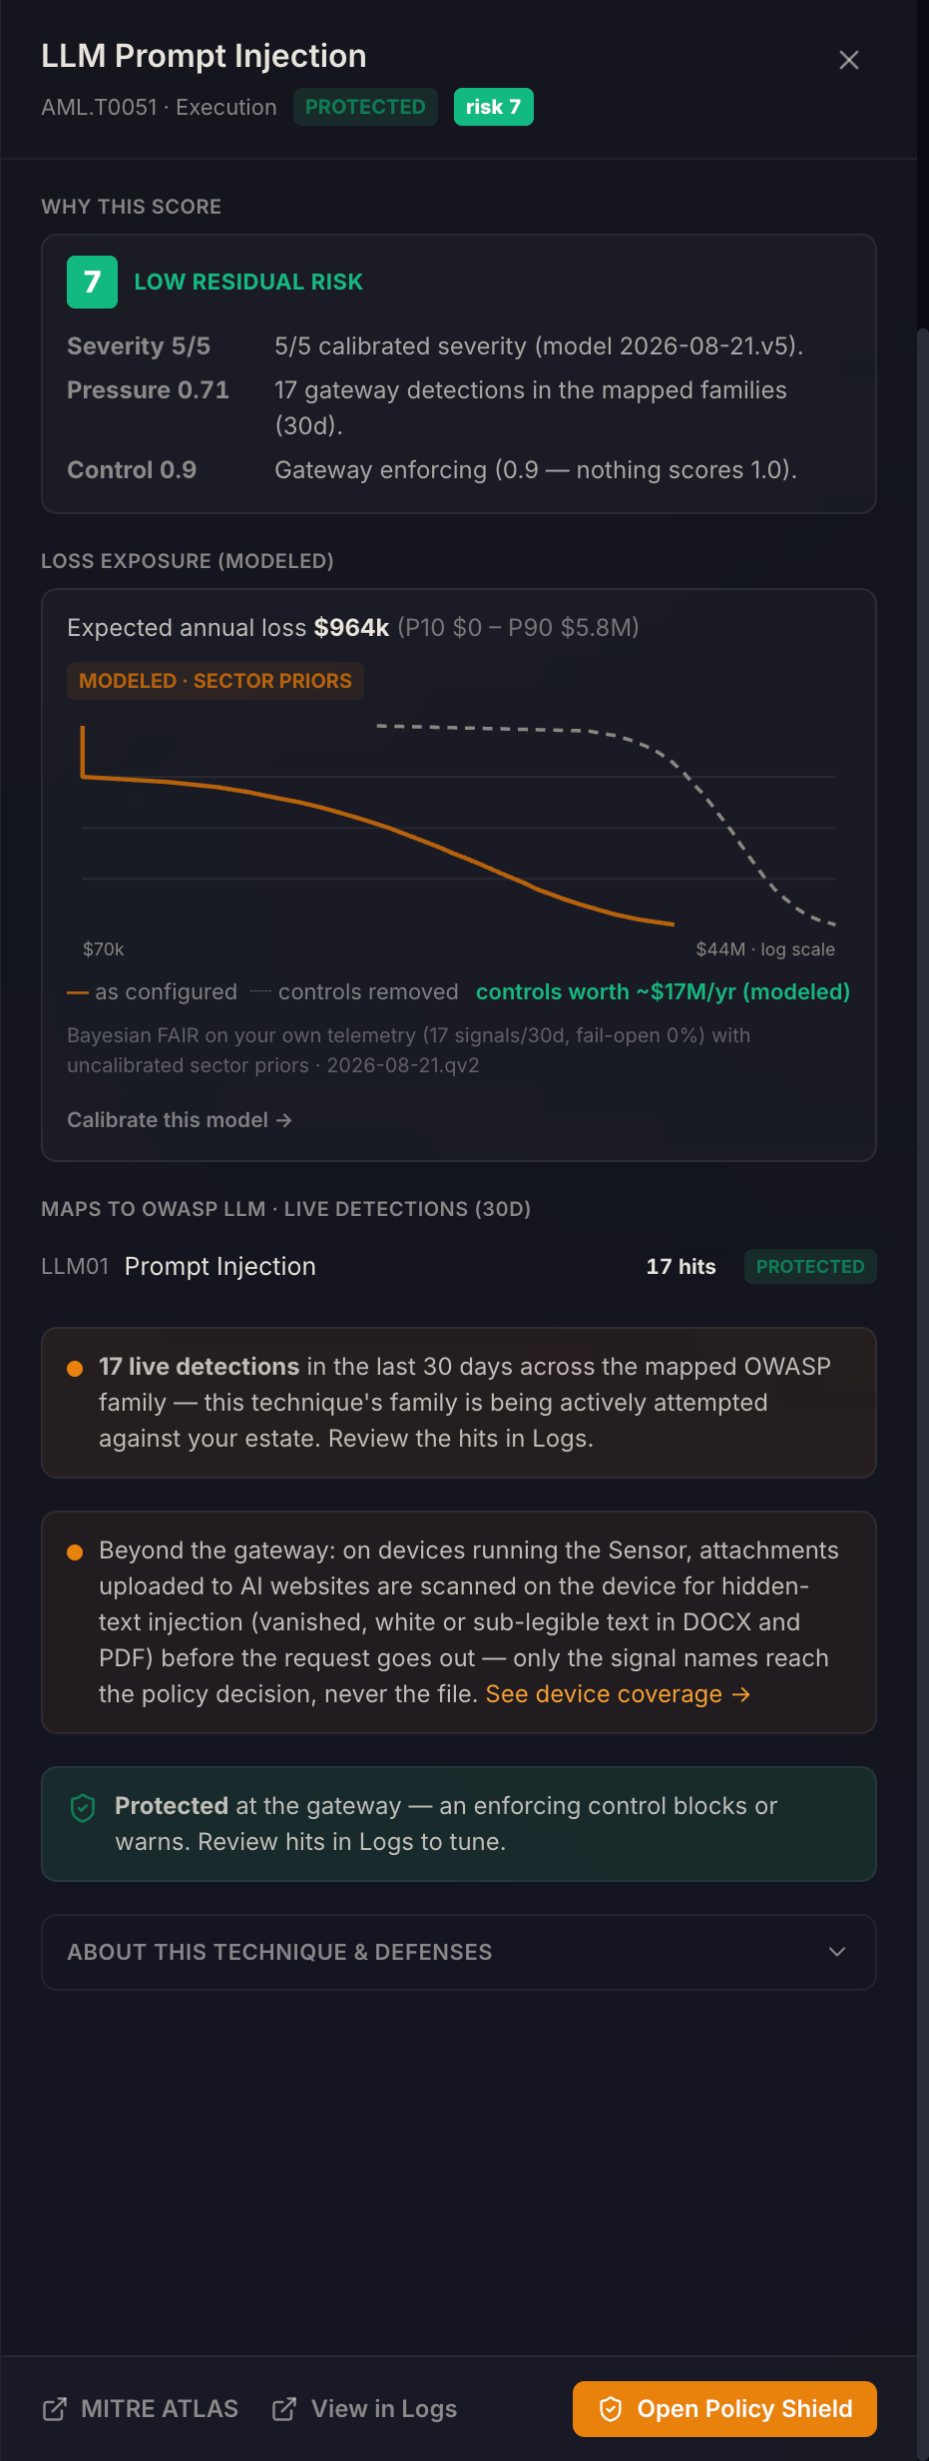
A denied prompt injection or an agent tool call lands on the MITRE ATLAS technique it belongs to, with the plane that covers it. Click the technique for its residual risk and a modelled annual loss, so Claude becomes one more covered door with a number on it.
- Every ATLAS technique against your live controls
- Loss modelled with Bayesian FAIR on your own telemetry, labelled as modelled
One score for the board, Claude included.
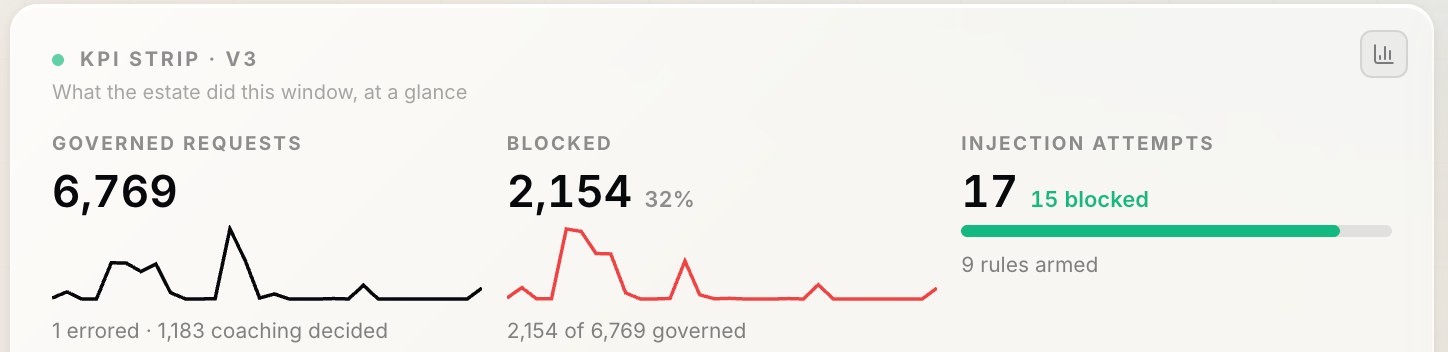
Claude activity and denials feed the AI Trust Index, the compliance obligations it proves and the evidence packs an auditor reads, so Claude is governed rather than exempted.
- Obligation, control, artifact, verification, in one chain
- Auto-verified where a live signal exists; attested where it cannot
Six steps, two of them in Anthropic’s console.
The audit plane needs one key. The inline plane adds a URL and a signing secret. Shadow mode first, so nobody is blocked on day one.
- Enable the Compliance APIYour Primary Owner turns it on under claude.ai › Organization settings › API. Activity is recorded from this point.
- Create a Compliance Access KeyWith the
read:compliance_activitiesscope. It starts withsk-ant-api01-and is shown once. - Connect it in KapālinsIntegrations › Claude Enterprise › paste the key. Kapālins reads one activity before storing anything.
- Allow Inference hooksUnder Data and privacy › Inference hooks, configure the endpoint URL Kapālins shows. Copy the signing secret.
- Test, then shadowPaste the secret into Kapālins, Test connection, then Shadow mode with Enforce verdicts on.
- EnforceChoose block or allow on failure, set a rollout percentage, keep Validate tool calls on.
The details a security team asks for.
Endpoints, polling, rate limits, key storage, verdict signing
Today: GET /v1/compliance/activities, and the Inference hooks prompt and tool_call events. Being added behind a per-organisation switch: the chats, files and session endpoints.
Every 15 minutes; 1,000 activities a page, up to 50 pages a sweep; the upper bound held a minute in the past; each window overlaps the last by five minutes; duplicates absorbed on the activity id.
Anthropic allows 600 requests a minute per parent organisation. A sweep makes at most 50. On a 429 the sweep stops and the next resumes; the connector is never marked failed for being throttled.
AES-256-GCM at rest, decrypted only inside the ingestion job and the connect-time validation, never returned to the browser or written to a log. A 401 or 403 marks the credential expired and notifies administrators.
Standard Webhooks signature with a five-minute clock skew, deduplicated on the webhook id, answered within 2.5 seconds by default. A deny carries a reason and a reference id of 50 characters or fewer.
The platform runs in Google Cloud australia-southeast1. Every event names its source as Claude Enterprise; the raw Activity object is kept as Anthropic returned it.
What this integration does not do
Boundaries set by Anthropic’s interfaces
The Activity Feed records resource events, not prompt or response text. Inference hooks return allow or deny; they cannot rewrite or redact a prompt, and image-only content is not inspected. Neither interface reaches Claude on Bedrock, Vertex AI or Foundry, and Claude Platform (API) organisations expose activity events only. Inference hooks are in beta.
Boundaries set by what Kapālins ships today
Conversation, file and session content retrieval through the content endpoints is built and under review; treat content coverage as a roadmap item. Redaction of sensitive data happens in the Governed Workspace and the gateway, where Kapālins holds the request, not inline on Claude.
Know the model before you trust it.
Kapālins Labs publishes how frontier models behave when they think no one is watching, the AI supply chain we catalogue, and a monthly review of what the safety institutes found.
See Claude Enterprise governed in thirty minutes.
Bring your Primary Owner. We connect a sandbox organisation live, watch the first activities land, and deny one prompt inline.
Questions buyers ask.
Does Kapālins read conversation content from Claude Enterprise?
Today the connector reads activity events from the Compliance API Activity Feed, which records who did what and when but not prompt or response text. Retrieval of chats, uploaded files and Cowork and Claude Code session transcripts through the content endpoints is being added behind a per-organisation switch and a key that carries read:compliance_user_data. Inline, the Inference hooks endpoint sees the transcript of each governed request at the moment it is sent, and keeps only the verdict.
Which key does the integration need?
A Compliance Access Key (sk-ant-api01-…) with the read:compliance_activities scope, created by your organisation’s Primary Owner under claude.ai › Organization settings › API. A standalone Claude Console organisation can use an Admin API key (sk-ant-admin01-…) instead, which reaches the Activity Feed only. A model API key (sk-ant-api03-…) does not work with the Compliance API.
Does it cover Claude on Amazon Bedrock, Google Cloud Vertex AI or Microsoft Foundry?
No. The Compliance API and Inference hooks are Anthropic interfaces for Claude Enterprise organisations, and sessions run through those cloud platforms are not captured by them. Claude Platform (API) organisations expose administrative and resource events through the Activity Feed but no prompt or response content. Models called through those platforms are governed by the Kapālins gateway instead.
What happens if Kapālins cannot answer an Inference hooks request in time?
Your organisation’s own failure handling in claude.ai decides: block the request or allow it without inspection. Within its budget Kapālins answers in under 2.5 seconds by default, and when a decision cannot complete in time it applies the inspection fail mode you set in Kapālins, so a fail-open is recorded as monitor-only rather than passed off as a verdict.
Where is the data held?
In Google Cloud australia-southeast1. The Compliance Access Key is encrypted at rest with AES-256-GCM and decrypted only inside the ingestion job and the connect-time validation. It is never returned to the browser or written to a log.
Is this a partnership with Anthropic?
It is an integration built on Anthropic’s published Compliance API and Inference hooks interfaces. Kapālins is a separate product; Anthropic does not operate or endorse it.