Kapālins for Snowflake Cortex REST API
xAI’s Grok models through the Snowflake Cortex REST API. Your applications call Kapālins instead of Snowflake Cortex REST API: the prompt is checked on the way out, the reply on the way back, and Snowflake Cortex REST API’s key never leaves the vault.

Stop it before it leaves
A prompt carrying a customer record, a secret or an injection attempt is redacted or blocked before Snowflake Cortex REST API sees it. The reply is checked on the way back.
One key no app ever holds
Each application gets its own virtual key. Snowflake Cortex REST API’s key is sealed in Kapālins, rotates without a redeploy, and can be cut off per app in one click.
Every model, judged
Snowflake Cortex REST API’s models are approved or blocked one by one, by a person, with who decided and when.
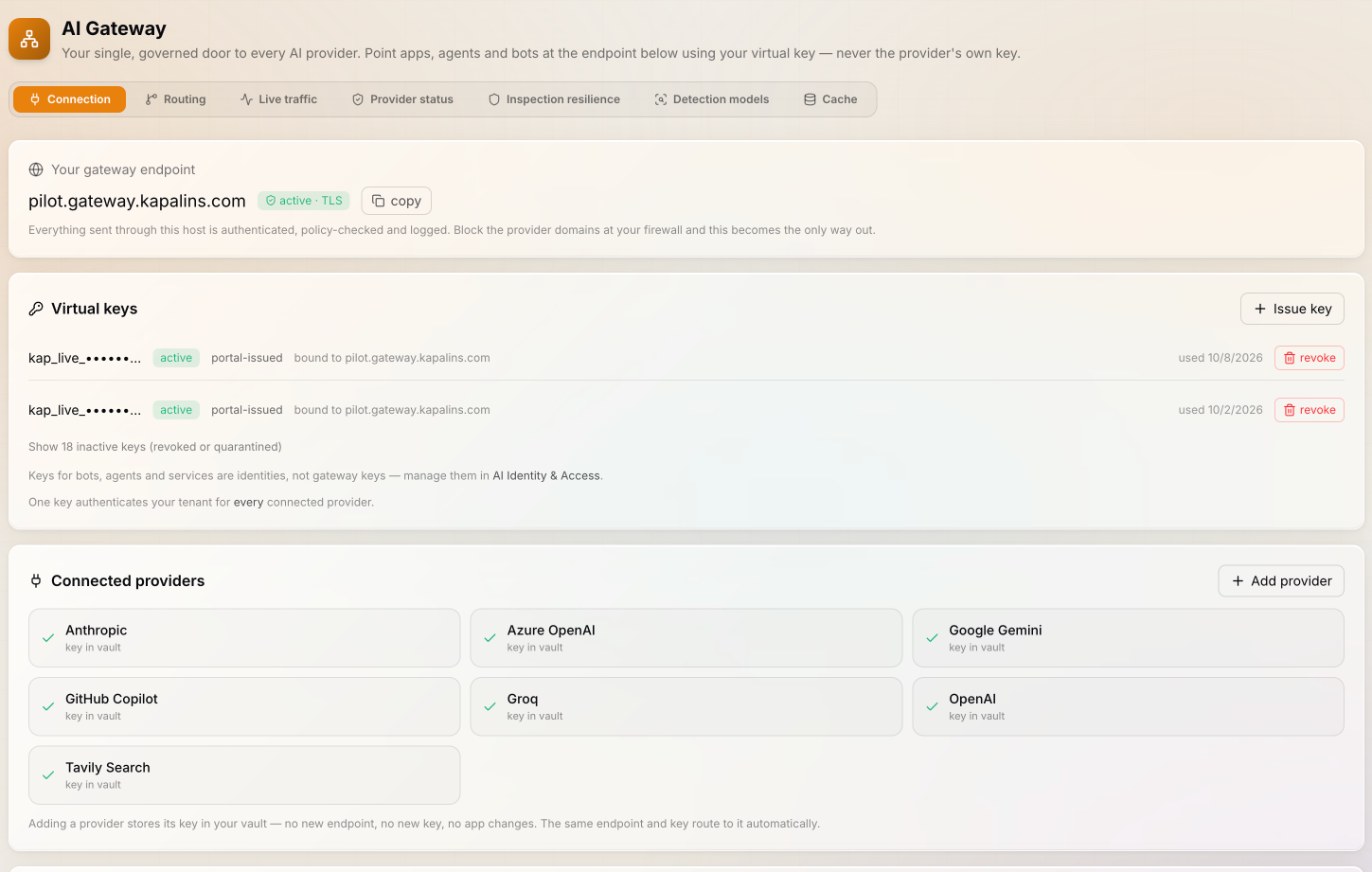
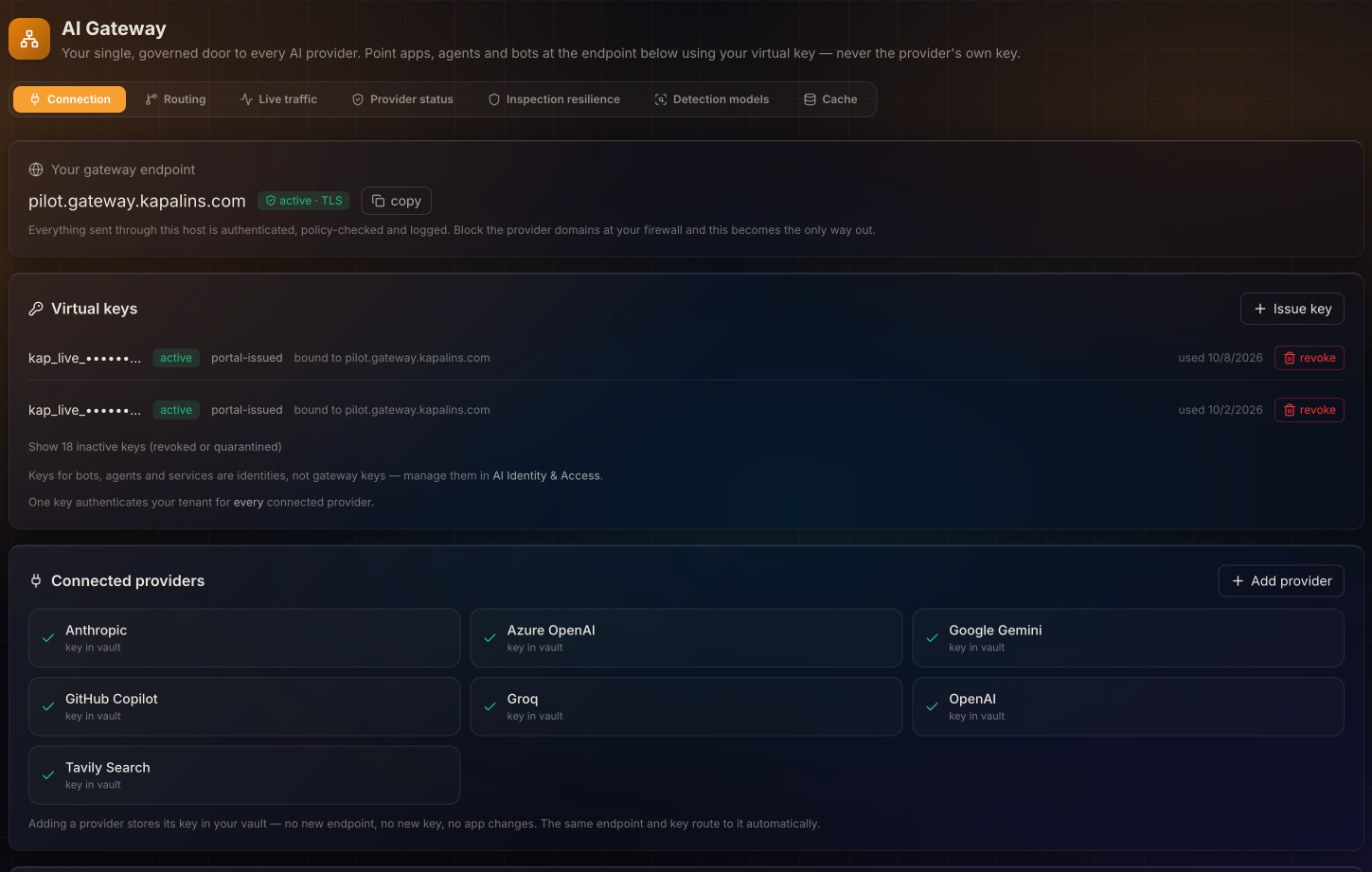
One endpoint, one key, every provider.
Point the application at your gateway host with a virtual key. Kapālins routes to Snowflake Cortex REST API with the key it holds, fails over when Snowflake Cortex REST API is down, and meters every call to the team that made it.
- Your app speaks OpenAI API format
- 2 Snowflake Cortex REST API models priced, so spend lands on a team the same day
- Block the provider domains at your firewall and this becomes the only way out
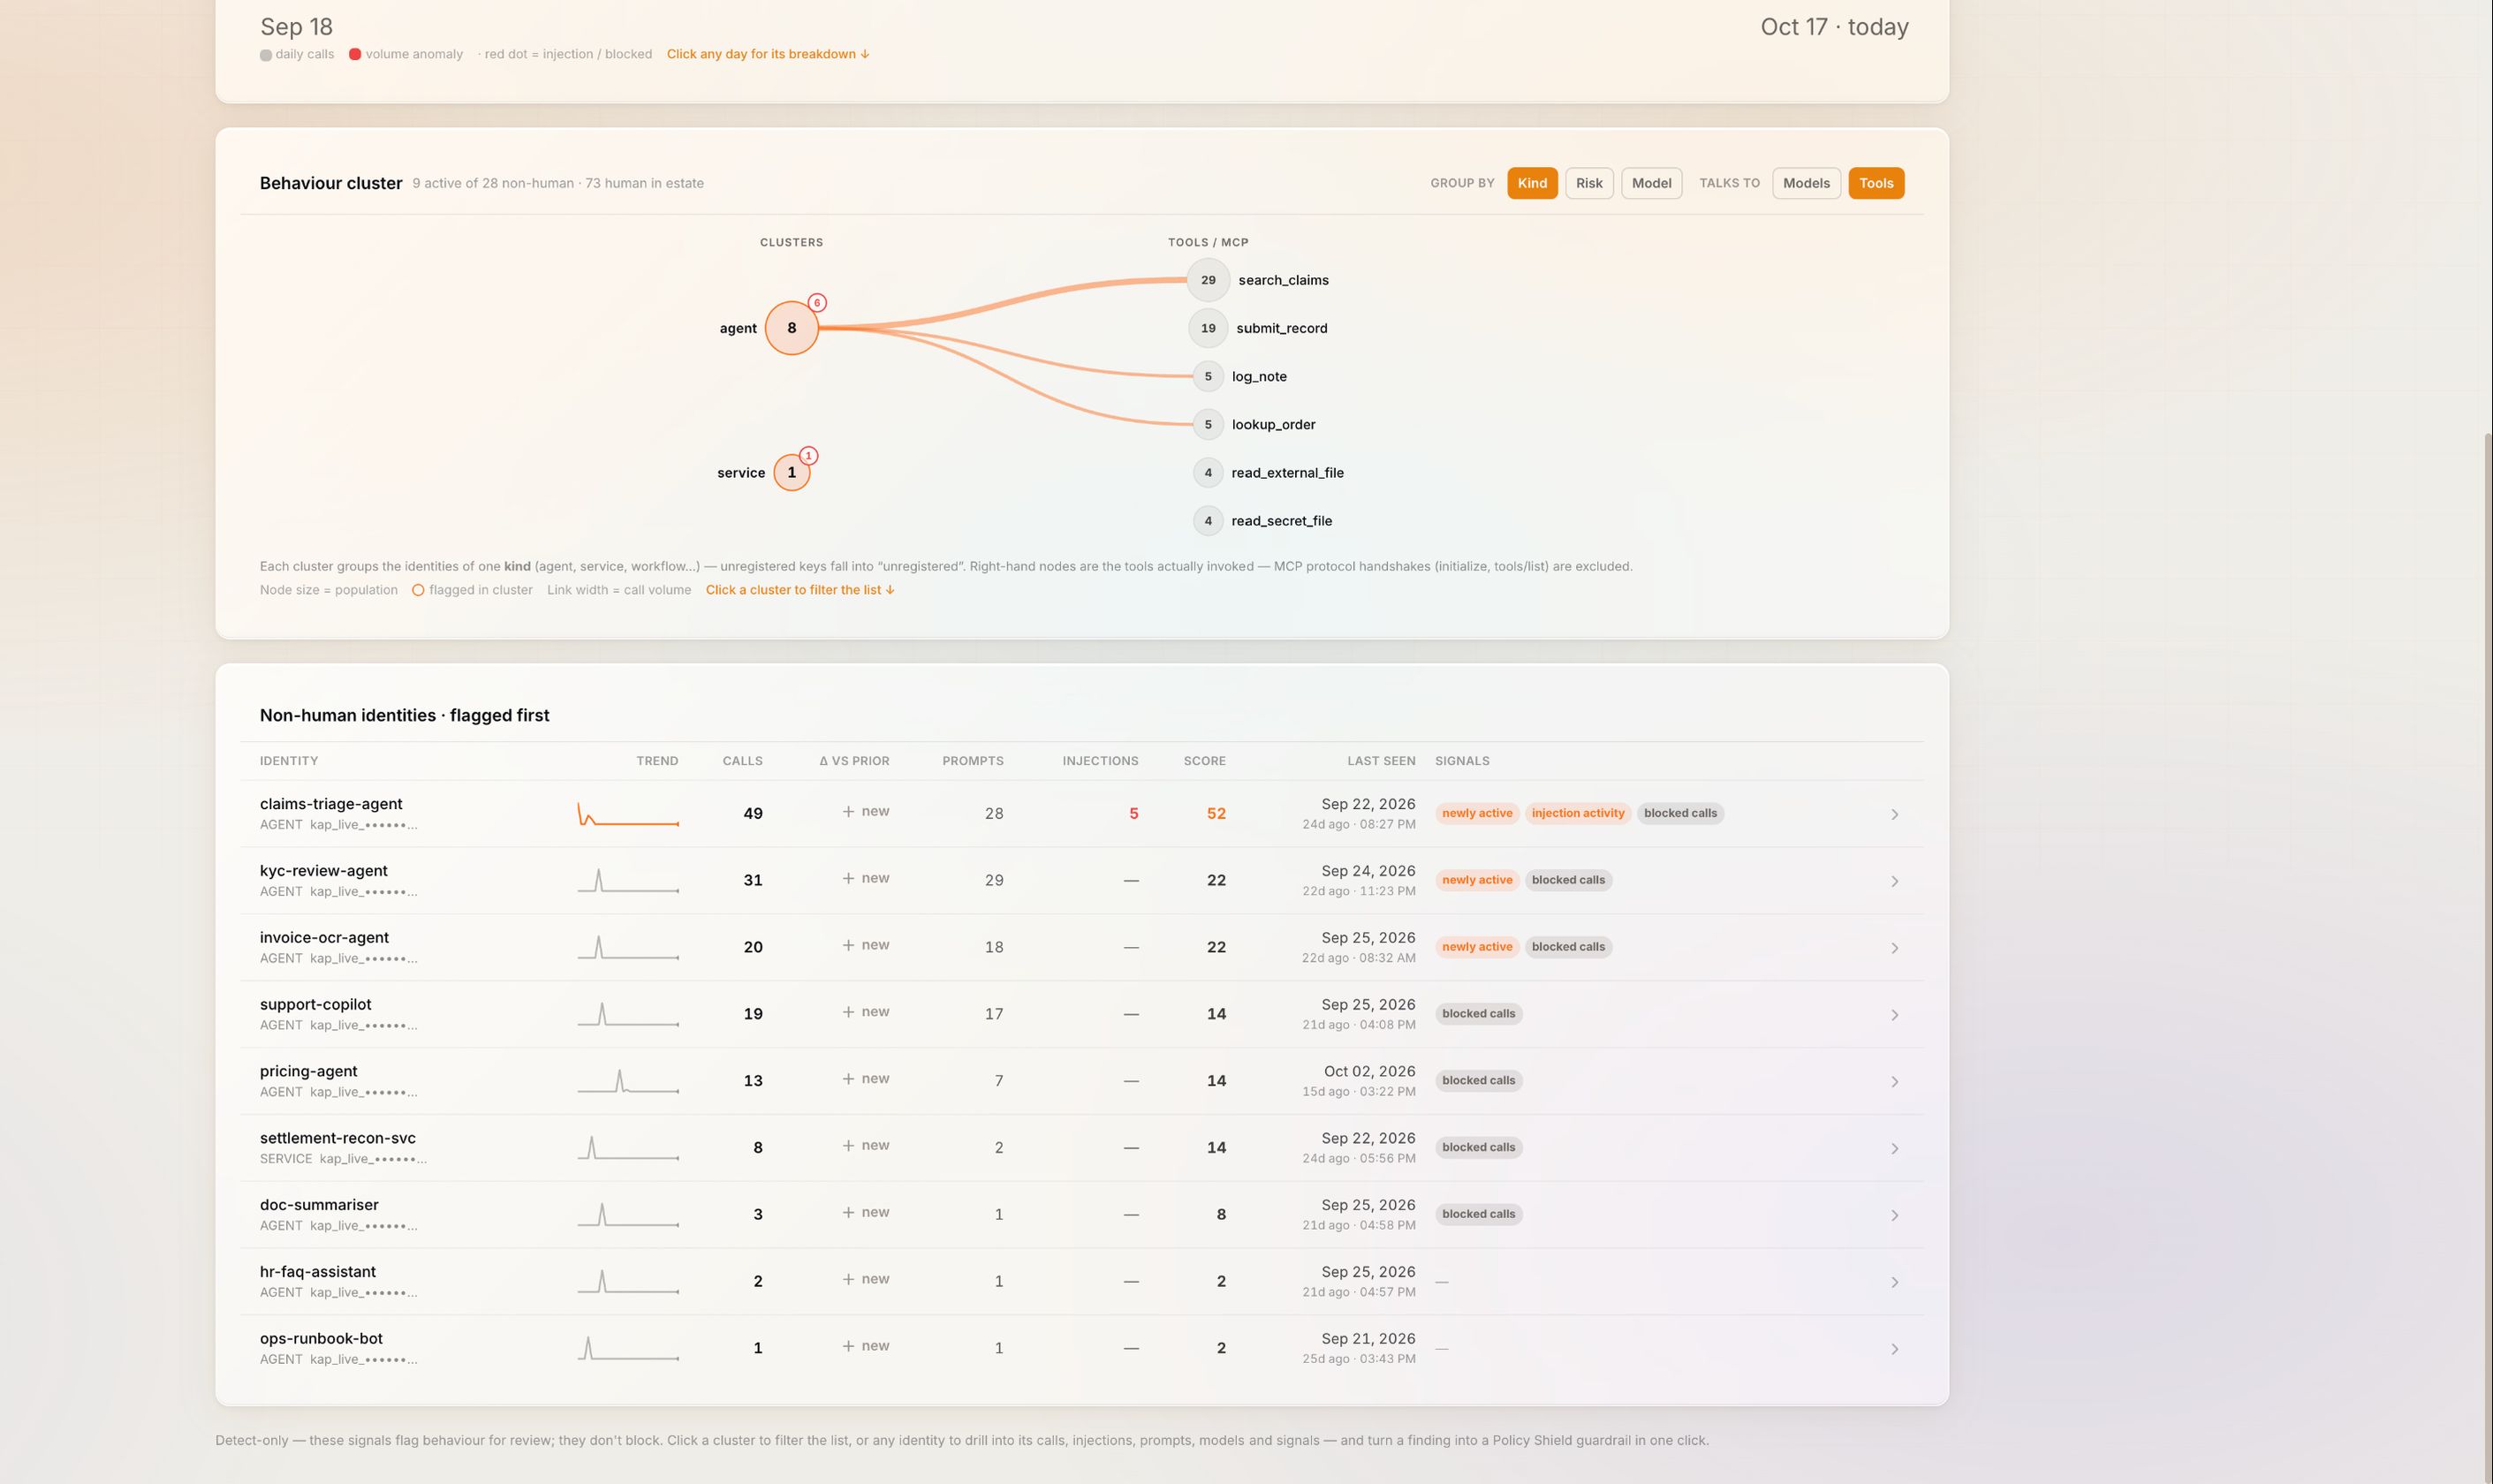
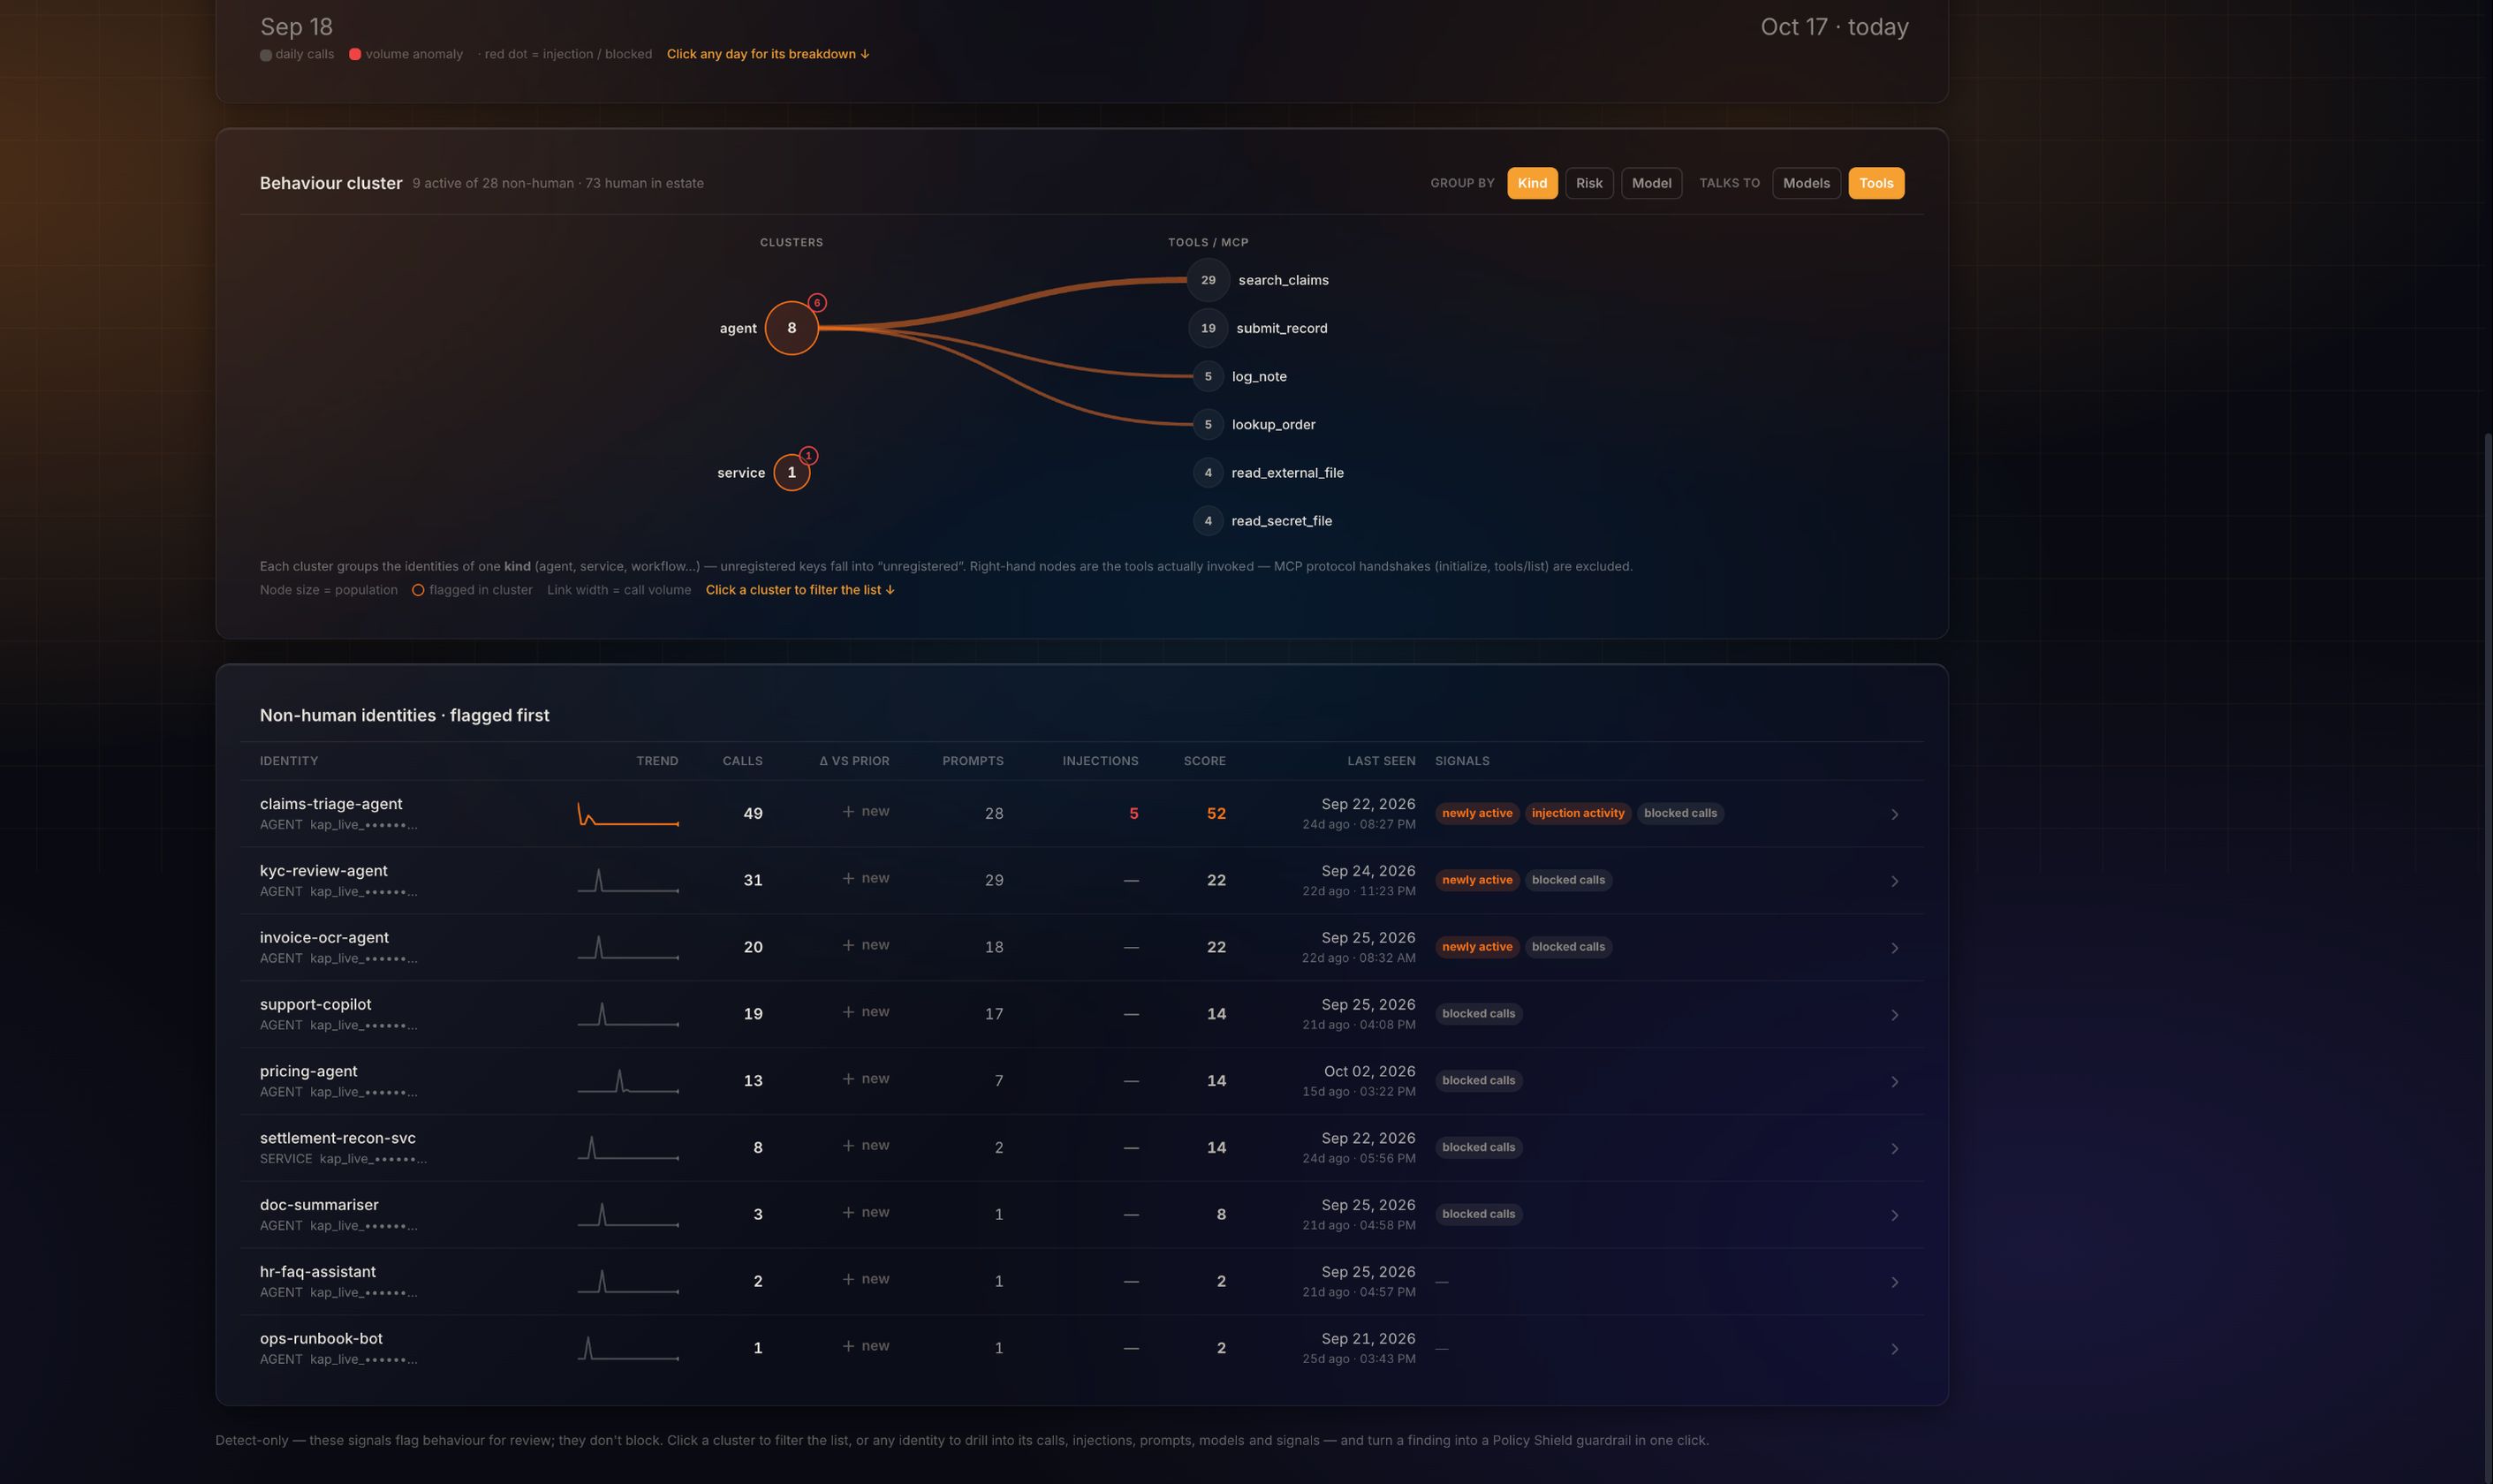
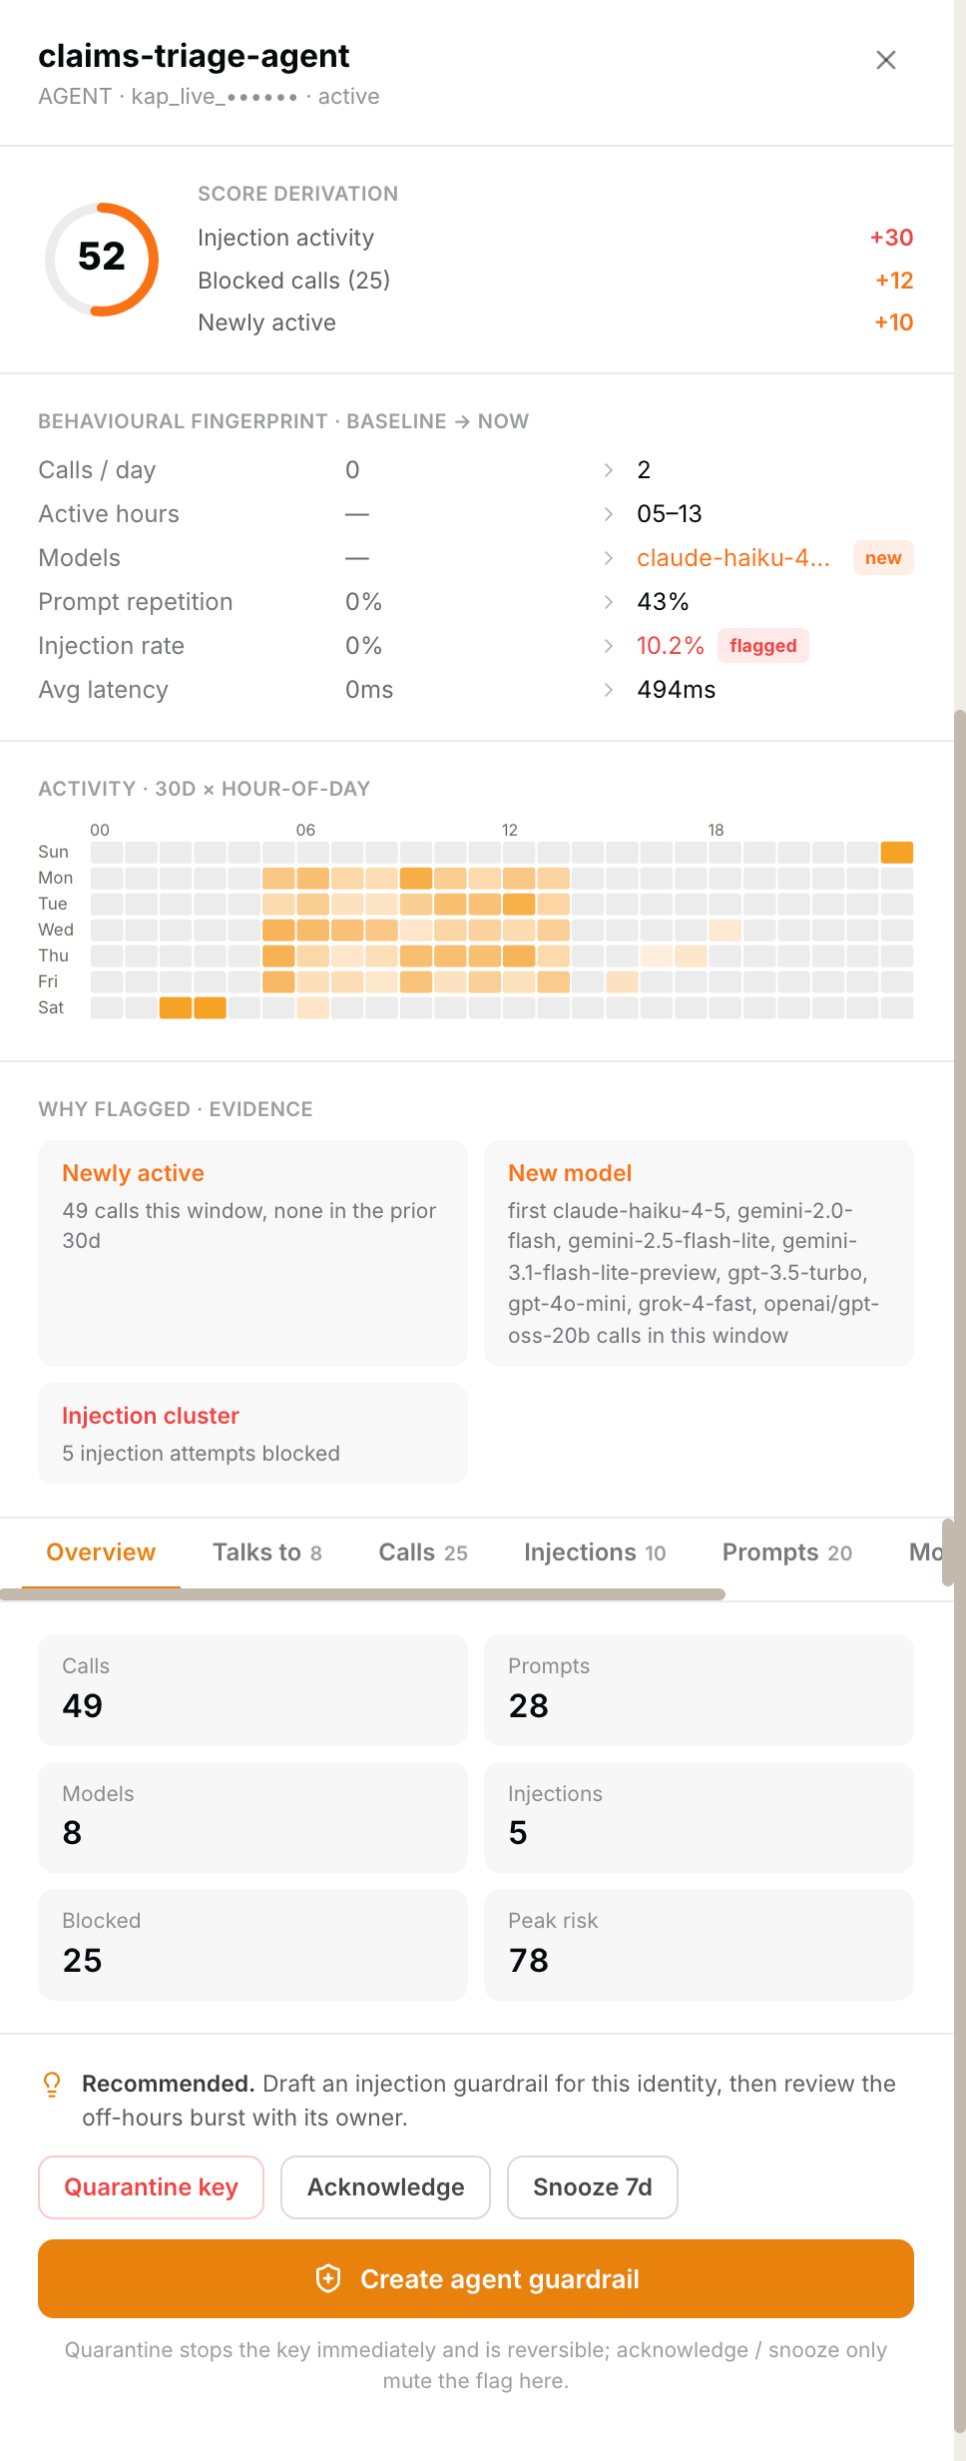
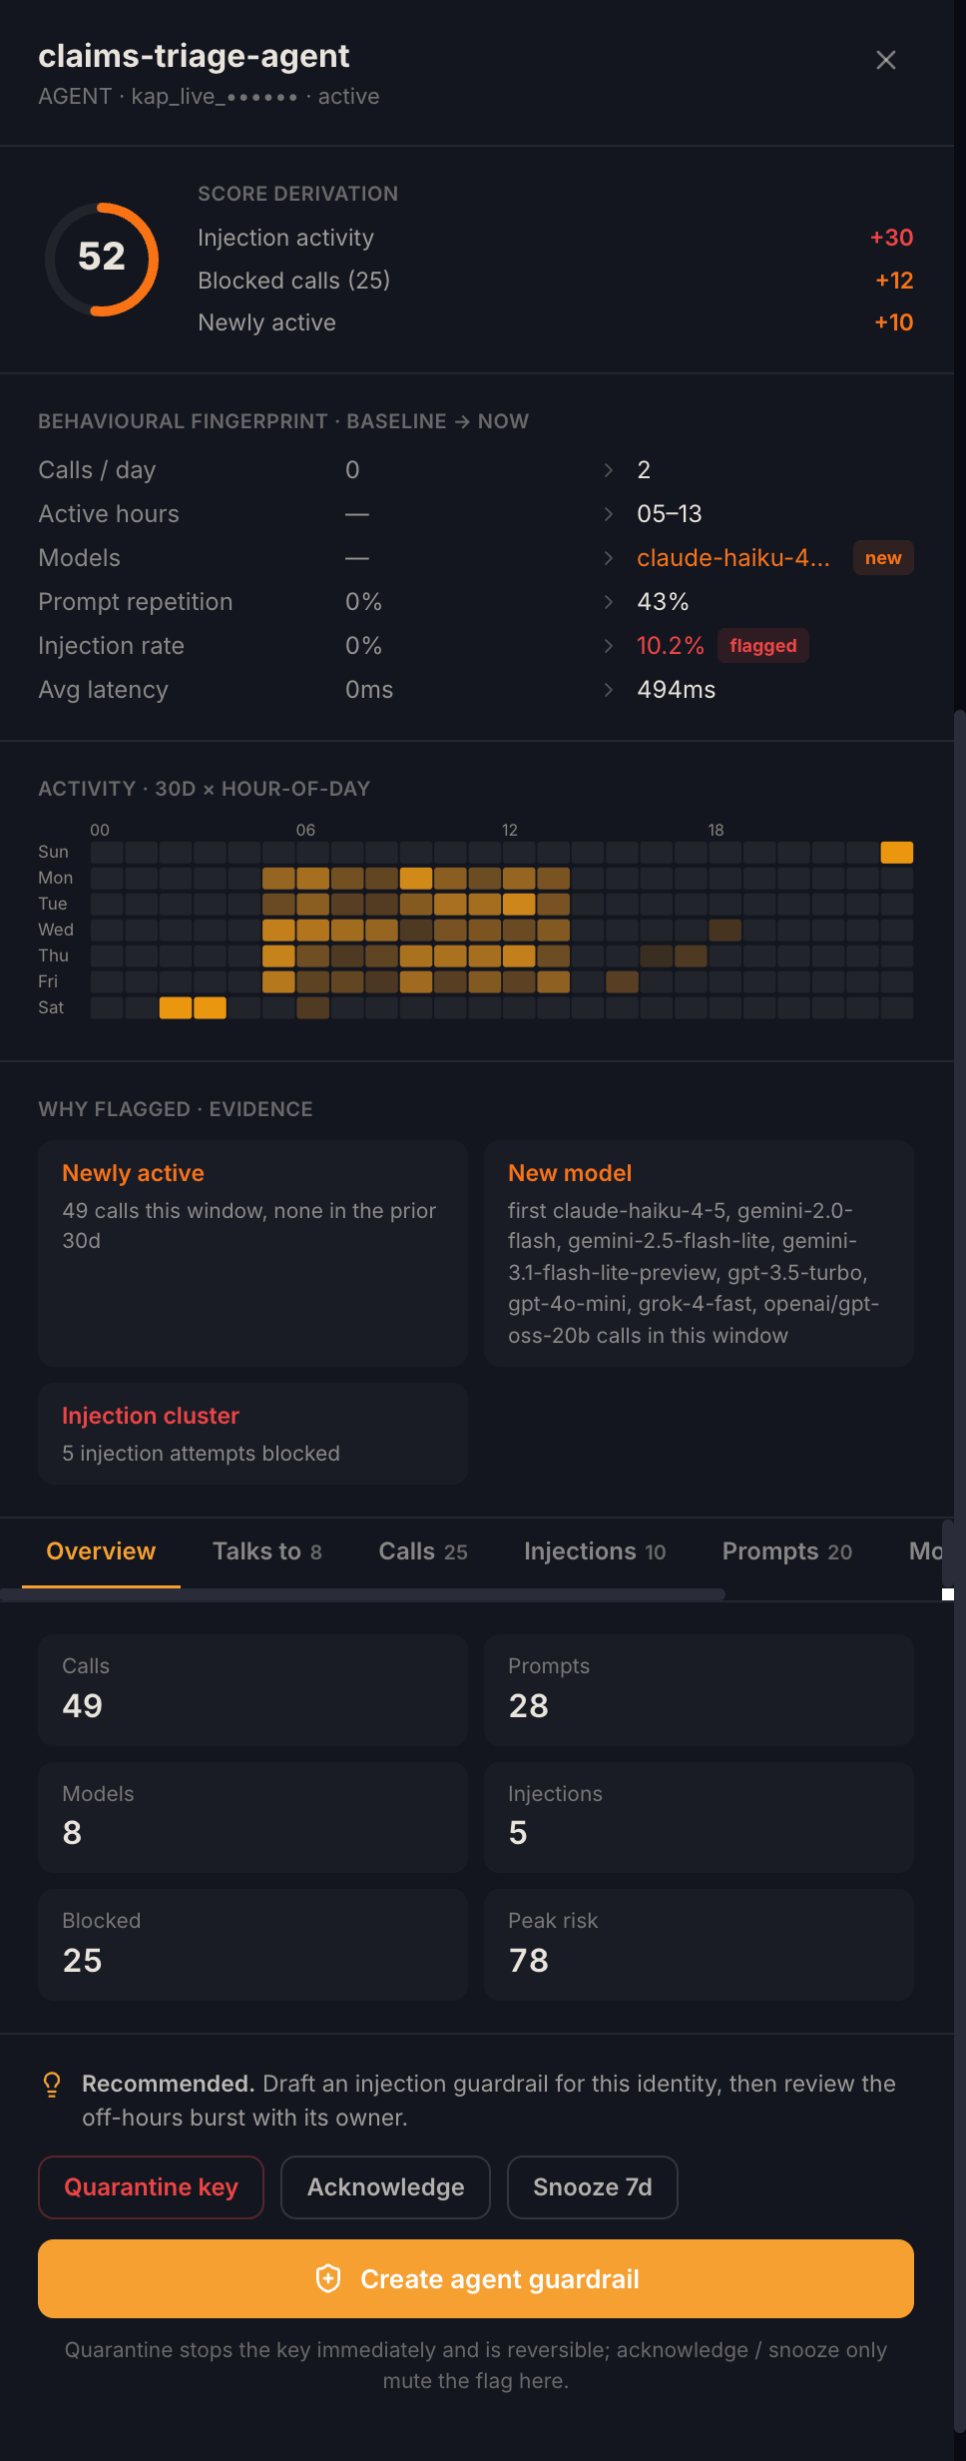
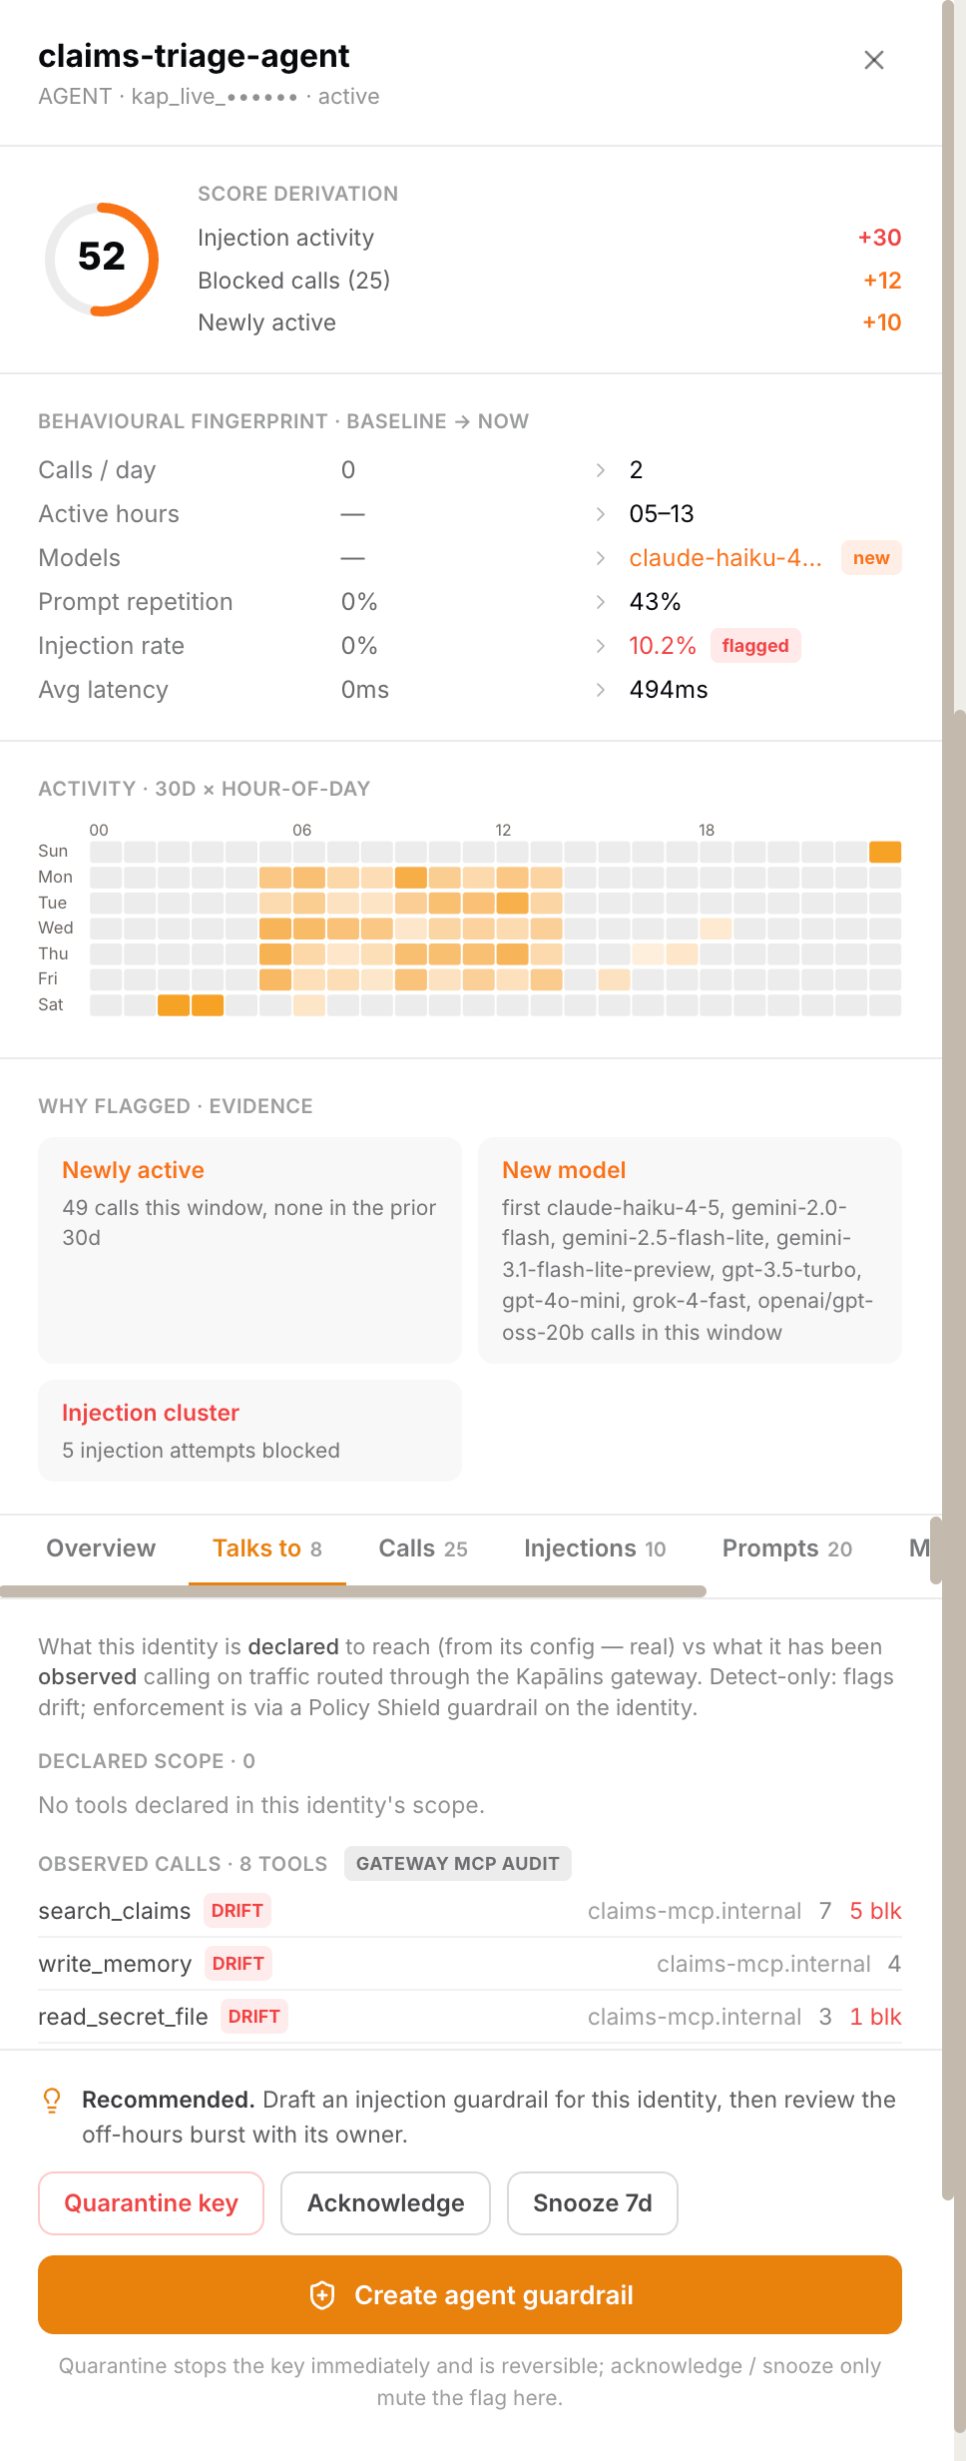
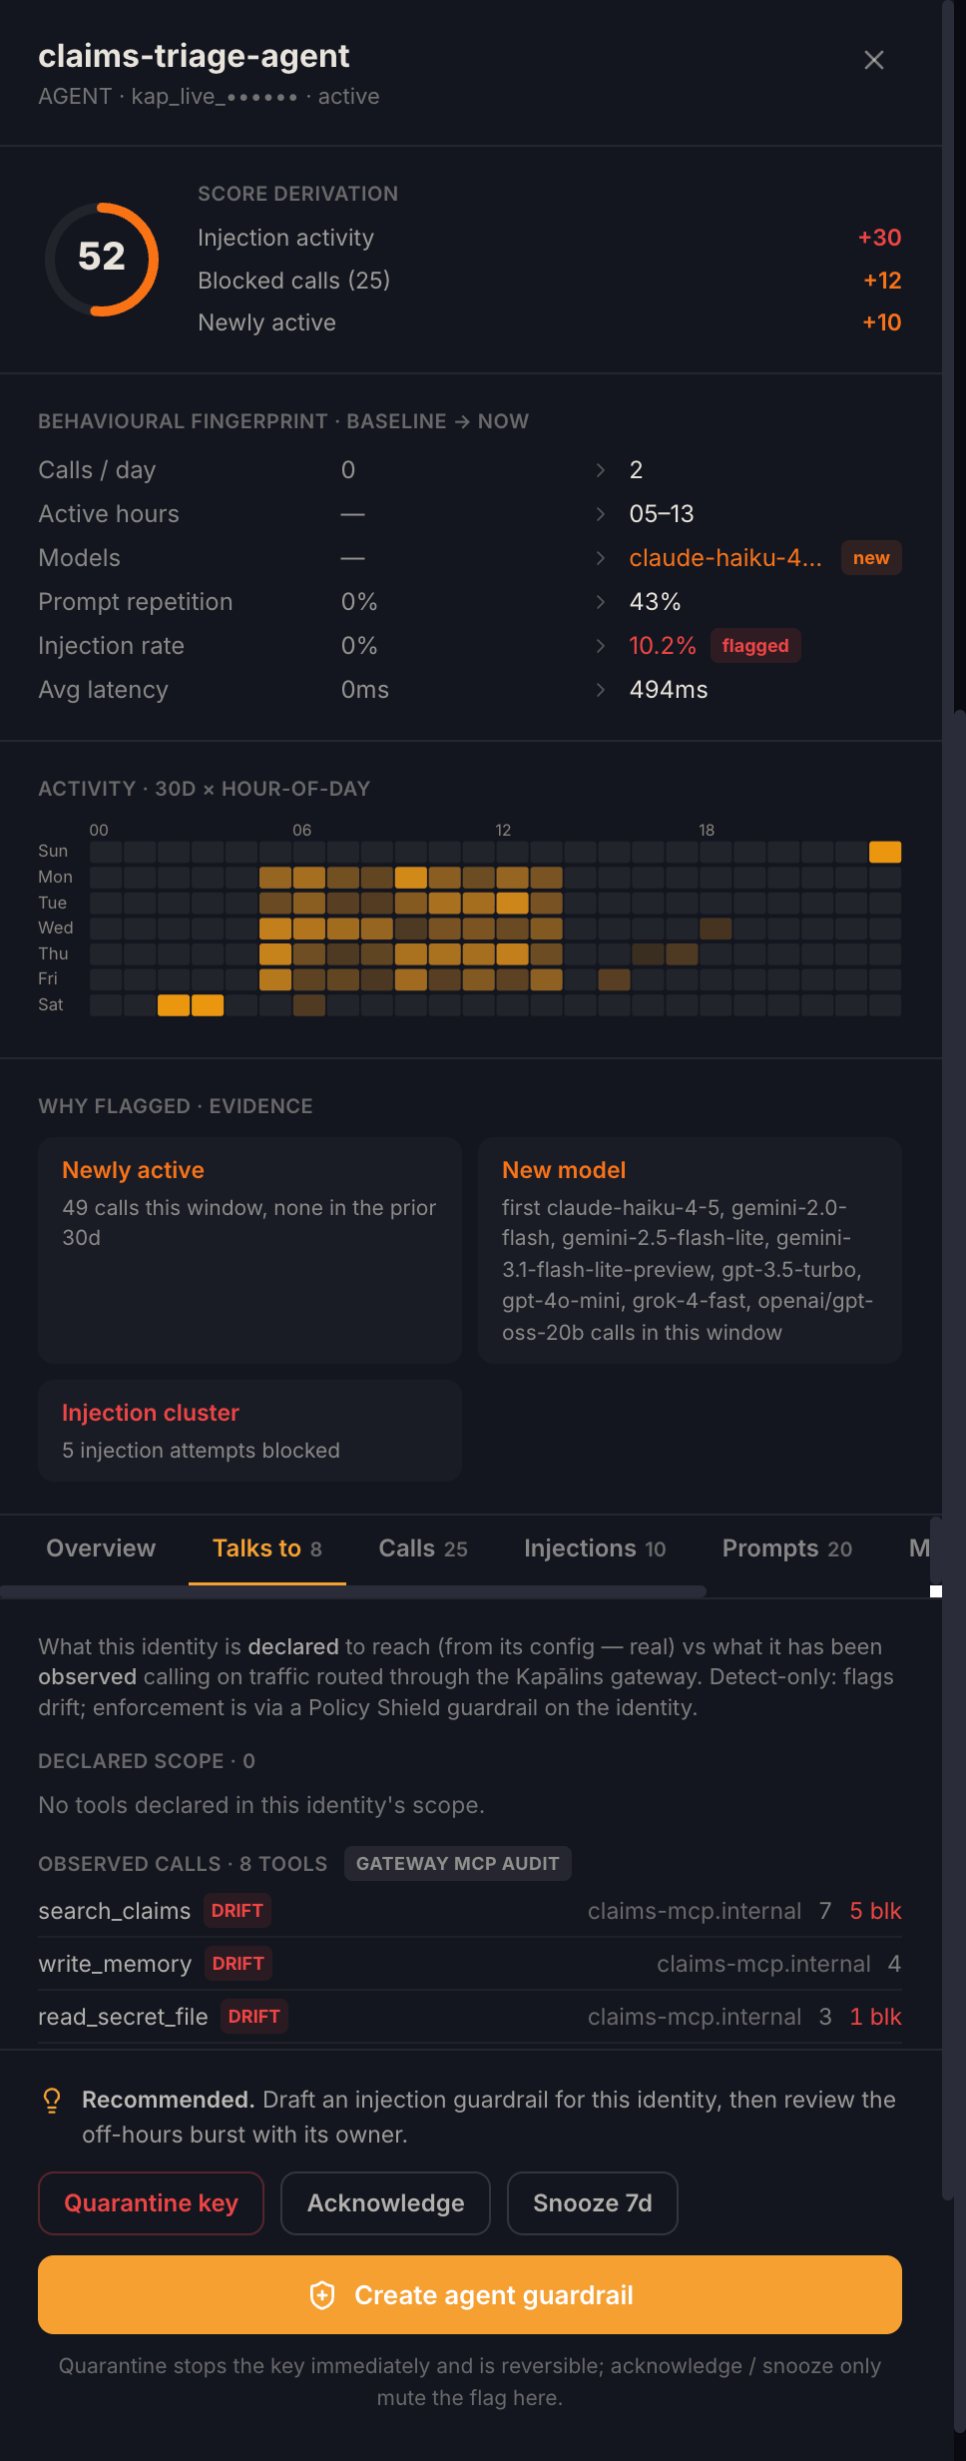
Agents calling Snowflake Cortex REST API, fingerprinted.
Every agent and service key that calls Snowflake Cortex REST API through the gateway gets a behaviour baseline: calls, active hours, models, prompt repetition, injection rate. When one drifts it is flagged with the reasons, and one click drafts a guardrail or quarantines the key.
- The tools and MCP servers each agent actually invoked
- Detect only by default; quarantine is one click and reversible
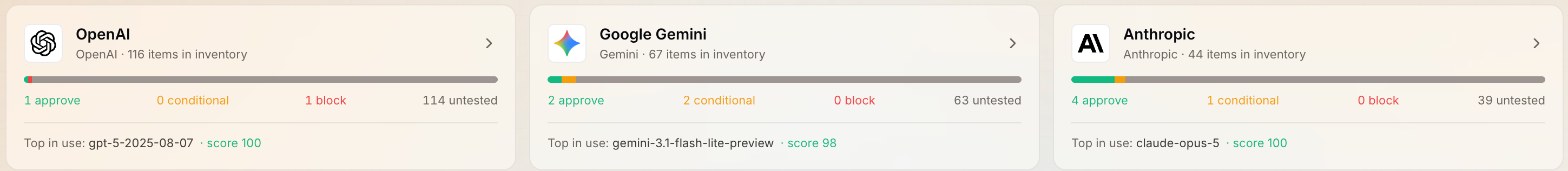
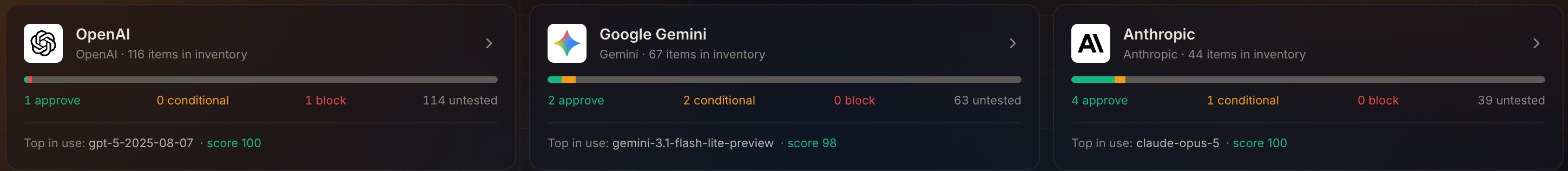
Snowflake Cortex REST API models: approved by a person.
Each Snowflake Cortex REST API model is approved or blocked by a person, with who decided and when. On Growth and Fortress, Policy Shield acts on the verdict at the gateway; on Foundation it records what it would have refused.
- A model nobody has approved is not served by the gateway
Four steps.
- Add the providerIntegrations › Snowflake Cortex REST API › paste the key. Kapālins checks it with a live call, then seals it.
- Issue virtual keysOne per application or agent, each with its own policy, models and budget.
- Change the base URLPoint the application at the gateway. Request and reply formats stay as they are.
- Detect, then enforceEvery shield starts in detect, so nobody is blocked on day one. Enforcing needs the AI gateway at Protect; below it, the gateway records what it would have blocked.
See Snowflake Cortex REST API governed in thirty minutes.
Bring the person who holds the credential. We connect it live and watch the first events land.
Questions buyers ask.
Does the gateway add latency to Snowflake Cortex REST API calls?
Policy Shield runs in the request path. Each family can be set to detect only, and the gateway reports its own added time per call in the timeline.
Do my applications need code changes?
A base URL and a key. The gateway accepts the OpenAI and Anthropic formats, so request and response handling stay as they are.
Can Snowflake Cortex REST API be governed without the gateway?
Routing is what makes inline control possible. AI that cannot be routed, such as hosted copilots, is governed from its audit logs, identity grants and the device sensor instead.